



Introduction
The disruption we’re witnessing isn’t because of a new threat category. It is the industrialization of conventional ones.
Cybercrime went corporate years ago: affiliate programs, Ransomware-as-a-Service (RaaS), Initial Access Brokers (IABs), support desks on underground portals. AI did not start that but what it did was collapse the cost and the skill floor of every stage of the attack at the same time.
Attacks did get smarter, but the part most underestimate is that mediocre attackers became competent, and competent ones became industrial.
Now that the cybercriminal economy has automated its traditional bottlenecks, defense requires two immediate pivots:
- Pre-exploit infrastructure tracking is essential: AI executes attacks at the speed that renders reactive defenses incompetent, making early infrastructure visibility and pre-exploit blocking your strongest shield.
- Cyber-fraud convergence is critical: AI enables threat actors to seamlessly blend technical network breaches with financial scams using the exact same underground ecosystem.
Automation of labor: Attacks orchestrated in less than the price of a coffee
When a capability holds an up-for-grabs market price, it has separated from the skill that used to build it. Anyone can buy it.
Think about where the leverage actually lands. The exploit was never the expensive part but human expertise: writing a convincing lure in a language you do not speak, running reconnaissance on thousands of targets, holding a persona together for weeks inside a romance or business email scam.
Those are exactly the tasks a language model is good at. So the automated lead generation and the synthetic identity kit that arrives ready to use.
Now look at the list. A deepfake toolkit sells for $5. Automated fake video bots run on Telegram at roughly $13 dollars. Pre verified business accounts, real identity attached and live payment rails included, sell for $300 to $700 dollars each.
One ransomware operation Group-IB investigated kept a browsable inventory of 14,700 pre-compromised devices and 969 validated VPN credentials, stocked for affiliates like a wholesaler’s shelf. These are commodity prices, and commodity pricing is the definition of industrial. The person who breaks in and the person who profits are now different businesses, trading through a market in between.
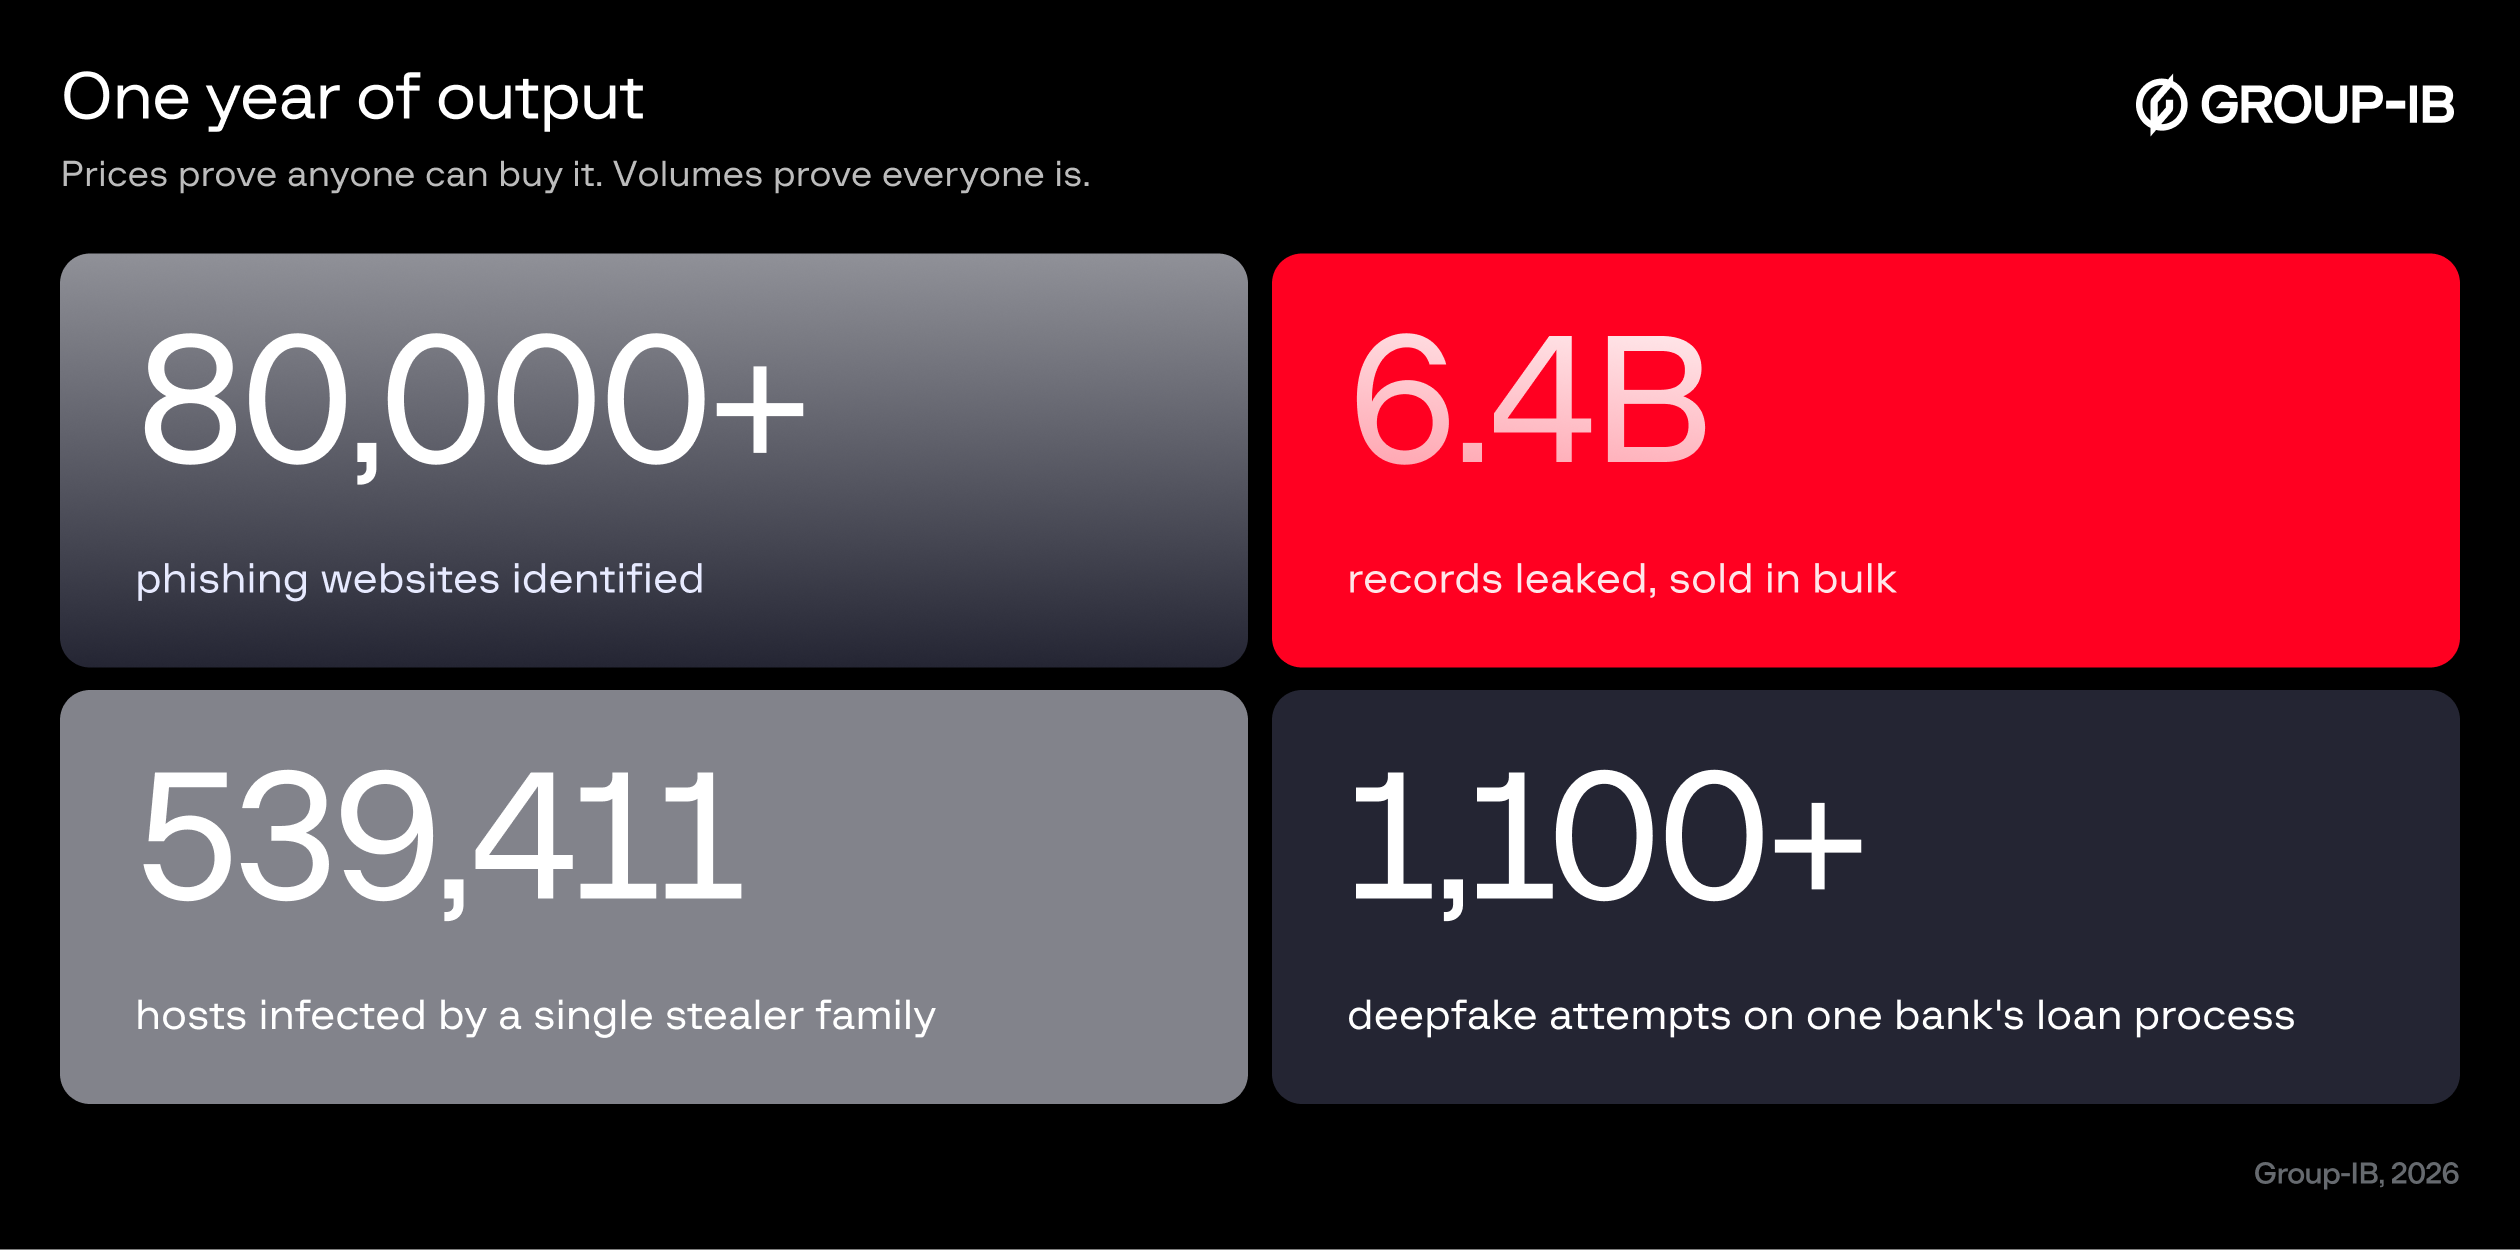
Scale is the second proof. These are single year, single source figures. The true totals are larger.
Modern cybercrime is a company now, and modern fraud is the same company
For most of this field’s history, how sophisticated an attacker was and how much damage they could do moved together. The as a service economy severs that line. The person who runs a campaign and the person who built the capability are now different people, and the operator needs almost no technical skill at all.
That is the deepest thing happening here: skill has been decoupled from impact.
What we’re facing is a market that behaves like a software company: a developer tier builds the platforms, a distribution tier resells access, and a large base of low-skill customers runs campaigns off a subscription.
The orchestration is corporate: support channels on Telegram, tiered pricing, free trials, uptime guarantees, and reputation systems that punish sellers who cheat other criminals. Take one platform down and demand does not evaporate; it migrates to a competitor within weeks, because the customers still exist and the market rushes to serve them.
You are not up against a hacker. You are up against a market, and markets do not get arrested. Map any single operation honestly and an org chart draws itself ; a job in every box you would recognize from any firm.
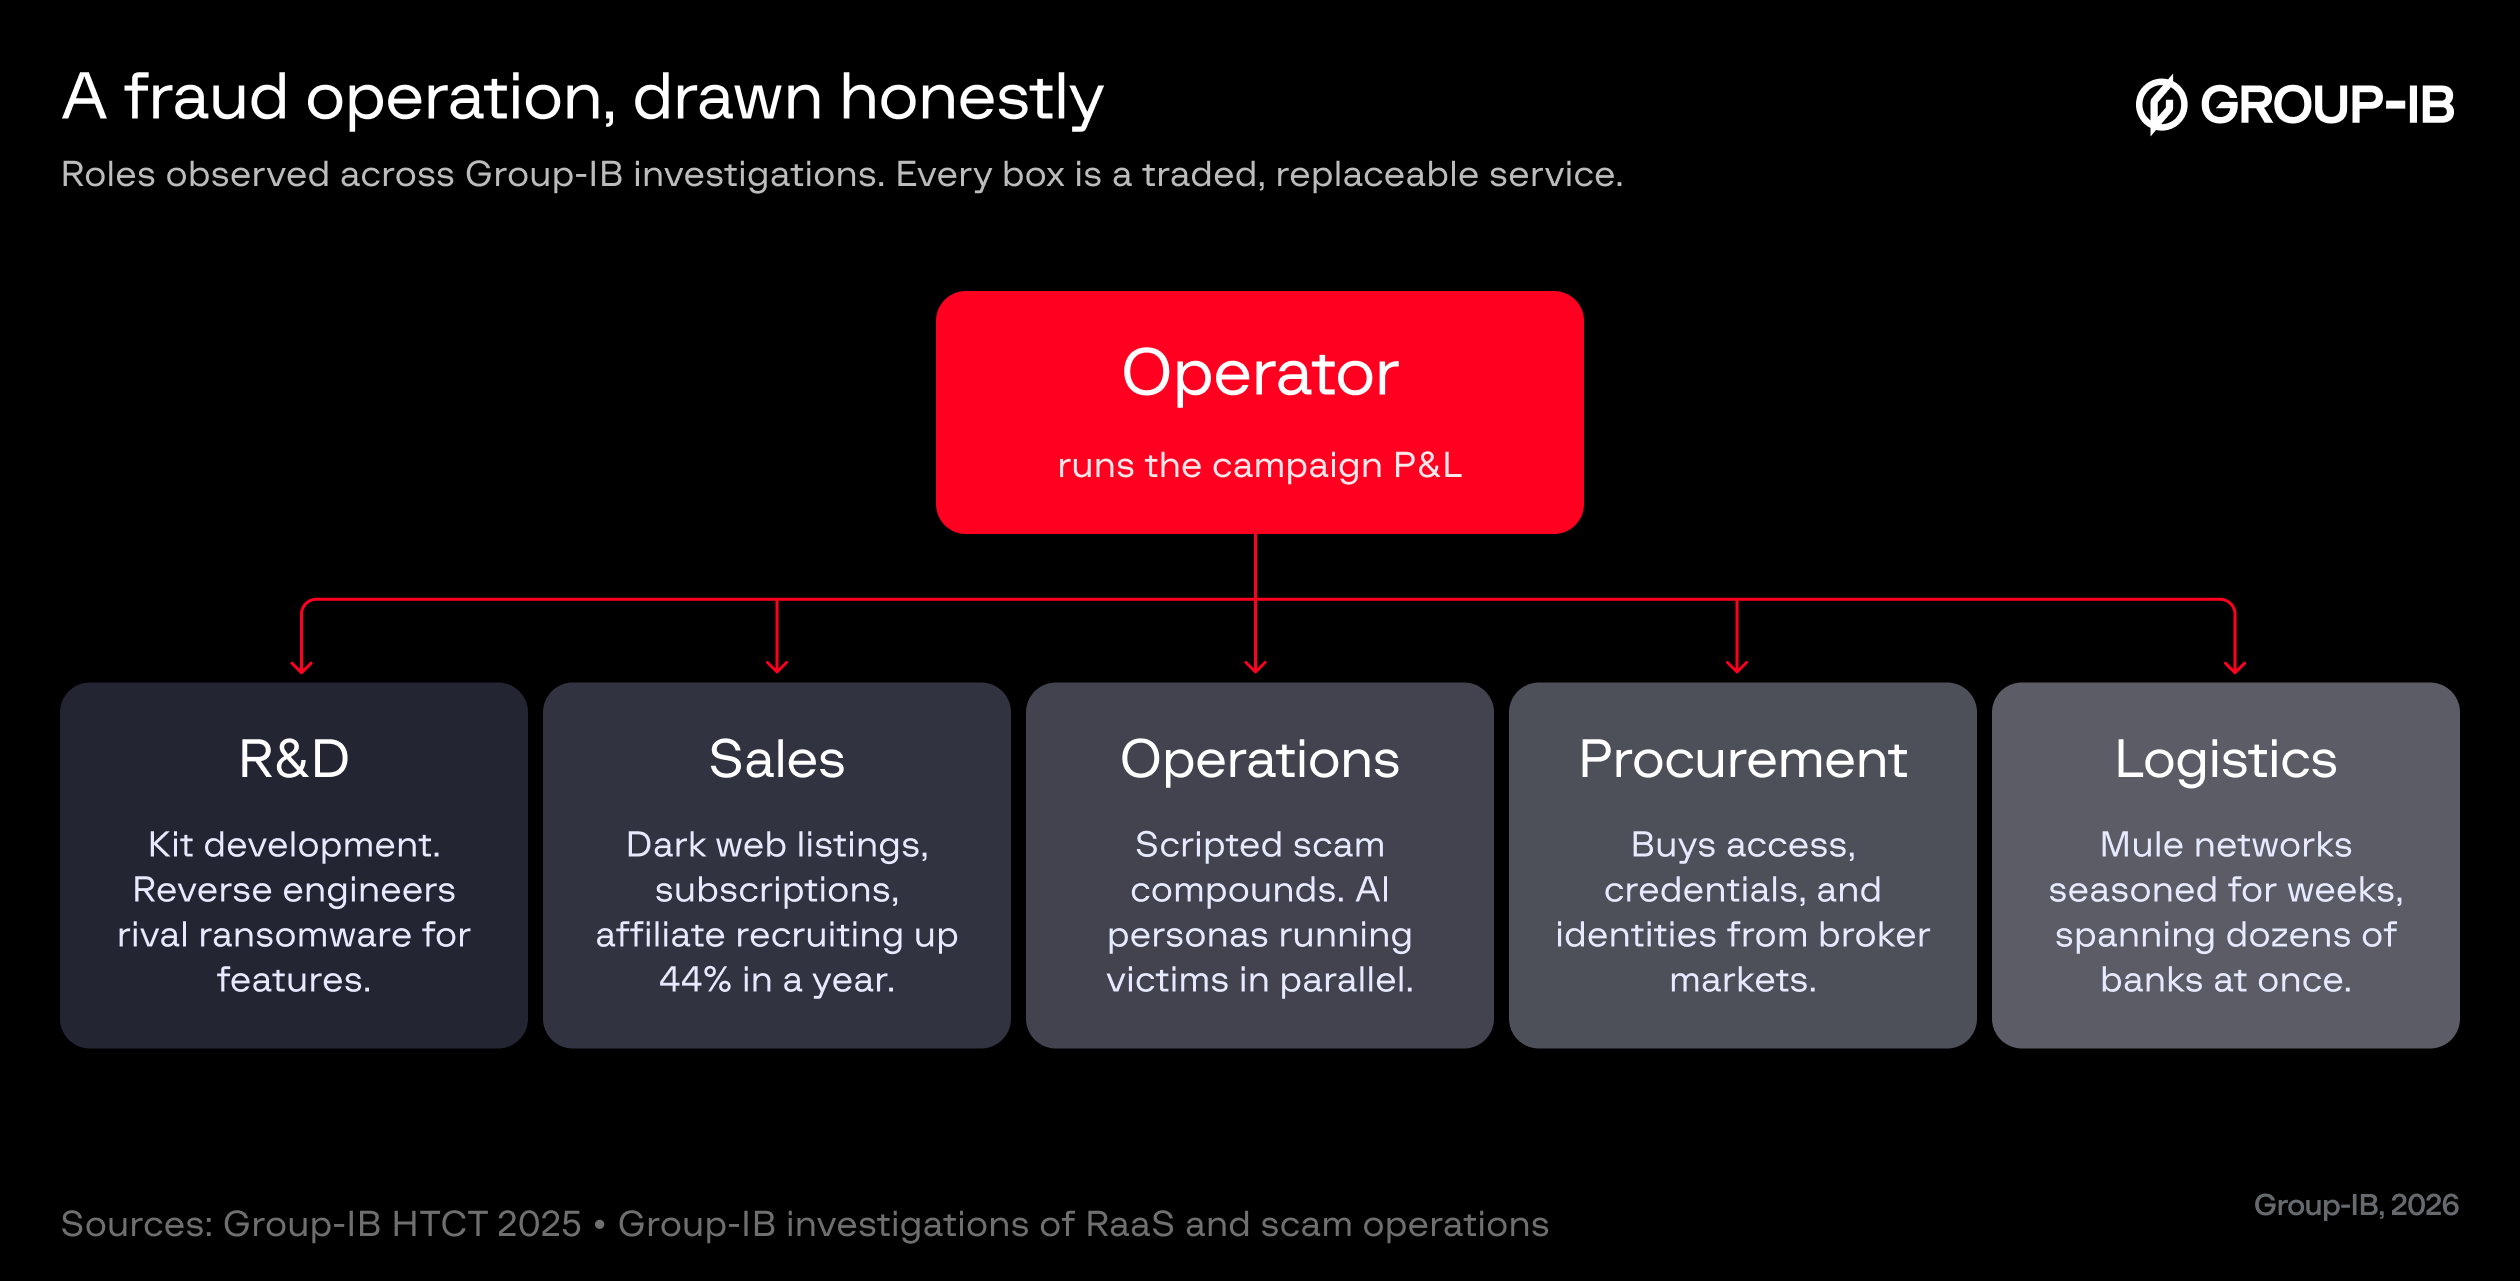
Image: If your defense assumes a lone attacker, you are defending against the wrong organization.
That company does not employ its departments, it rents them from the market, assembled on demand and dissolved when the job is done.
Attackers outsource their entire operating model: Instead of building custom tools or running end-to-end operations, syndicate leaders rent specialized departments straight off the dark market:
- Procurement: Buys pre-stolen logins and device footprints from stealer log markets (RedLine, Lumma, Vidar, Raccoon).
- R&D and Operations: Subscribes to ready-made phishing kits and rents AI-powered OTP bots to manipulate victims into giving up two-factor codes live on the phone.
- Logistics and Sales: Rents pre-seasoned money-mule networks to wash cash and runs affiliate programs, like the $64 million Classiscam model, where freelance scammers take a 20 to 30 percent commission per hit.
Defense must intercept the supply chain, not just the intruder: Because attackers assemble their operations out of standardized, off-the-shelf components, defenders cannot wait to detect a breach after it happens. Continuous scouring of the dark market is needed and that is what Group-IB Threat intelligence tracks – it ingest stealer logs and credential dumps as they surface, matching exposed data against your monitored identities and assets so compromised logins are blocked at the front door before access is granted.
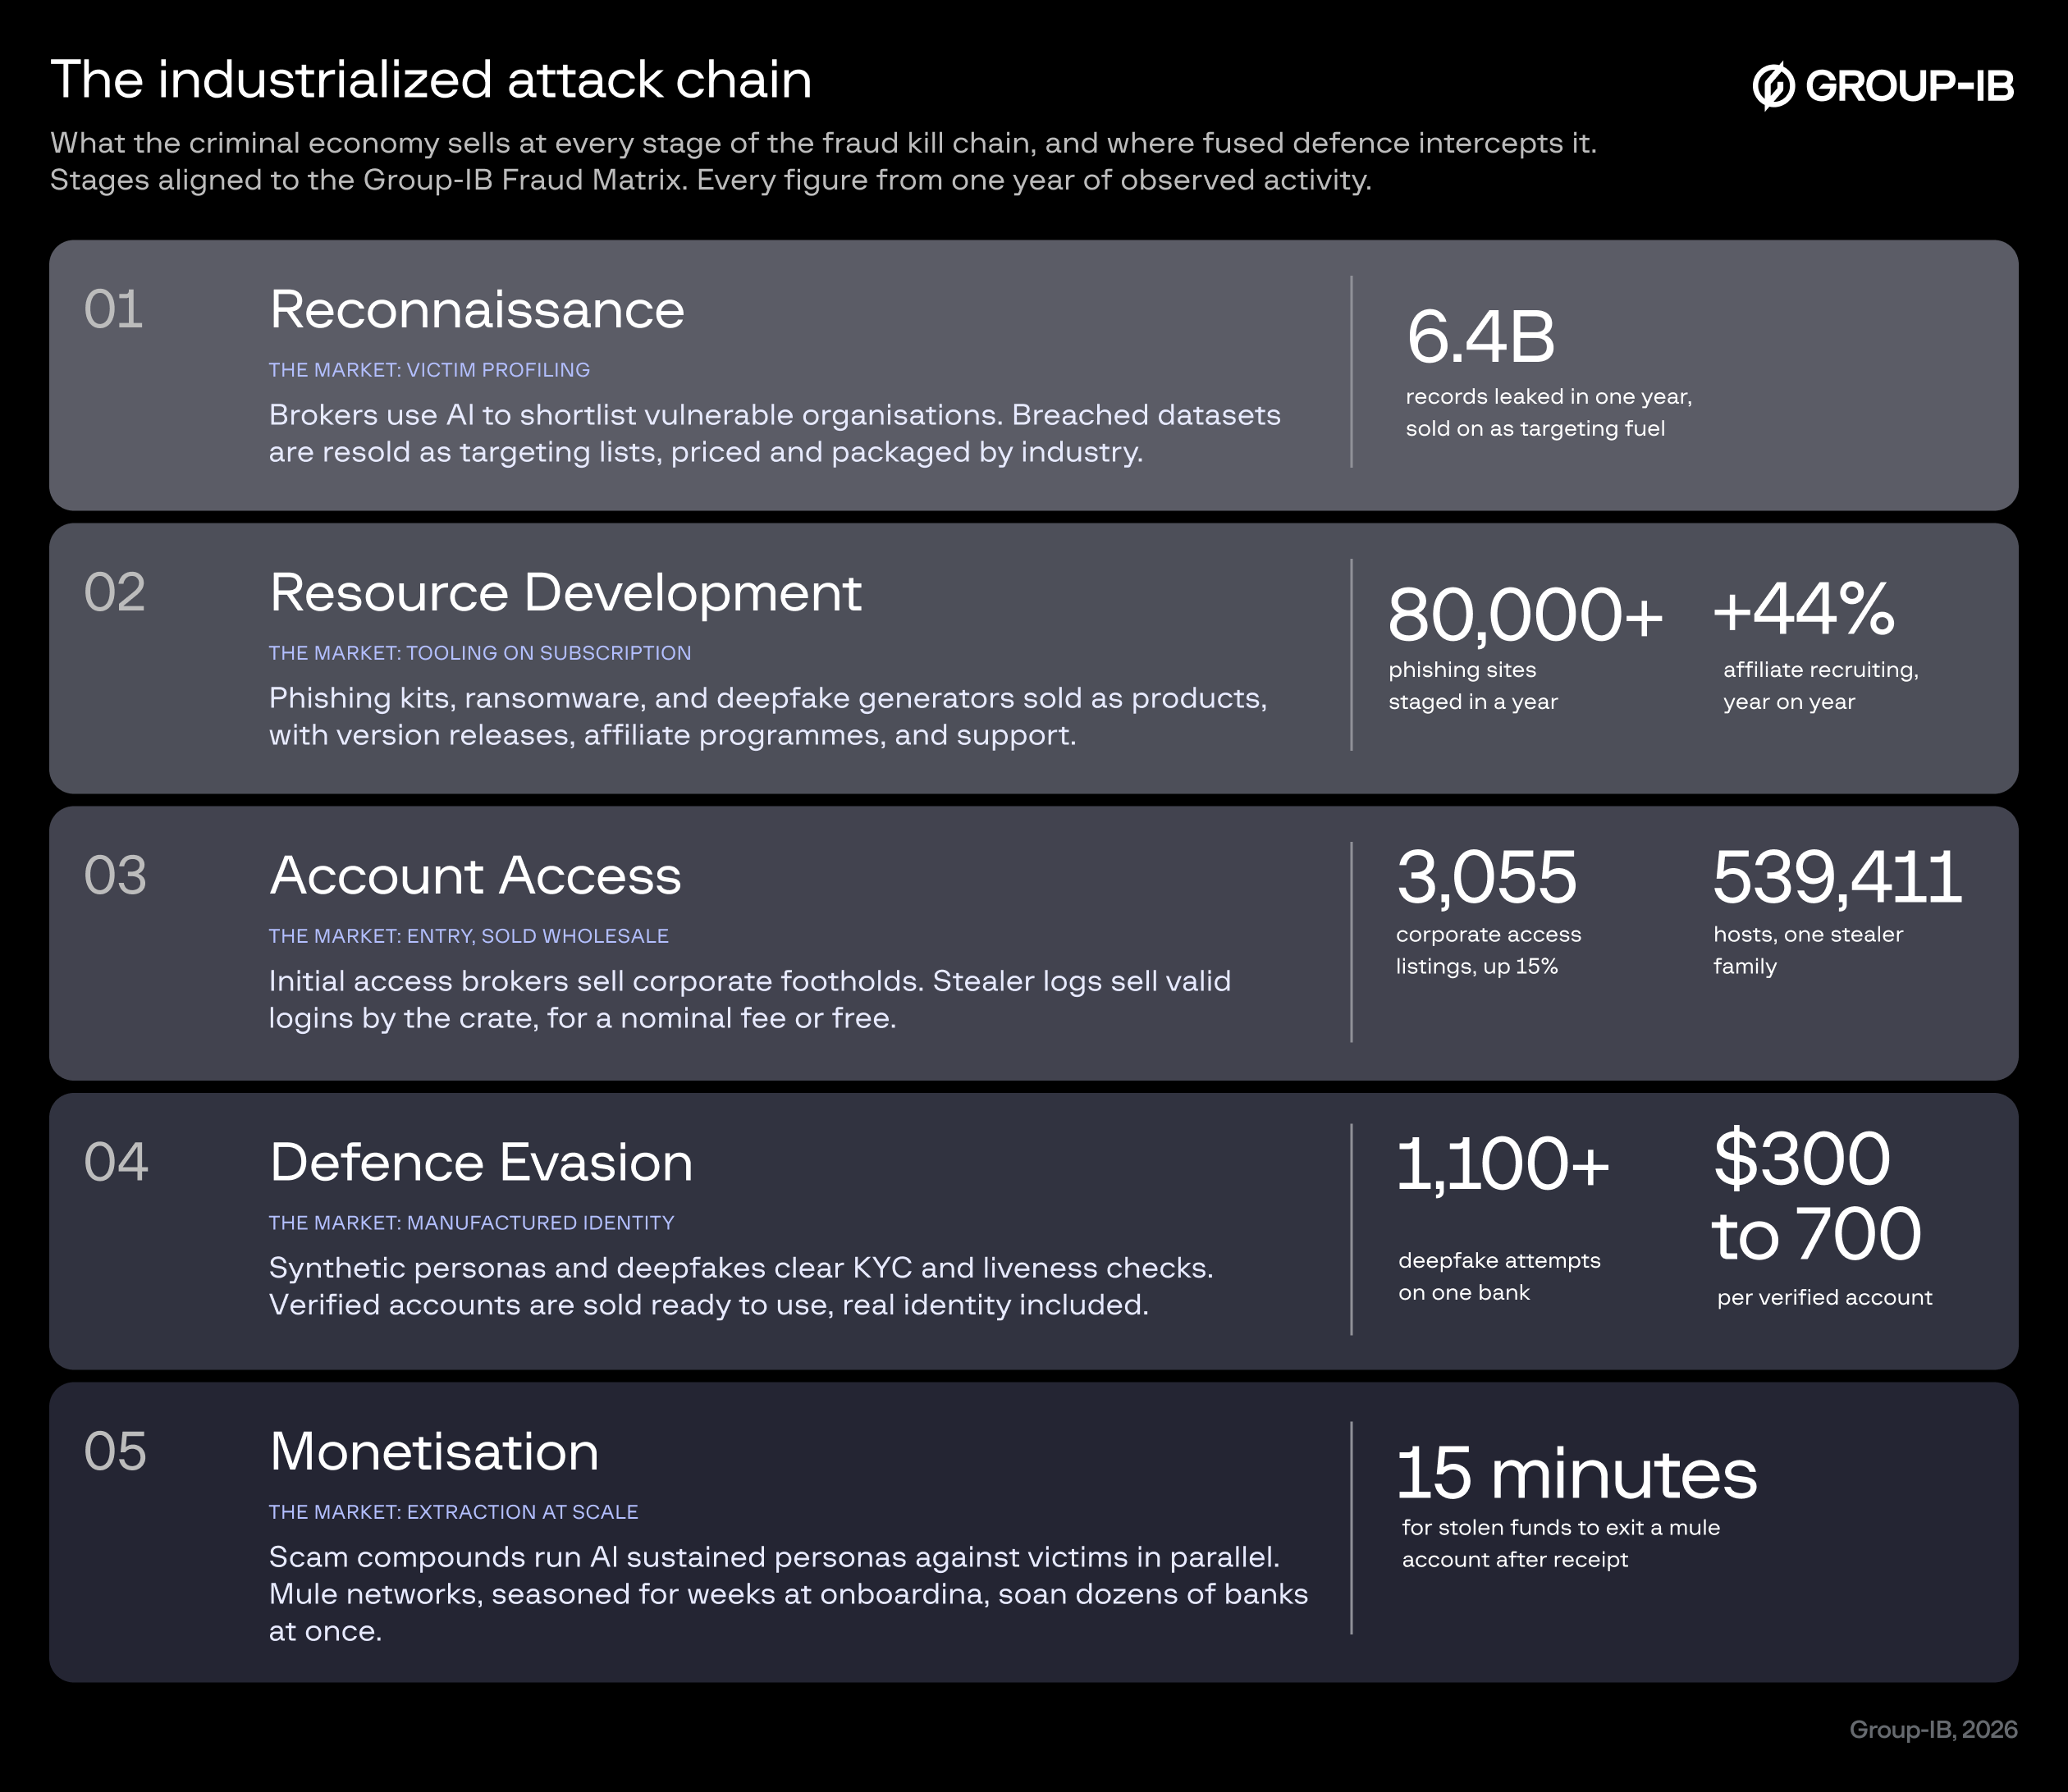
What the criminal economy sells at every stage of the attack, and where fused defense intercepts it. Every figure is a single year, single source. The true totals are larger.
What gets industrialized keeps climbing toward what you trust
Watch what the market manufactures and it keeps moving in one direction. Access became a wholesale listing: 3,055 corporate footholds sold in a year, up 15 percent. Credentials became a bulk commodity: 6.4 billion records leaked, stealer logs sold by the crate. Then identities became products, manufactured whole.
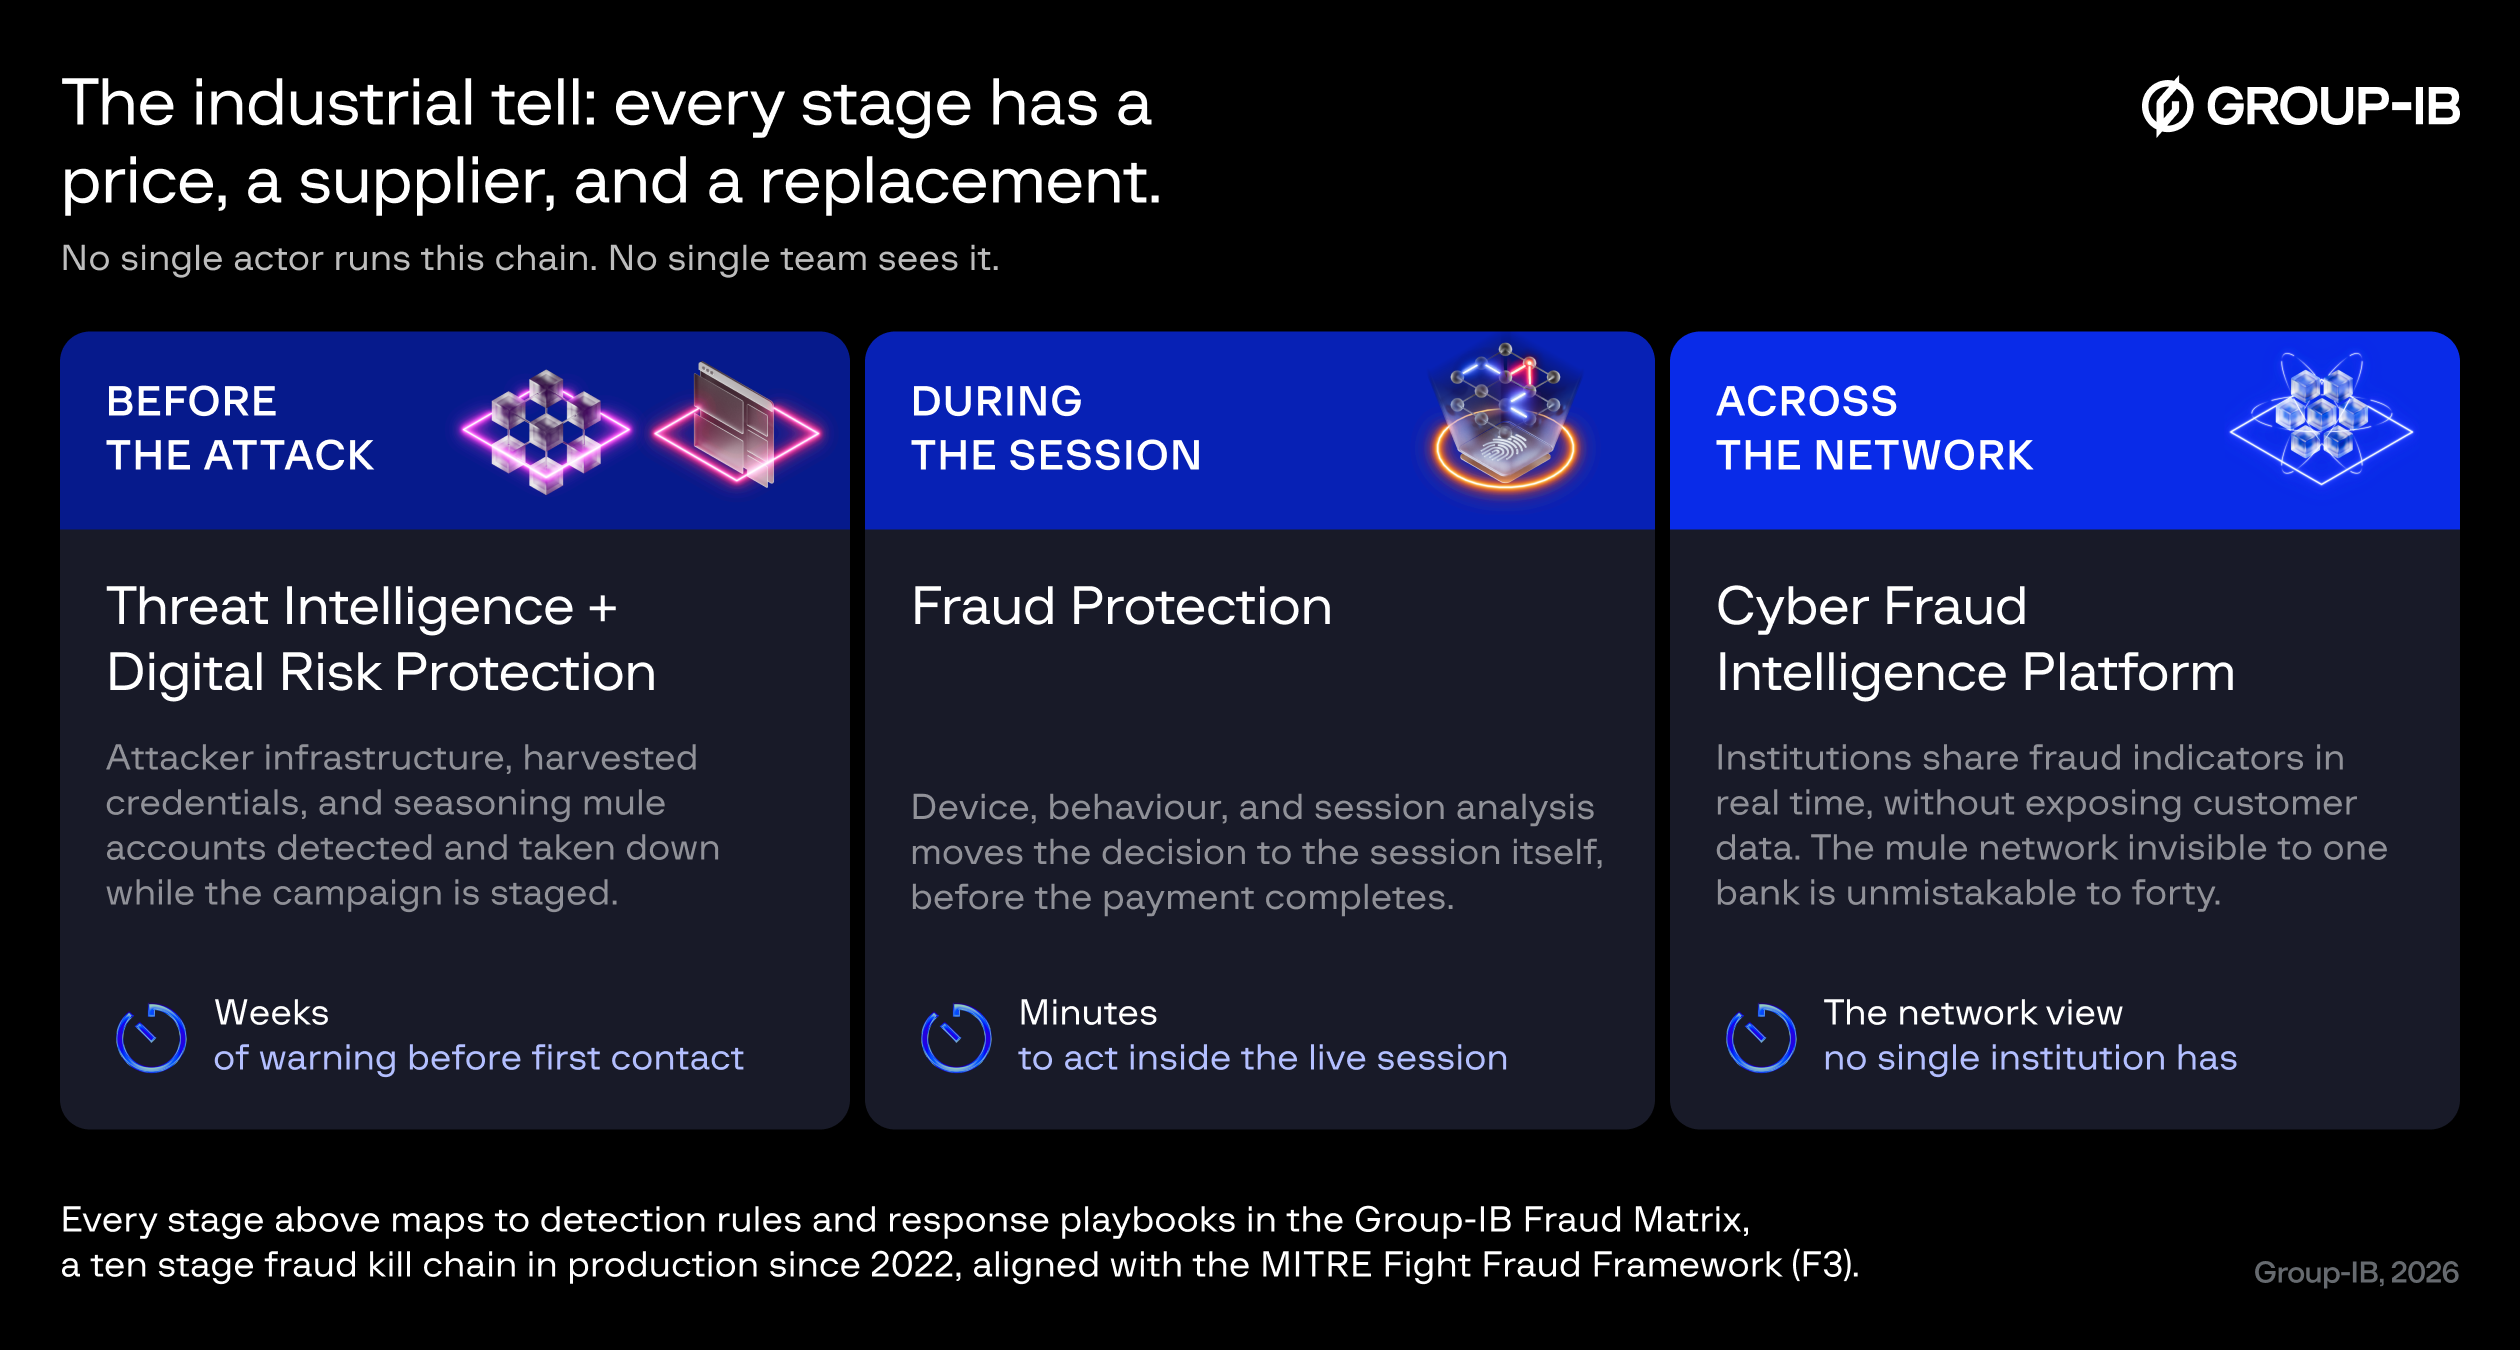
The direction of travel is the finding. Every rung moves the attack further from breaking in and closer to being believed.
The security perimeter is dead. Attackers are no longer breaking into systems; they are inheriting the access you willingly grant to legitimate users, vendors, and service accounts — and the ladder shows exactly how they get there.
Identity hijacking has replaced system hacking: Attackers don’t bypass identity checks; they trick real victims into completing the liveness scans and multi-factor checks for them. Once validated, the attacker takes over the session, localizes the device, and sells the authentic, fully verified account on the dark web. The identical loophole that lets a fake customer through onboarding lets a fake employee past HR.
A supply chain attack doesn’t breach your defenses; it breaches a vendor you already decided to trust: When you install a software update, you push the attacker’s code directly past your own security. Through stolen OAuth tokens, API keys, and service accounts, intruders ride valid credentials through trusted integrations without triggering a single intrusion alert.
When Scattered Spider went after financial institutions, they did not attack banks. They compromised a platform the banks trusted, abusing OAuth tokens through third party integrations, and reached hundreds of institutions without triggering an intrusion alert. Nothing was broken. The access was legitimate everywhere it travelled.
Contain the blast radius when trust itself is compromised: You cannot defend a build pipeline you don’t own or inspect software dependencies four layers deep. Because initial entry cannot be fully prevented, survival depends on controlling the damage:
- Refuse Standing Access: Strip away persistent, always-on permissions for any account outside your direct control.
- Watch the Update Channels: Monitor the silent software pipelines pushing code to your machines, as they represent your highest-risk asset.
- Treat Trust as Variable: Realize that initial validation proves nothing about who controls the session five minutes later.
An industrialized adversary needs an industrialized defense
Follow any chain here end to end and the hinge is the same. A credential or a manufactured identity carries the compromise from the cyber side of the house to the fraud side. In most institutions those two ends are watched by teams that never compare notes, on different tools, under different executives. The adversary lives in the space between them, and that space is exactly what got industrialized.
Group-IB does not leave the gap to imagination. By estimates, close to a month passes between the first malware signal and the moment the fraud team is even aware of it, and over that window the number of joint investigation sessions between the two teams is typically zero. That is not an edge case. It is the architectural default.
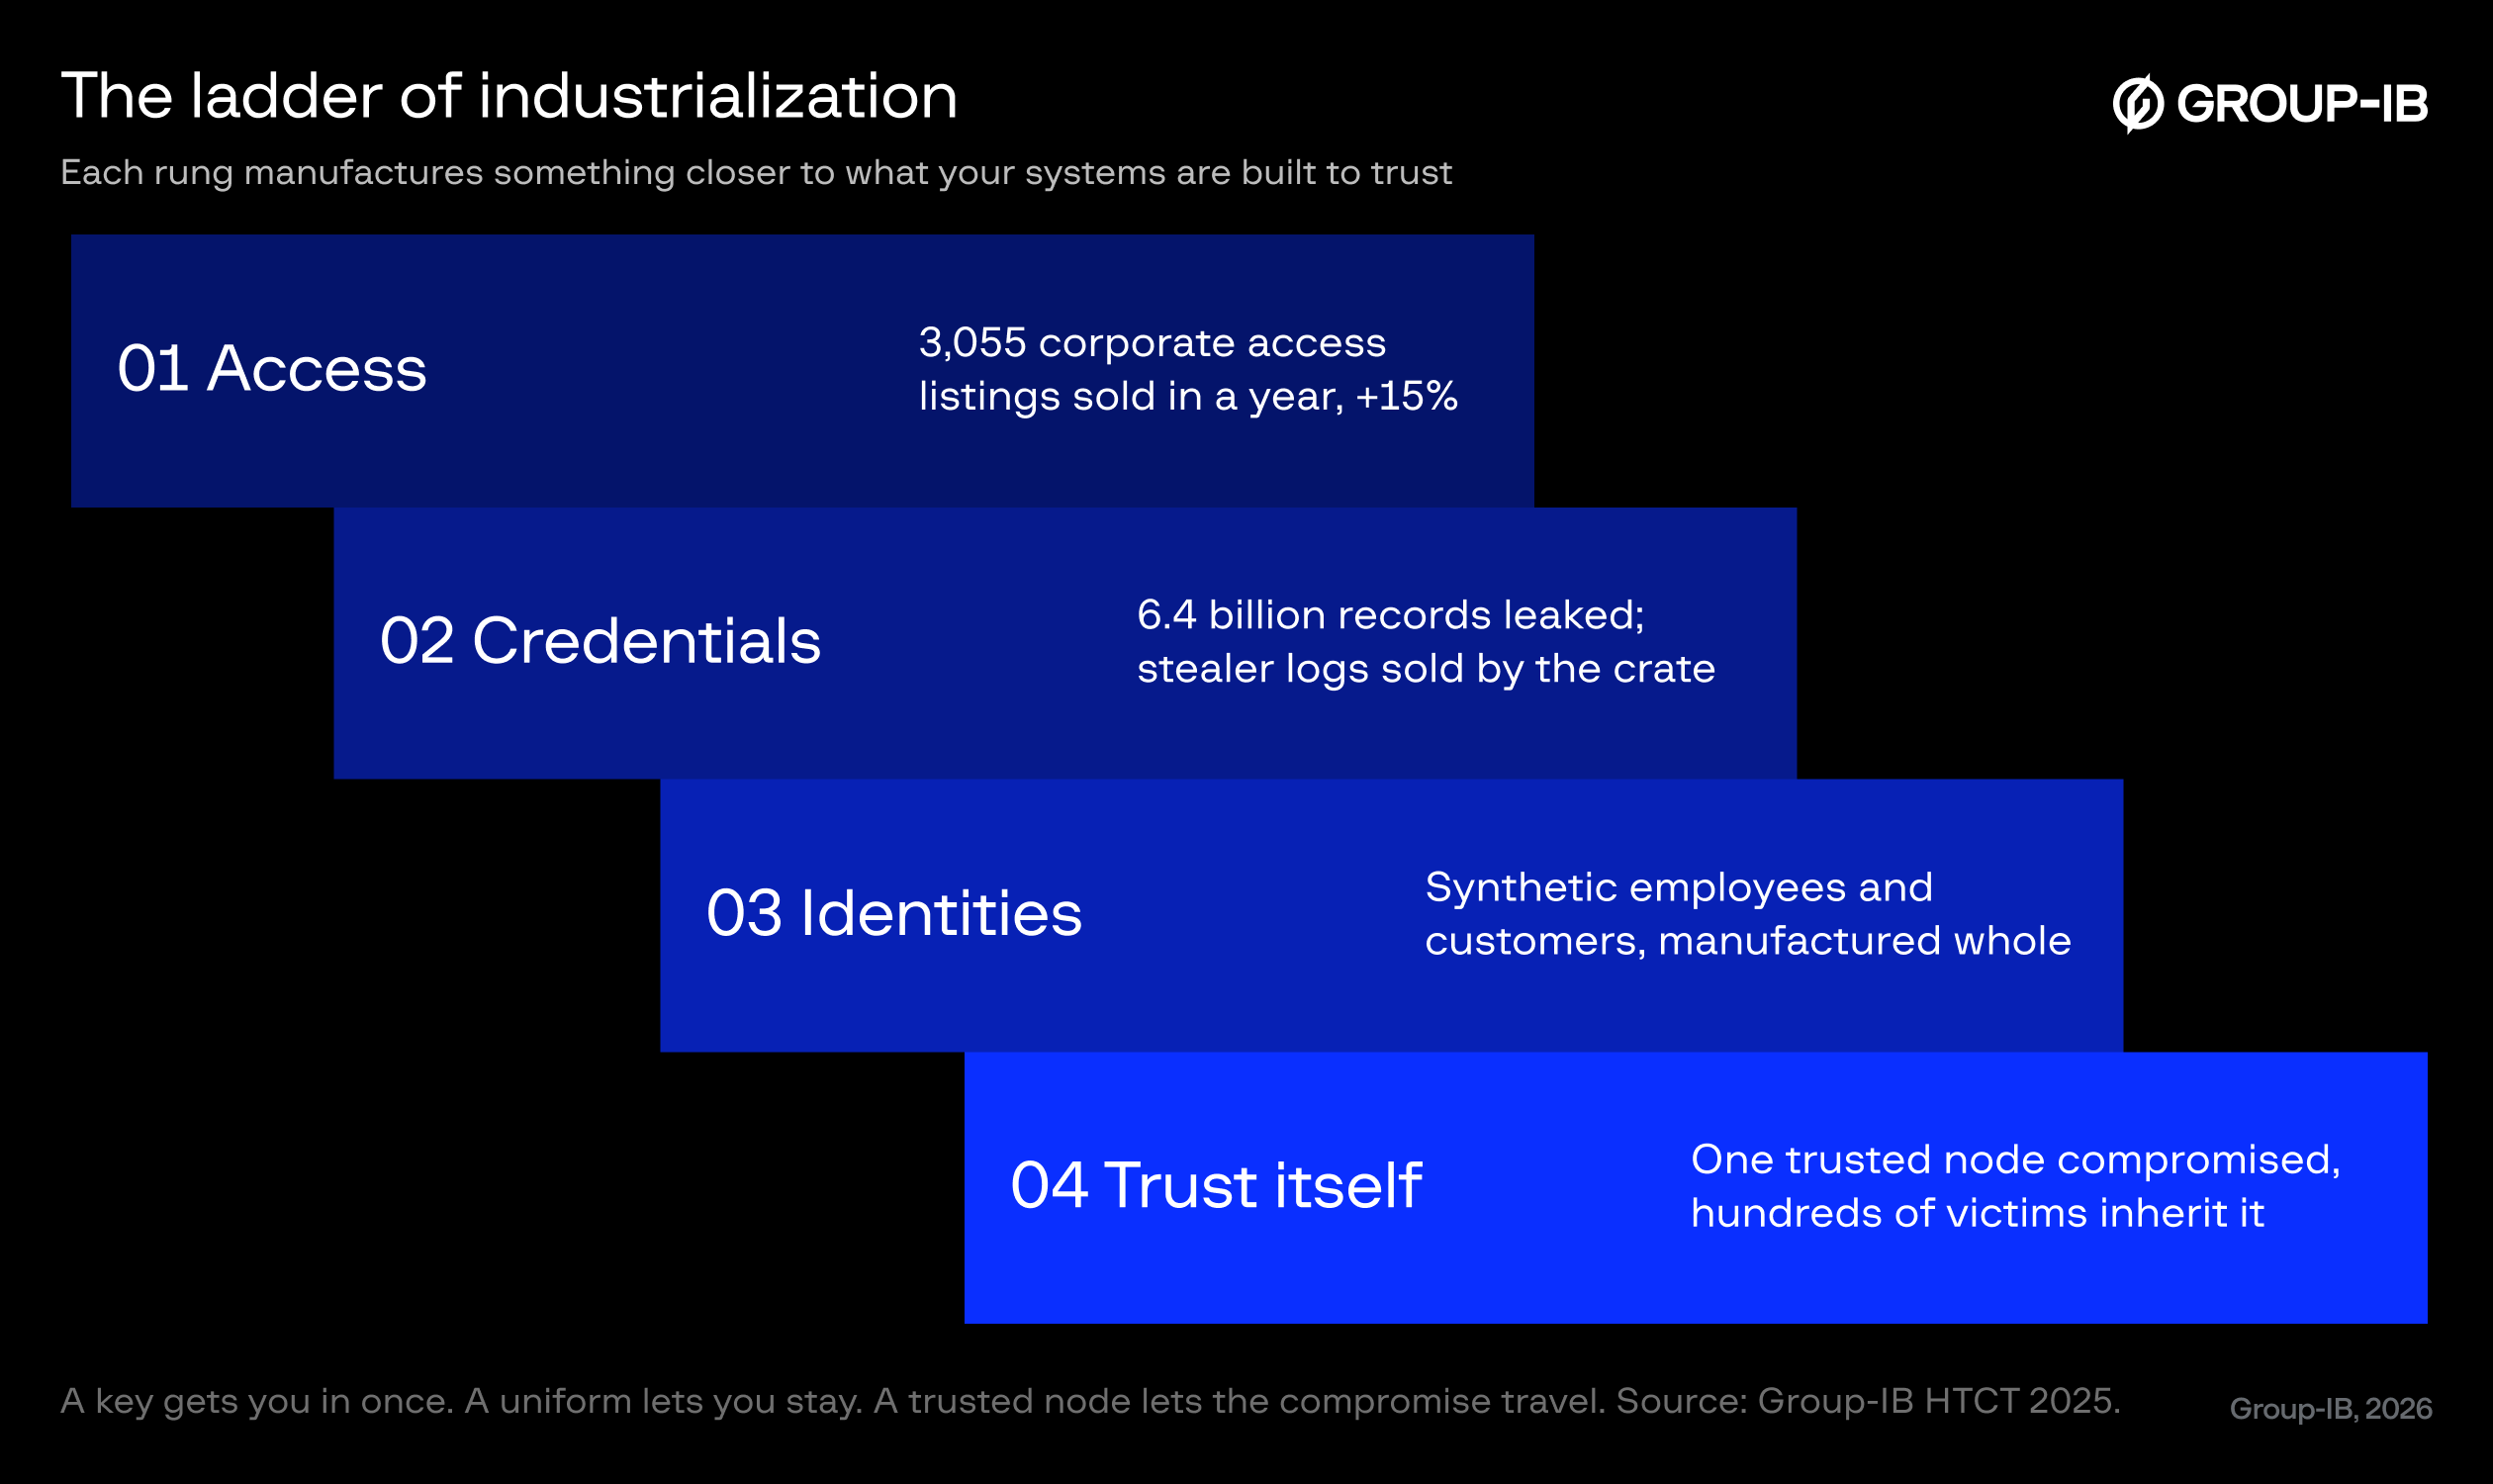
The gap is the argument for Cyber Fraud Fusion. Group-IB’s Before Fraud Transacts paper puts the fraud side plainly: fraud is not an event at the moment of payment, it is a campaign that begins weeks earlier.
So map the full kill chain and intercept where prevention is still possible, which is the Group-IB Fraud Matrix, aligned with the MITRE Fight Fraud Framework. Share indicators across institutions in real time, without exposing customer data, so the mule network invisible inside one bank is unmistakable across forty, which is the Cyber Fraud Intelligence Platform (CFIP): Group-IB provides the technology, and the consortium of participating banks runs the network between them.
The question of any fraud control stops being what it catches, and becomes how early it warns. The posture that results is predictive rather than reactive: acting on the campaign while it is being staged, not on the transaction after it clears.
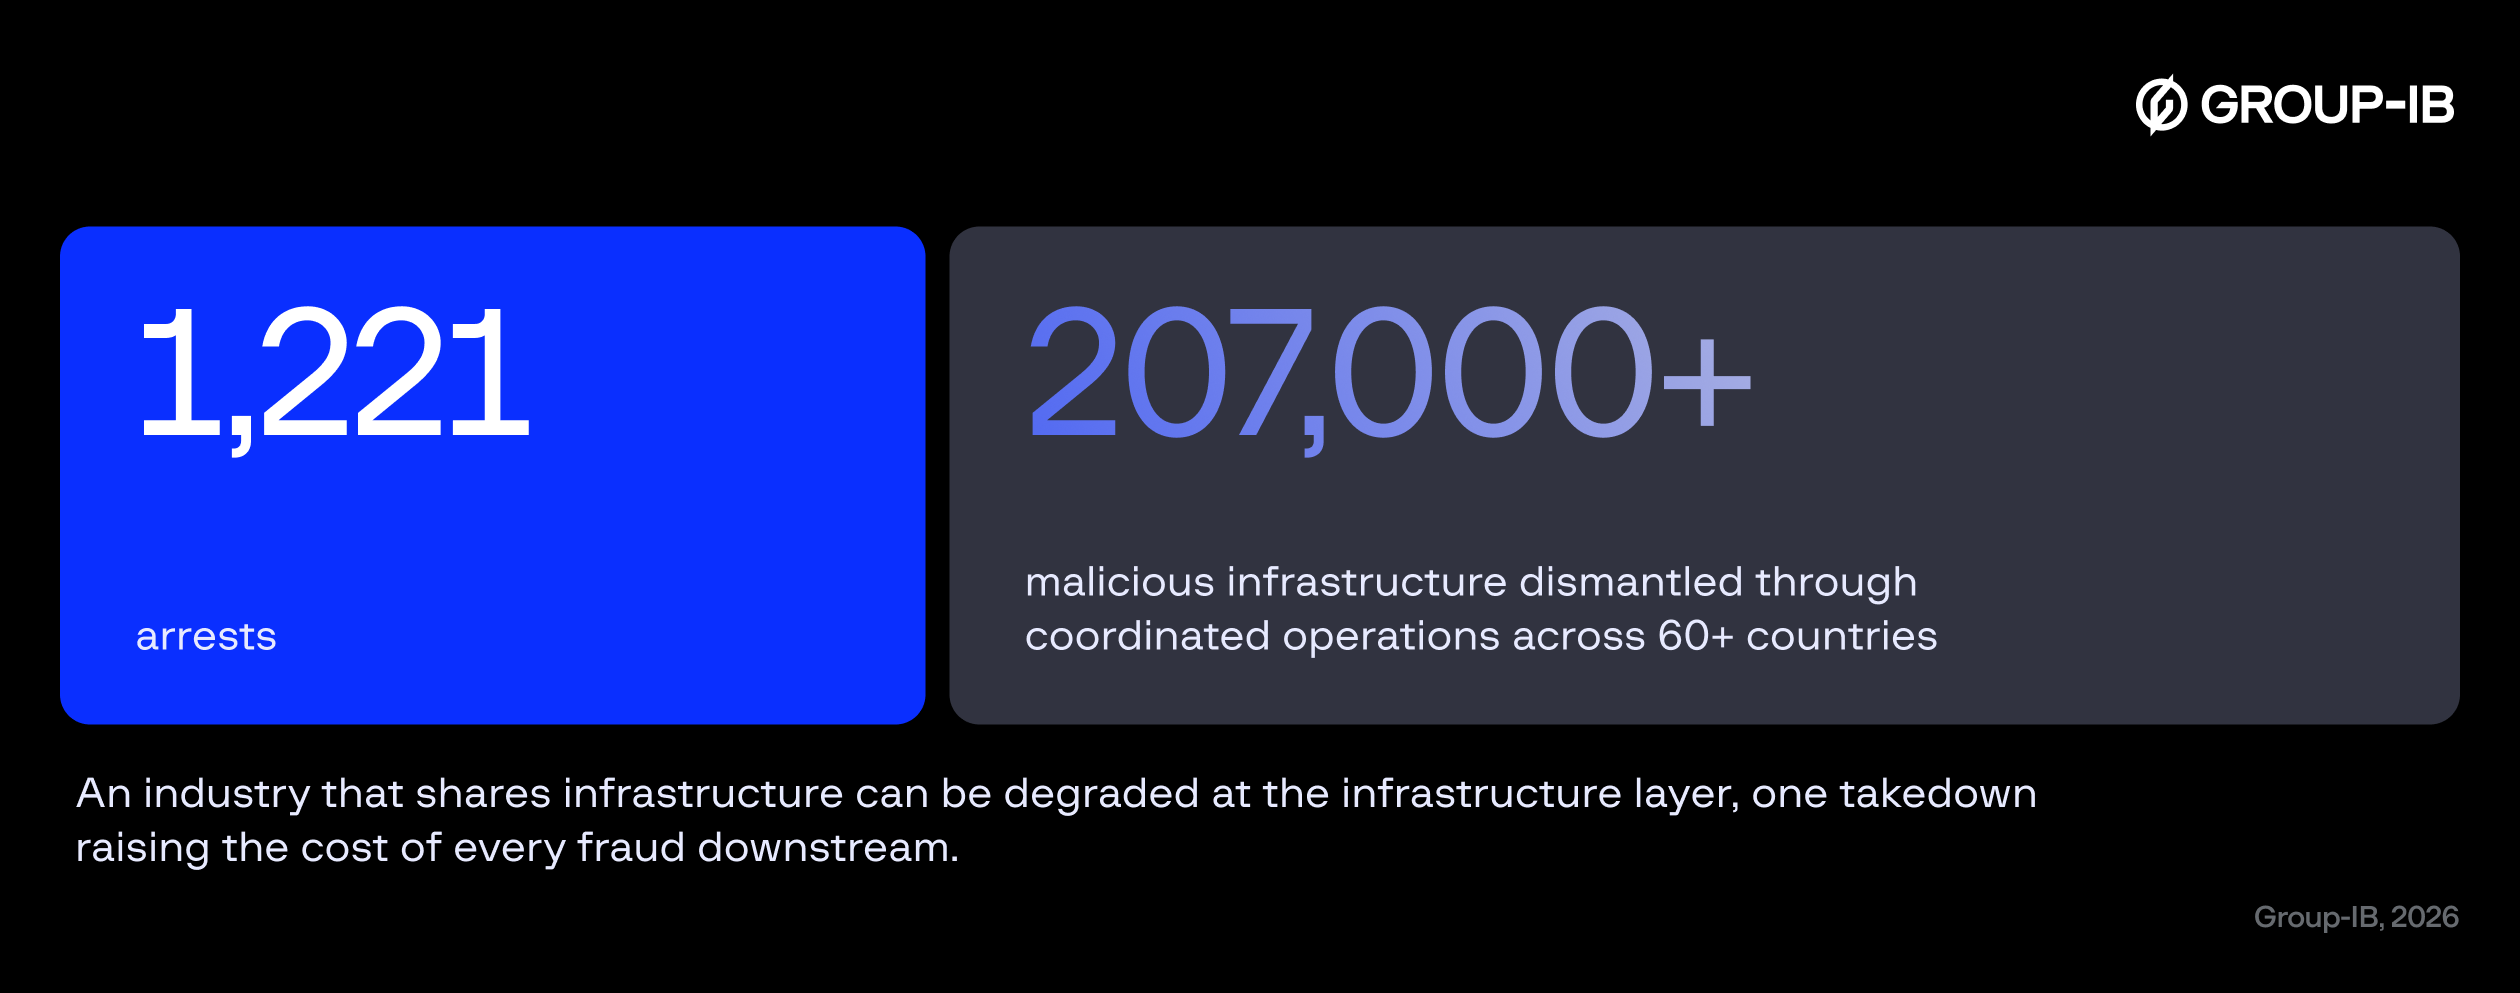
Adversary economics is the only metric this market responds to, and no institution moves it alone. The criminals stopped attacking companies one at a time. The question is how long defenders keep defending that way?
The winners will not use the most advanced AI. They will advance towards fused, predictive intelligence
Cybercrime is a specialized, outsourced, data rich economy where identity is the product, trust is the exploit, and AI is the efficiency layer across every stage. The developer builds, the broker sells, the affiliate is recruited, the reservoir of stolen data supplies the raw material, and the trusted relationship delivers the reach. No single actor does the whole thing, which is why you will not arrest your way out of it.
So the plan for next year writes itself. Every institution is about to buy AI, so the model itself will be table stakes, not an edge. The edge is the data underneath it. The winners will not deploy the most advanced model, they will fuse the data it reads: cyber and fraud, internal and external, and the indicators shared by other institutions, read as one picture across the network.
Stop organizing the defense around attack types and organize it around what every pattern here exploits, identity and trust. Assume credentials are already stolen. Assume your trusted third parties are a way in. Invest there first.
Speed is the reason this cannot wait for detection. When execution collapses to fifteen minutes, reacting to an attack means arriving after it, and a defense that waits for the transaction has already lost it. The industrialized chain takes weeks to stage and stays visible the whole time, so the position that works is not faster response but prediction: pre-execution visibility, the campaign disrupted before it ever transacts.
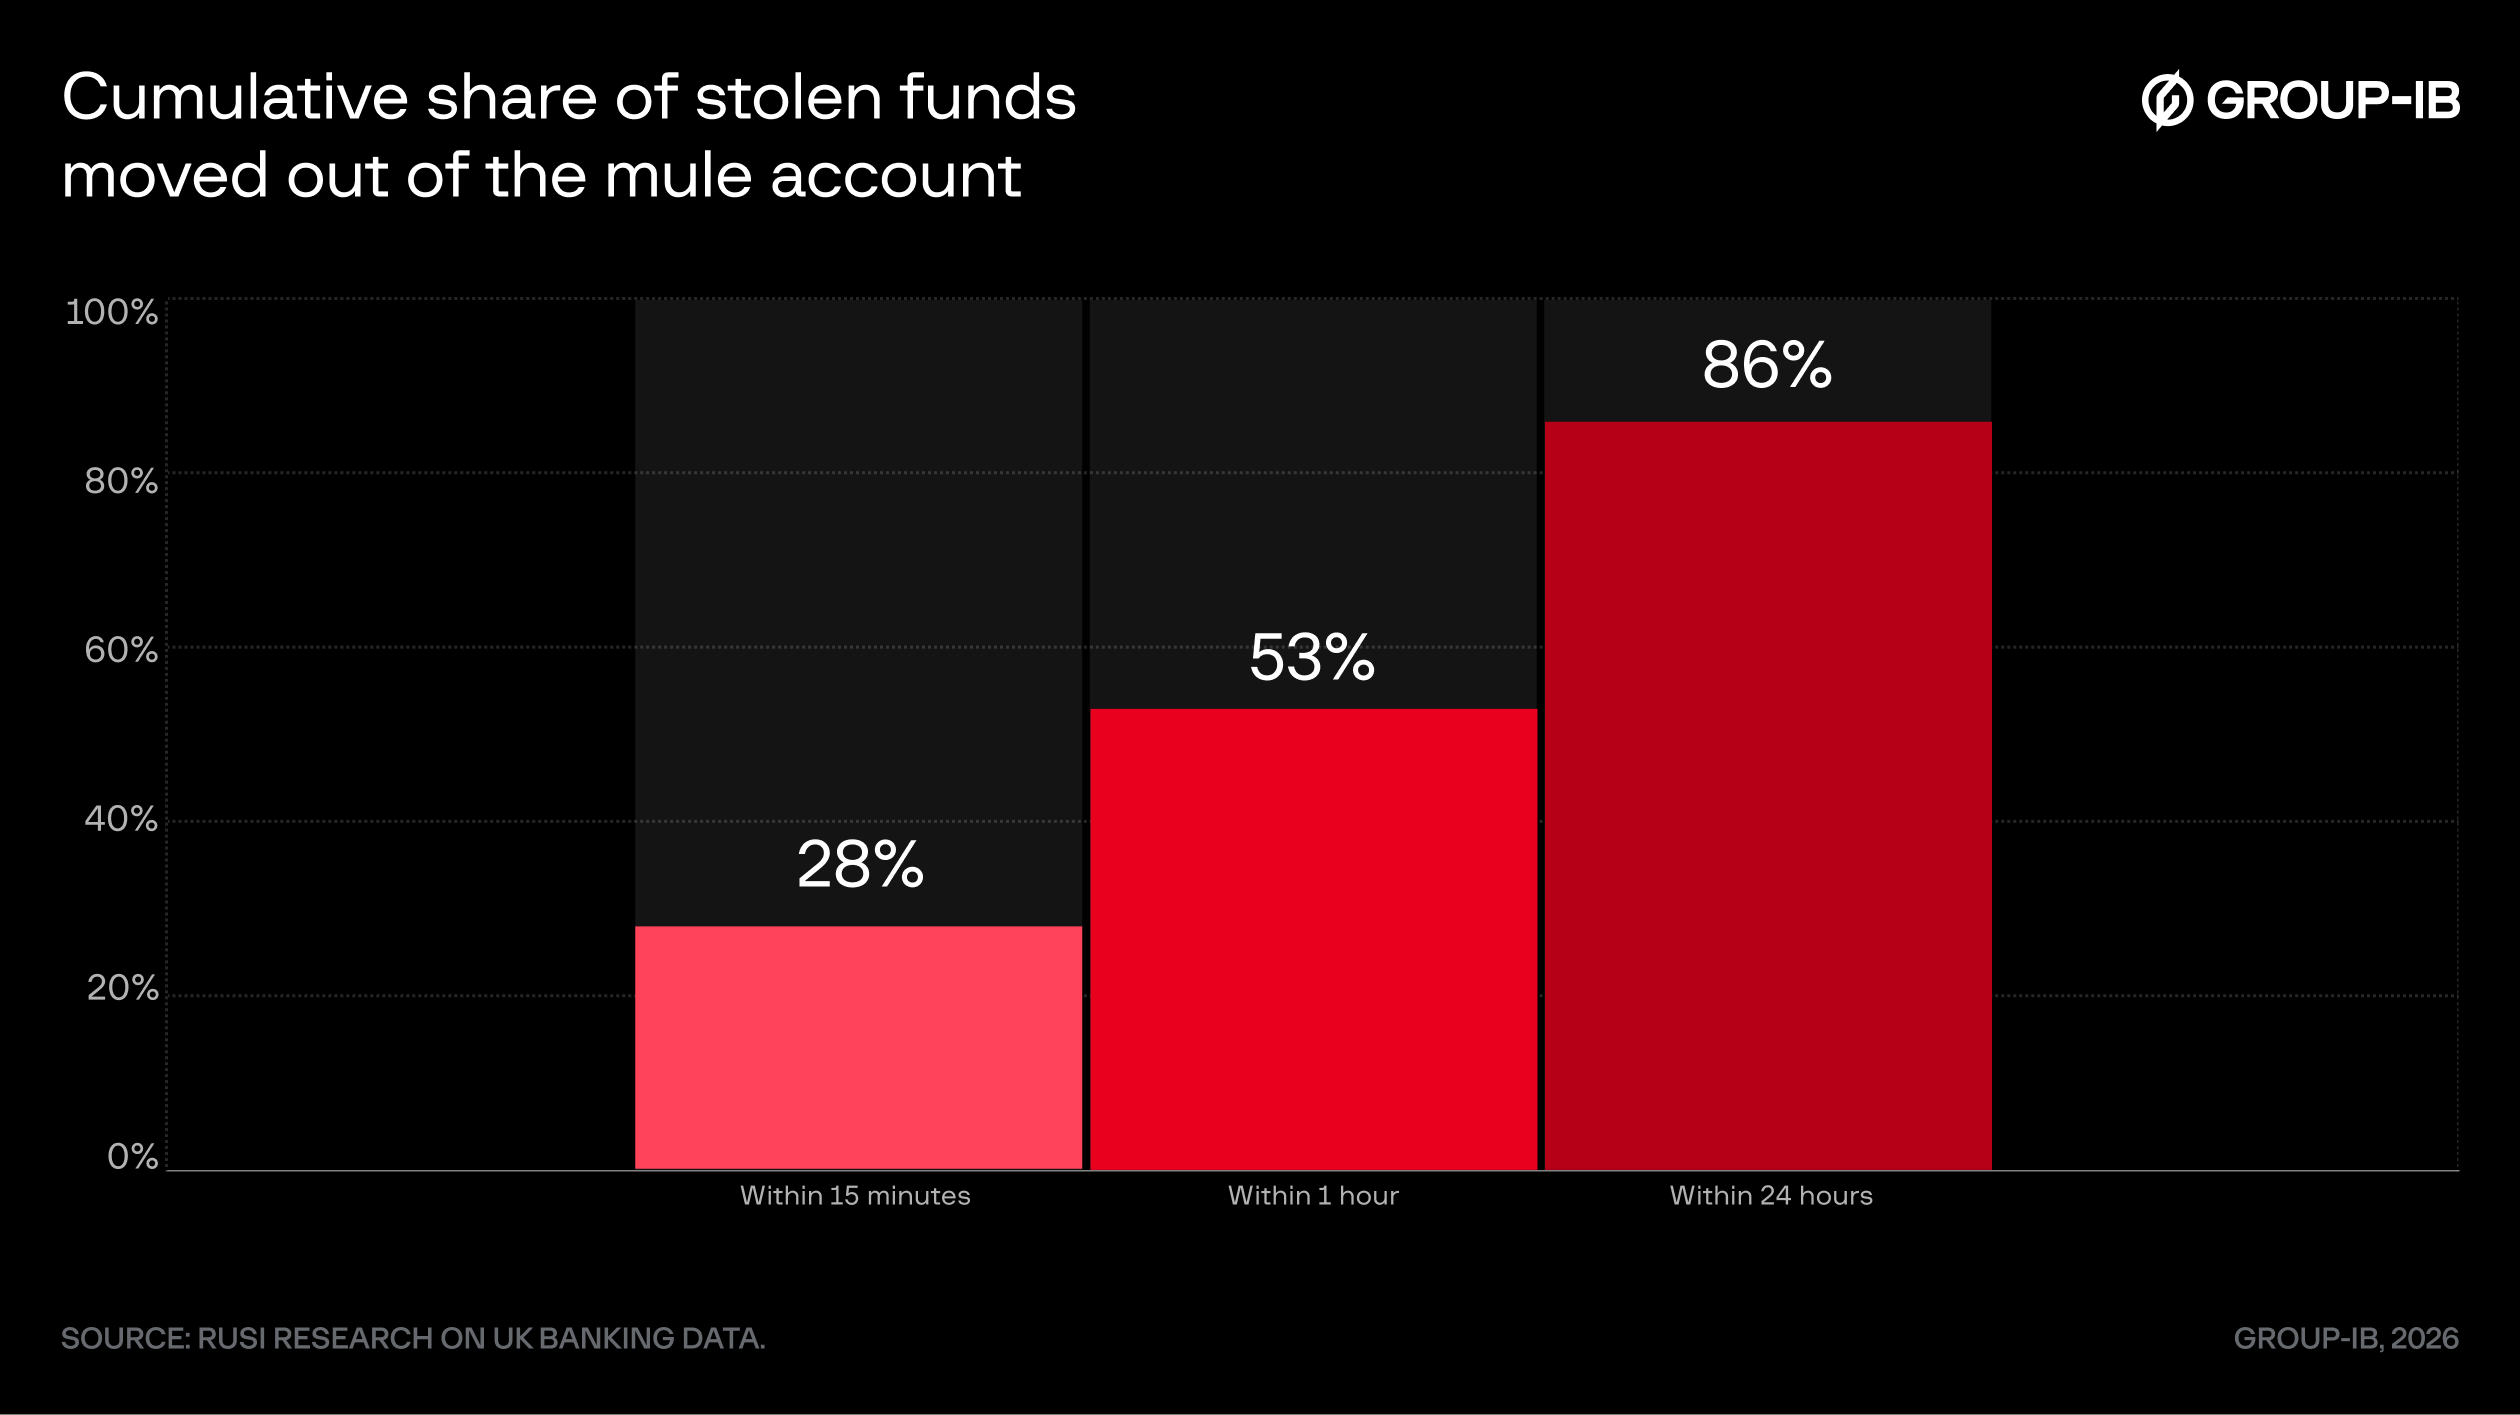
Cumulative share of stolen funds moved out of the mule account. Source: RUSI research on UK banking data.
Two moves put a defender there. First, merged visibility: a mule warm up that means nothing to one fraud desk becomes an early signal read against the credential theft the security team logged three weeks earlier, and the metric it moves is signal to action time, days when the two halves are separate, minutes when they are fused. The second is agentic AI inside the operations centre, pointed at that fused picture and acting on those indicators of attack at machine speed. Group-IB runs this as Prevyn AI, launched in 2026 as the reasoning layer of its Unified Risk Platform. In threat intelligence it works in agentic mode, coordinating twelve specialized agents modelled on Group-IB’s own high-tech crime investigations, malware profiles threat actors, dark web data lake, to help analysts with remediation workflows, response actions and alert investigation.