Report an incident
Get 24/7 incident response assistance from our global team
- APAC: +65 3159 4398
- EU & NA: +31 20 890 55 59
- MEA: +971 4 540 6400
- LATAM: +56 2 275 473 79
Get 24/7 incident response assistance from our global team

Your guide to AI innovation, adoption, and acceleration in cybersecurity
Modern fraud isn't an event. It's an industrialised campaign that begins weeks before the payment. The transaction is where fraud ends, not where it happens. This paper shows how to disrupt the campaign weeks before the payment, not document it after.
Your guide to AI innovation, adoption, and acceleration in cybersecurity
Learn more


Perform full-cycle investigations in Windows environments by mastering forensic evidence collection, artifact analysis, and intelligence-driven investigation workflows.
Enhance digital forensics expertise through hands-on analysis of NTFS metafiles, registry artifacts,system files, application data, malicious files, and volatile memory.
Strengthen the ability to identify, preserve, and analyze evidence of malicious activity by applying advanced forensic techniques, and memory forensics methods.

Ahmed has been working in the Security Operations Center over the last three years, transitioning his expertise from penetration testing to Digital Forensics and Incident Response and regularly takes part in complex incident response operations.
Ahmed has conducted numerous training sessions, molding the new age cybersecurity professionals. His expertise doesn’t just stop at identifying digital threats but extends to fostering a culture of continuous learning and curiosity among aspiring cyber experts.

Moataz carries over three years of specialized cybersecurity expertise, particularly in the realm of red teaming and penetration testing, where he has honed his skills in identifying and mitigating vulnerabilities within various systems and networks. Moataz has led several training sessions, playing a pivotal role in shaping and developing the next generation of cybersecurity professionals helping them navigate the landscape of modern cyber threats.
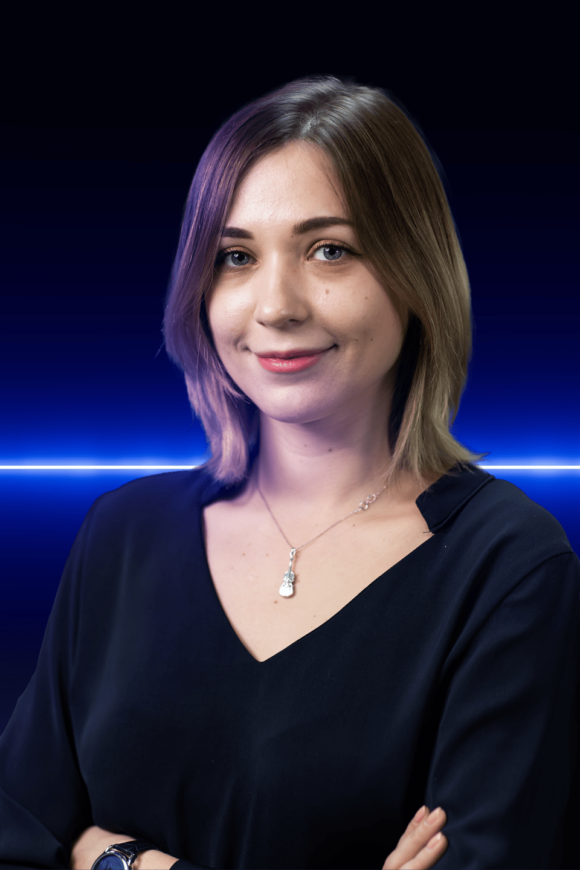
With a background in incident response and digital forensics, Svetlana has designed many DFIR training programs and crisis management masterclasses. She has also co-authored articles and books on cybersecurity, such as Practical Memory Forensics, Incident Response for Windows, and the e-guide Human-Centric Assessments. She has trained specialists in more than 30 countries and spoken at leading conferences worldwide, from FS-ISAC Japan to GITEX UAE.
Nam has over 13 years of experience in cybersecurity and specializes in digital forensics and incident response. At Group-IB, he investigates advanced cyber threats and supports organizations during complex security incidents, including ransomware attacks and post-compromise activity in enterprise and critical infrastructure environments.
Nam is a contributor to the MITRE ATT&CK® framework and has published technical research on advanced threat actor techniques, including ransomware operations and Linux-based evasion methods.