Report an incident
Get 24/7 incident response assistance from our global team
- APAC: +65 3159 4398
- EU & NA: +31 20 890 55 59
- MEA: +971 4 540 6400
- LATAM: +56 2 275 473 79
Get 24/7 incident response assistance from our global team

Your guide to AI innovation, adoption, and acceleration in cybersecurity
Modern fraud isn't an event. It's an industrialised campaign that begins weeks before the payment. The transaction is where fraud ends, not where it happens. This paper shows how to disrupt the campaign weeks before the payment, not document it after.
Your guide to AI innovation, adoption, and acceleration in cybersecurity
Learn more


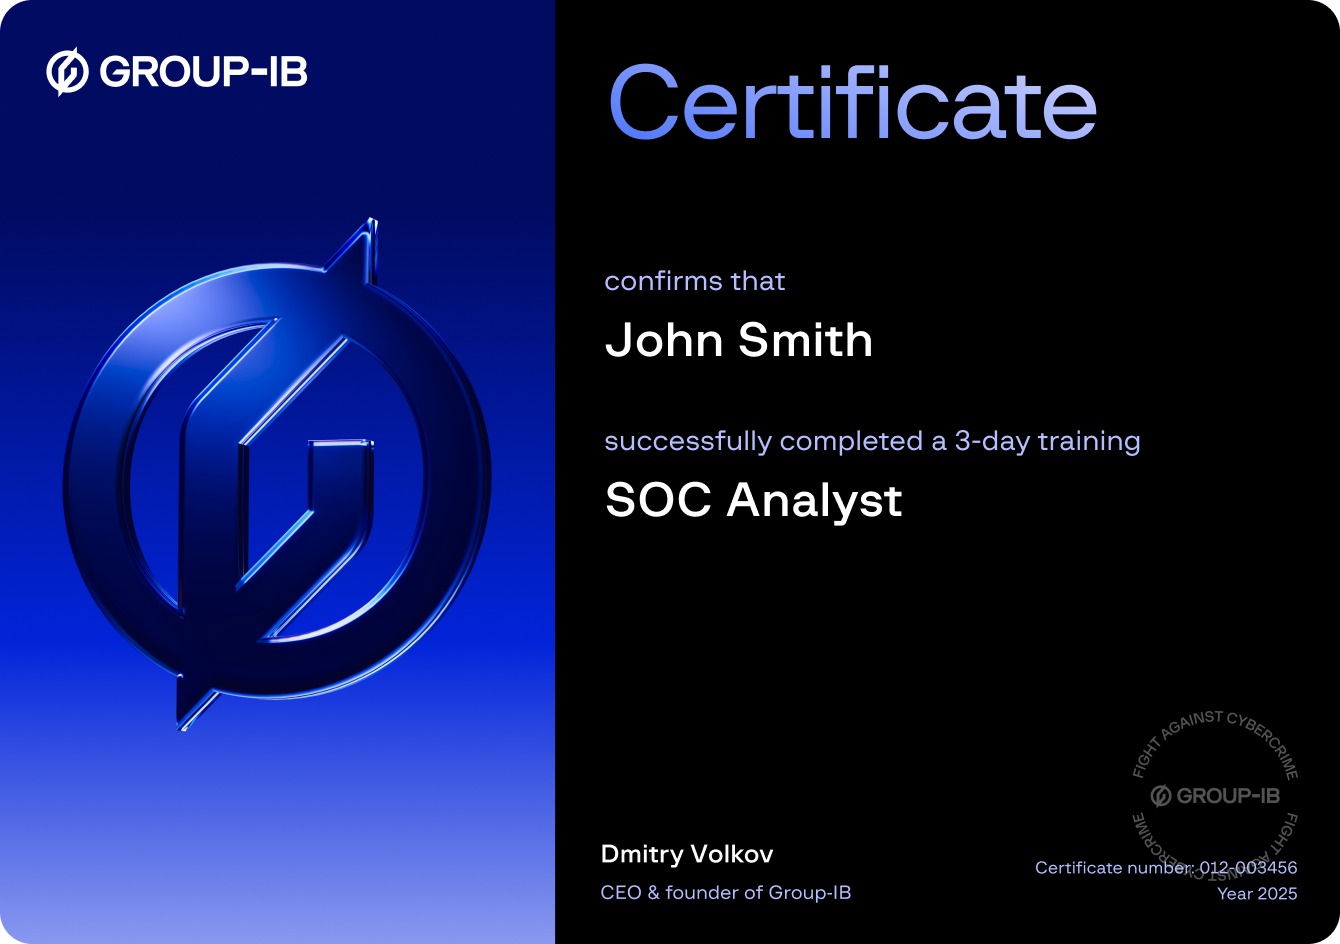
Gain in-depth knowledge of Security Operations Center objectives and core technologies, focusing on tools for advanced threat detection, log-based threat analysis, and the identification of threat indicators.
Develop a comprehensive understanding of cyberattack methodologies and common attack vectors while building practical expertise in endpoint monitoring and analysis.
Strengthen incident response capabilities by mastering the interpretation of Windows event logs, analyzing system behavior, and applying knowledge to effective threat detection and remediation workflows.

Acquire practical proficiency in network traffic analysis and packet capture tools to identify complex threats, correlate network-level evidence, and fortify organizational infrastructure against evolving attack vectors.
Ahmed has been working in Security Operations Center over the last three years, transitioning his expertise from penetration testing to Digital Forensics and Incident Response and regularly takes part in complex incident response operations. Ahmed has conducted numerous training sessions, molding the new age cybersecurity professionals. His expertise doesn’t just stop at identifying digital threats, but extends to fostering a culture of continuous learning and curiosity among aspiring cyber experts.
Moataz carries over three years of specialized cybersecurity expertise, particularly in the realm of red teaming and penetration testing, where he has honed his skills in identifying and mitigating vulnerabilities within various systems and networks. Moataz has led several training sessions, playing a pivotal role in shaping and developing the next generation of cybersecurity professionals helping them navigate the landscape of modern cyber threats.