Report an incident
Get 24/7 incident response assistance from our global team
- APAC: +65 3159 4398
- EU & NA: +31 20 890 55 59
- MEA: +971 4 540 6400
- LATAM: +56 2 275 473 79
Get 24/7 incident response assistance from our global team

Your guide to AI innovation, adoption, and acceleration in cybersecurity
Modern fraud isn't an event. It's an industrialised campaign that begins weeks before the payment. The transaction is where fraud ends, not where it happens. This paper shows how to disrupt the campaign weeks before the payment, not document it after.
Your guide to AI innovation, adoption, and acceleration in cybersecurity
Learn more


Investigate security incidents involving Linux infrastructure by collecting forensic data, analyzing system artifacts, and identifying traces of malicious activity in *nix environments.
Strengthen Linux forensic analysis skills by working with file systems, metadata, timestamps, forensic images, and memory acquisition techniques.
Enhance the ability to investigate attacks on Linux systems through structured evidence collection, memory analysis, and examination of key artifacts and in-memory filesystems.

Ahmed has been working in the Security Operations Center over the last three years, transitioning his expertise from penetration testing to Digital Forensics and Incident Response and regularly takes part in complex incident response operations.
Ahmed has conducted numerous training sessions, molding the new age cybersecurity professionals. His expertise doesn’t just stop at identifying digital threats but extends to fostering a culture of continuous learning and curiosity among aspiring cyber experts.
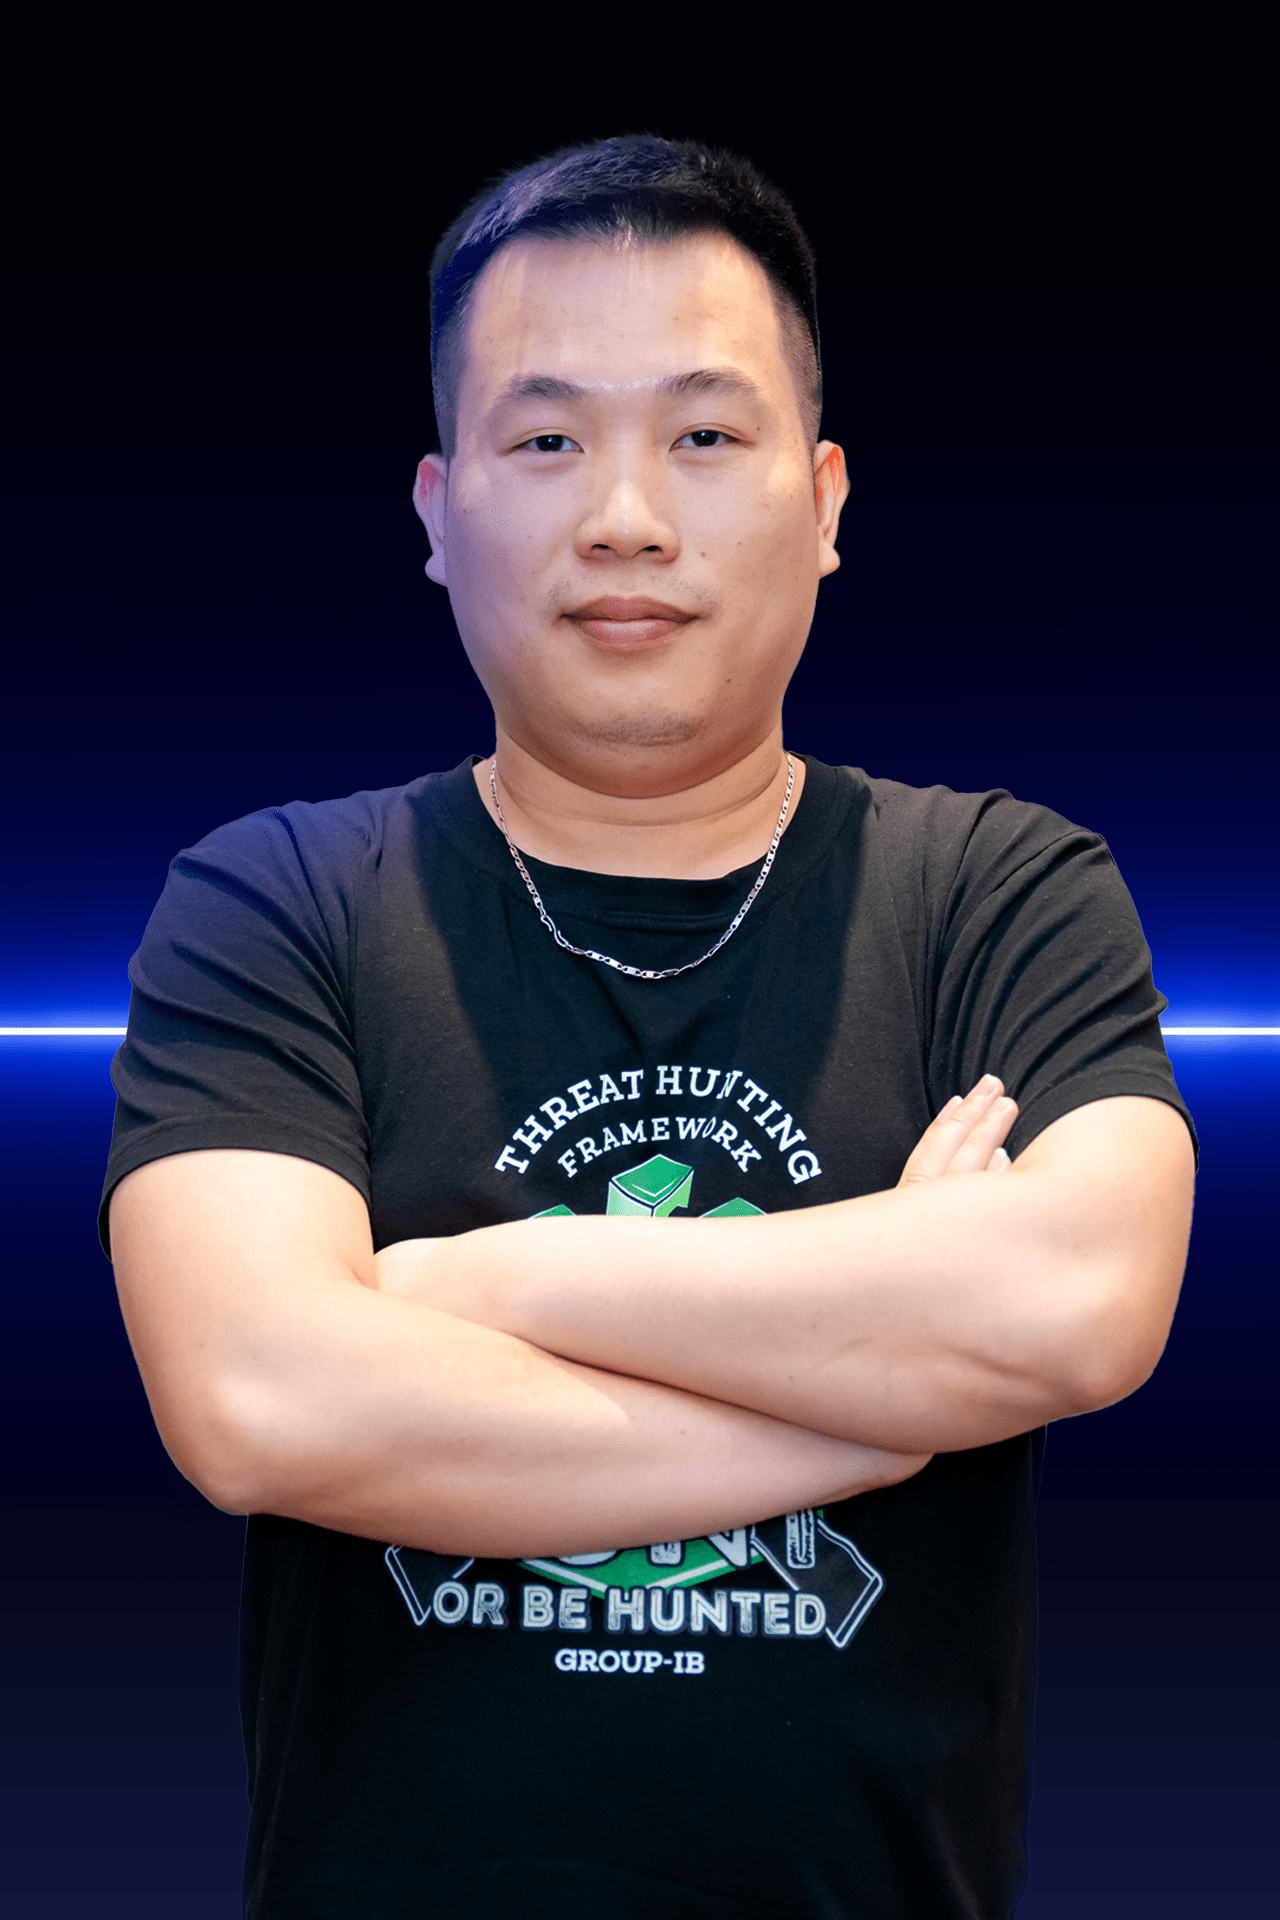
Nam has over 13 years of experience in cybersecurity and specializes in digital forensics and incident response. At Group-IB, he investigates advanced cyber threats and supports organizations during complex security incidents, including ransomware attacks and post-compromise activity in enterprise and critical infrastructure environments.
Nam is a contributor to the MITRE ATT&CK® framework and has published technical research on advanced threat actor techniques, including ransomware operations and Linux-based evasion methods.