Report an incident
Get 24/7 incident response assistance from our global team
- APAC: +65 3159 4398
- EU & NA: +31 20 890 55 59
- MEA: +971 4 540 6400
- LATAM: +56 2 275 473 79
Get 24/7 incident response assistance from our global team







Your guide to AI innovation, adoption, and acceleration in cybersecurity

Modern fraud isn't an event. It's an industrialised campaign that begins weeks before the payment. The transaction is where fraud ends, not where it happens. This paper shows how to disrupt the campaign weeks before the payment, not document it after.
Your guide to AI innovation, adoption, and acceleration in cybersecurity
Learn more
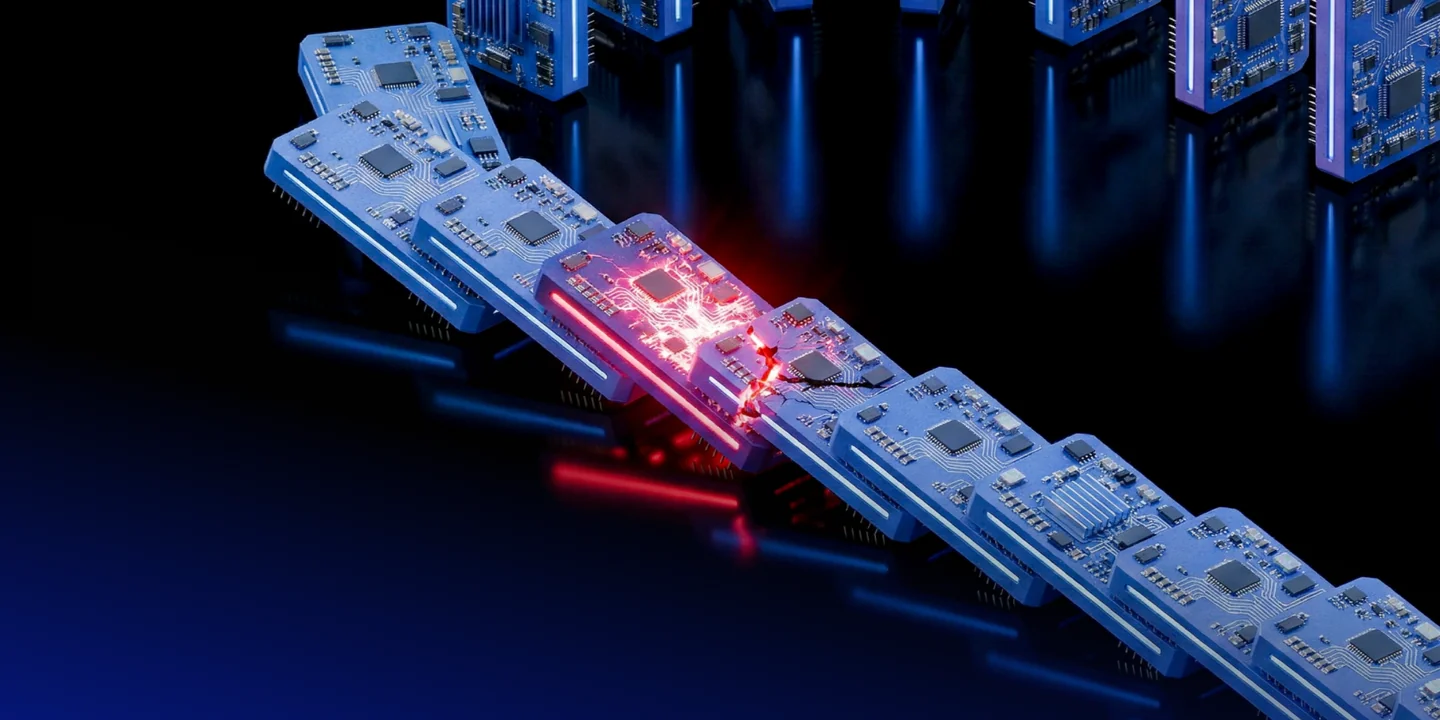
Supply chain attacks have become the defining force in today’s cyber threat landscape. Rather than targeting organizations directly, attackers exploit trusted vendors, SaaS platforms, open-source dependencies, and OAuth integrations to gain inherited access that silently spreads across entire ecosystems. What appear to be isolated incidents like phishing, ransomware, data breaches, malware are increasingly interconnected stages of a single supply chain-driven attack model. Stolen tokens, API keys, and service accounts enable threat actors to move laterally across trusted environments while blending in as legitimate users.
In this webinar, we’ll cover
Join us to understand how to break the domino effect before it spreads.The same webinar is also available in German.
Subscribe to stay up to date with the latest cyber threat trends