





Introduction
Between March and September 2026, thousands of Android phones belonging to retail banking customers in the META region were confirmed to be infected with the malware Group-IB tracks as Mirax, with two big activity spikes observed over the Eid holidays and at the end of July.

Figure 1. Mirax RAT samples installation over time (based on Group-IB telemetry).
Where unauthorized international transfers were reported, funds were sent to accounts abroad, some of which are suspected to be mule accounts. Based on reported cases, we estimate losses in the millions of US dollars. These numbers account for only what Group-IB analysts can confirm, through our own telemetry and confirmed cases reported by affected banks in the region. The real figure is likely higher, from infections on devices we have no visibility into, and bank customers who never reported a loss.
The campaign uses dynamically generated package names and impersonates “Google Play Services” to evade user suspicion and signature-based detection. The number of infected devices exceeds the number of identified samples, consistent with sample reuse and distribution across multiple victims. This campaign is still observed to be running at the time of publication.

Figure 2. Android malware campaign statistical summary.
The bait appears to be simple: a free video streaming app on the Google Play Store. Users who frequently download low-reputation streaming apps expect very little, and this one delivered exactly that — advertisements, video links, and not much else. It looked, and largely behaved, like any other low-effort streaming app. But evidence suggests that the ad banners served inside it lead users to a dropper, downloaded outside the official store which installs the Mirax malware payload.
Mirax is classified as an Android Device Take-Over (DTO) family of malware. Its key permission: the Accessibility Service. With it, the attacker is able to see and control the compromised device in real time: reading credentials, intercepting one-time codes, capturing the PIN to unlock the device later, opening a banking app and moving money out to newly added beneficiaries and mule accounts abroad. From the bank’s side, little looks unusual; the activity and transactions come from the customer’s own device, app, and from the expected location.
The lure is actually the least interesting part; malicious ads served inside shady streaming apps is nothing new. What matters begins after installation. Mirax ships deliberately light on incriminating code and configuration. Its C2 infrastructure, ports, TLS parameters, DNS-over-HTTPS behavior, polling intervals, and even the phishing and HTML-injection templates tailored to individual banking apps are all fetched from the attacker’s C2 server at runtime. The hardcoded C2 address in the sample is a rendezvous point and nothing more. While the capabilities ship in the app, how they are configured, what they are aimed at, and how the device reaches its operator are all settled afterwards.
This report walks through how Mirax reaches victims, how it earns the permissions it needs, what its infrastructure looks like under the hood, and what defenders can do about it.
Key Discoveries
- Malicious ads served inside low-reputation free streaming apps that lead to a dropper.
- The payload impersonates “Google Play Services,” substituting a Cyrillic “о” for the Latin letter, and actively coerces victims into granting Accessibility Service access – the single permission that unlocks full remote control.
- Build identity is deliberately disposable: package names are randomized per build, the launcher icon is hidden at runtime, so no drawer entry exists, and the campaign rotates app names to stay ahead of takedown and detection.
- Command-and-control runs a dual-WebSocket design over a single host with an HTTP long-poll fallback; nearly every transport parameter is remotely reconfigurable, and DNS-over-HTTPS keeps C2 resolution off local and carrier DNS entirely.
- Phishing content is never shipped in the APK – HTML injection templates and their target-app mappings are pushed from C2 at runtime, meaning static analysis of the installed sample reveals only a fraction of the campaign’s real capability.
- A region-specific campaign, identified by its build tag: the samples in this report all carry the embedded build tag aquafina, which links them to a single operation across more than one C2 host. The applications the C2 pushes for targeting are predominantly regional: 20+ META banks and digital wallets.
Who may find this blog interesting
- Fraud and mobile threat analysts at financial institutions
- Malware researchers and reverse engineers covering Android threats
- Threat intelligence teams tracking Device Take-Over families
- Digital risk / app-store abuse teams
- Incident response and SOC teams at targeted banks
Group-IB Threat Intelligence and Fraud Intelligence Portals:
Group-IB customers can access our Threat Intelligence and Fraud Intelligence portals for more information about the threat actor and malware described in this blog.
- Threat Intelligence Portal: Aquafina
- Threat Intelligence Portal: Mirax
- Fraud Intelligence Portal: Mirax Bot


Anatomy of the Infection
From streaming app to drained accounts, Mirax’s infection chain is built to look unremarkable at every step:
- Delivery: The victim installs a low-reputation streaming/video-player app from Google Play. Evidence suggests that the ad banners and video links it serves, lead to a dropper downloaded outside the official store. There is no suspicious link in an SMS: the starting point is an app from an official store doing what streaming apps do: serving ads.
- The Dropper: The installed app quietly retrieves and installs Mirax’s second-stage payload, the component that actually carries out the takeover. A confirmed dropper observed in the course of this research presents itself as an adult version of TikTok named “Tiktok 18+1; it is not affiliated with TikTok.

Figure 3. Detected NSFW lure dropper using the label TikTok 18+.
Impersonation and permission coercion: The payload presents itself as “Google Play Services” – down to the Cyrillic homoglyph in its name – and requests a broad set of permissions, most critically Accessibility Service. On-device automation actively steers the victim toward granting Accessibility access, rather than simply hoping they click through.

Figure 4. “Google Play Services” Interface prompts displayed to targets leading to Accessibility Service authorization.
- Takeover: Once accessibility is granted, the operator has a real-time, interactive view of the device: SMS and notification interception, screen monitoring, and screen-sharing/remote-control abuse.
- Fraud execution: With this live access, the operator can open the victim’s own banking session and drive it directly, initiating transactions that appear, from the bank’s perspective, to originate from the legitimate device and app.
- Persistence: Accessibility Services privileges make the app harder to remove through normal means, extending the operator’s window.
- Monetization and laundering: Evidence to date indicates several potential channels used to monetize and move the fraudulent proceeds, including the addition of a beneficiary for international transfers, internal transfers between accounts, and eShop purchases on online marketplaces. The available evidence suggests that mule accounts may have been used to facilitate the movement and laundering of funds in India. Further tracing of transaction destinations and beneficiary accounts is ongoing by Group-IB to establish the full flow of funds.
-
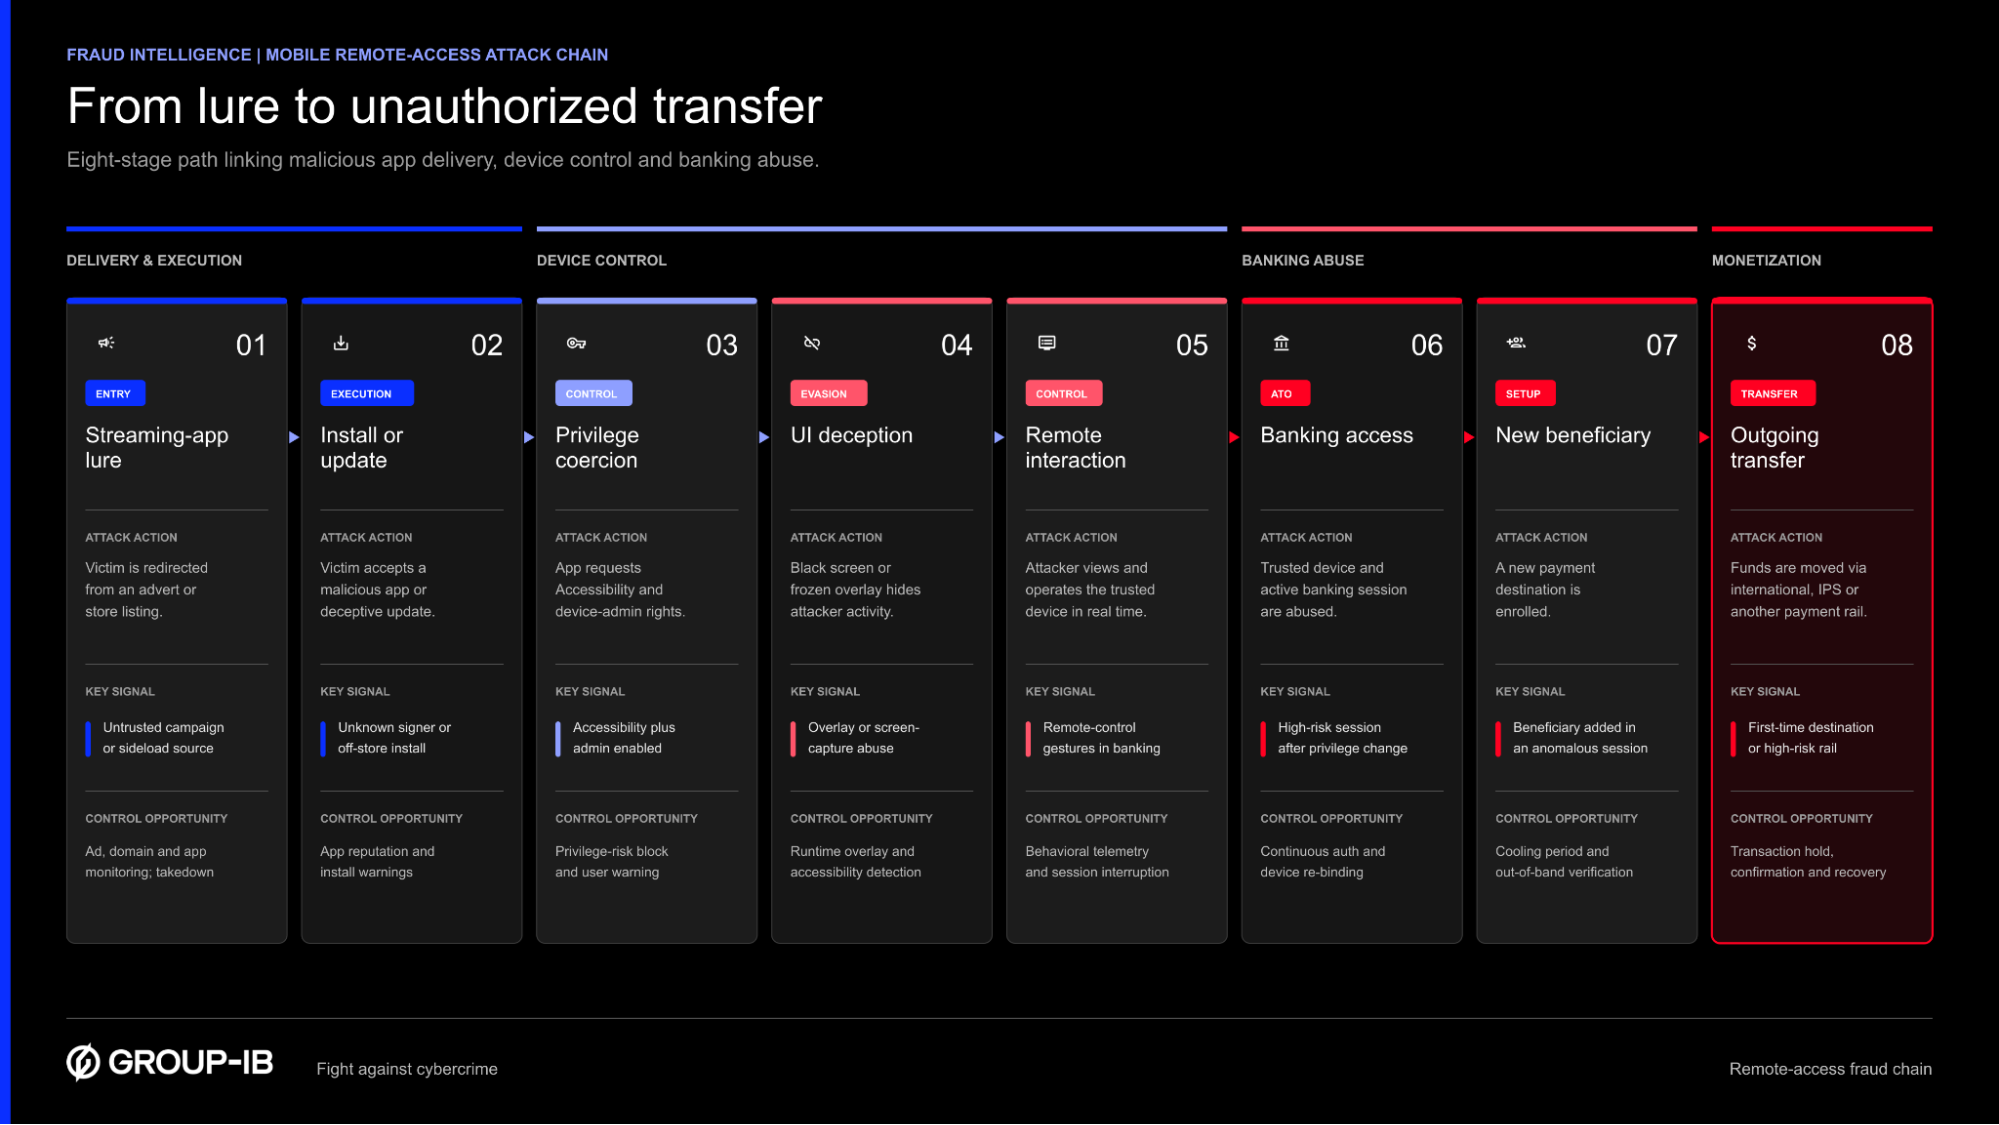
Figure 5. Mirax attack chain scheme.
Why Mirax is Hard to Pin Down
Under the hood, two design choices set Mirax apart from more static regional DTO families.
The first is identity fluidity. The manifest package name is randomized per build, launcher aliases are toggled at runtime so the app never shows a drawer icon, and the campaign rotates the visible app name over time. None of this requires a new build pipeline each time – it’s designed to be cheap to repeat.
The second, and more consequential, is server-side capability. Mirax’s C2 runs a dual-WebSocket architecture on a single host with an HTTP long-poll fallback, and effectively every transport parameter – host, both ports, TLS, DNS-over-HTTPS, polling intervals – can be reconfigured remotely. DNS-over-HTTPS is enabled by default, which keeps C2 resolution invisible to local and carrier-level DNS monitoring. The phishing and HTML-injection templates used to target specific banking apps aren’t in the APK at all; they, along with their app-to-template mappings, are pushed from C2 after install.
The practical effect is that inspecting the installed sample – even thoroughly – only shows what Mirax could do at the moment of install, not what it’s actually configured to do in the field. This visibility gap is the campaign’s real advantage.

Built for Control: Inside the Mirax Platform
- Private MaaS, not a commodity: Mirax is an Android remote access trojan and banking malware observed to be sold on Russian-language cybercrime forums since December 2025 by a developer using the handle MiraxBot. According to the developer’s forum advertisements, access is reserved only for vetted affiliates, with priority given to established Russian-speaking actors.
- A full device-takeover platform: Beyond credential theft, Mirax offers HTML overlay injection against banking, crypto, email and social apps; keylogging; SMS and notification interception for OTP theft; and hidden VNC / screen-sharing for real-time interactive control of the device.
- Autonomous device unlock: Mirax captures the victim’s lock-screen secret (PIN, password or pattern), and can replay it to unlock the device unattended, letting the operator act while the victim isn’t watching.
- Residential proxy built in: A February 2026 update added a SOCKS5 module that turns each infected phone into a residential proxy node, letting operators route fraudulent traffic through the victim’s own IP address to defeat geolocation and IP-reputation checks.
- The app ships the capabilities, not the targets: Overlay templates and their target-app mappings are not shipped in the APK. They are pushed from the C2 per device, based on what the victim has installed. Two infections of the same malware can therefore be configured to attack entirely different institutions.
- Persistence and self-preservation: Mirax maintains persistence through Android Broadcast Receivers, re-establishing itself after reboots and app restarts. On top of that it actively resists removal: it blocks the user from reaching its uninstall screen, can block security and antivirus apps from launching, and uses full-screen black overlays (including a fake “updating” screen) to hide malicious activity while it runs.
- Command-and-control: The C2 runs over dual WebSocket channels, one for commands, one for data exfiltration. Newer builds add DNS-over-HTTPS and an HTTP long-poll fallback, and almost every transport parameter is remotely reconfigurable. The operator drives the device through a broad command set. The full list of observed C2 commands is provided in the Appendix.
- Built to support affiliates: Mirax ships as a ready-to-run operation: a builder with selectable packers, a web panel for managing multiple infected devices, and a steady stream of updates from the developer. Every build is also stamped with a campaign identifier – build tag, that the payload reports back to its C2.

Figure 6. Banking overlay example.
The Aquafina Campaign
The samples behind the activity described in this report all carry the same build tag: aquafina (and its variant aquafina_all). This single identifier led Group-IB researchers to treat these infections as one coherent campaign rather than unrelated sightings. The same tag was observed reporting to more than one C2 host, so even where the infrastructure differs, the samples trace back to a common operation. The tag string itself says nothing about who is being targeted; that comes from the C2’s own response. When the discovered samples checked in with the C2, the server returned the list of applications it wanted monitored and pushed a matching set of banking overlays. The target set of 20+ packages contains retail banks and digital wallets from the META region, alongside a couple of global cryptocurrency exchanges. In other words, aquafina is not a generic Mirax deployment that happened to reach the META region; it is a campaign configured specifically for it.
Impact
Mirax’s activity intensified sharply during the Eid holiday period and, as of this investigation, remains ongoing. At the time of writing, streaming apps assessed as potential vectors for the malicious ads remained available on Google Play, and the operators continued rotating application names to stay ahead of takedown. Victims are retail banking customers reached indirectly through a general-purpose entertainment app rather than a banking-themed lure, which is precisely what makes the initial install unremarkable. Multiple victims across the region have reported unauthorized transactions and missing funds. Preliminary data indicates approximately thousands of affected bank accounts on the Android channel across several financial institutions, with reported unauthorized international outgoing transfers initiated from infected victim devices and routed to mule accounts in India. Set against the confirmed infection count, that puts the estimated losses in the millions — a floor rather than a total, since it captures only fraud that was detected and disputed.
Because the phishing templates and target-app mappings are server-controlled rather than fixed at build time, the campaign can pivot toward other banking apps, industries, or regions without a new release – a spread vector worth monitoring closely.
Detection
Group-IB Fraud Protection’s coverage of Mirax leans on behavioral signals rather than static signatures alone, in line with how little the installed sample actually reveals on its own. Detection focuses on Accessibility Service abuse patterns, remote-control and screen-sharing session activity, and network/C2 behavior consistent with the dual-WebSocket and DoH design described above. Fraud-monitoring rules that flag screen-sharing or remote-control indicators alongside an active transaction attempt are the primary trigger for escalation and review before funds move.

Figure 7. Active remote access alert detection on the infected victim device with Mirax RAT sample.
Group-IB Fraud Protection generated alerts shortly after Mirax malware sample was installed on victim devices with admin and Accessibility Service permissions were granted (Figure 8).

Figure 8. Post-installation alerts on infected devices indicating potential DTO ( Device Takeover).
Group-IB solutions constantly monitor new android malware threats and update existing detection mechanisms and IOCs databases.

Figure 9. Example of session with Mirax infected device detection.
Conclusion
Mirax fits a pattern Group-IB has tracked across several regional campaigns this year: attackers investing less in the installed APK and more in what the server can do after the fact. A thin, disposable client – randomized package, hidden icon, rotating name – paired with a fully server-controlled attack surface means that app-store review and victim awareness, on their own, are less effective defenses than they used to be. Mirax and similar threats are likely to keep reappearing under new names, including via lures distributed through official app stores, timed around high-traffic periods like religious holidays, and to keep leaning on Accessibility Service as the one permission that matters. The takeaway for defenders: any detection strategy anchored solely to the installed sample is likely to remain a step behind a campaign whose real capability lives on a server it controls.
Recommendations
To limit exposure to Mirax and similar Device Take-Over campaigns, we recommend the following layered measures, mapped to where they take effect in the chain.
For Businesses
- Fraud Protection: Add confirmed-affected devices to an enhanced monitoring list; treat fraud-alert triggers accompanied by screen-sharing or remote-control indicators as high-priority escalations, and hold transactions pending customer verification where such indicators are present.
- Threat Intelligence: Keep certificate, package, and C2 infrastructure indicators current as the campaign rotates identifiers, and monitor for signs of the phishing template set expanding to new targets.
- Reach out directly to users of confirmed-affected devices to help identify and remove the malicious app, using approved mobile security tools where needed for remediation.
- Where permitted by applicable law and contractual obligations, share indicators and campaign patterns with other institutions and app-store abuse teams, given the potential for this delivery method to spread to other industries or regions.
For End-Users
- Be cautious with ads, video pop-ups, and redirect banners on unpopular or untrusted streaming apps and sites – this is Mirax’s primary vector.
- Treat any request for Accessibility Service access from an app that isn’t a genuine accessibility tool as a red flag, especially from an app impersonating “Google Play Services.”
- If a streaming or entertainment app requests Accessibility permissions, decline and uninstall.
Acknowledgement of research support:
- Pavel Naumov, Global Senior Security Researcher FHP
- Yuan Huang, Global Fraud Intelligence Lead
Group-IB Fraud Matrix

MITRE ATT&CK® Scheme

MITRE ATT&CK® for Mobile

Indicators of Compromise (IOCs)
File Indicators
| name | sha1 | installed |
| net.wgrjvz.toolyt93a | b9e84889c9760460f53c9b49cb43a636bb721d28 | Aug 6, 2026 |
| org.xrmhvlfx.litewnj3h | 8531fe2db41e9e08525080be6d3e8092c5ffa5f8 | Jul 31, 2026 |
| net.jsbzchba.clientpnzd | 0d83344fee8973165e5009768c1752095a57f3c1 | Jul 28, 2026 |
| org.xifbep.utilityt50 | 3a1f9060dad56cd08e87fcafa2c87b99295b3db3 | Aug 4, 2026 |
| io.svmlmt.mobilecu7sq | 6a37c3d4beb80ae1689dbbedcb53a86f85c8e44a | Jul 8, 2026 |
| io.xccqt.helper3mk | fd4a2c02ab5a99b5420538c8b1bfef6fa4fbd7fe | Aug 6, 2026 |
| io.vvecxa.clientffb | 2b5eeabbc52a25172123c2e7789c977e6bb557af | Jun 29, 2026 |
| io.crxti.systems11f | d7b4d33c38deb0978b71ef79ff4df9fb90118cc2 | Aug 2, 2026 |
| org.lfzfxjmb.securejp65 | 746dc75b1b887812db37b3801e104d887b2c8707 | Aug 5, 2026 |
| net.yexqoe.systemlshkq | c9258f527fe447431ff983aa76866e340db98e60 | Aug 5, 2026 |
| net.mfiaekme.toolgdqvu | ace41996dc5b7ecdb68c2222fc7af8e6f3b7d839 | Aug 6, 2026 |
| org.fxutpep.utility0ql | 9e6889b1445e30d9d28849cbffed5a3123408646 | Aug 4, 2026 |
| net.rhnrektl.mobilejrs | cca7187d5cbf31b3e785f21309bb60b9247a4fb4 | Aug 5, 2026 |
| io.isvac.safemmz7g | 562d8360854005e90ae316c1350b9660ffd3e6f9 | Aug 1, 2026 |
| com.zjper.litewens | da997eeb64a3879af819c5cdda3aa5a236c55a25 | Jul 31, 2026 |
| org.pruvqil.appq1km | 413e1c8661ec11fc8e7f9a7caccfc9c54cb1ea3d | Aug 1, 2026 |
| net.vsqomby.toolc4s1x | c8f5abb80e9c936d6bd5da99c10e829cde69a8f5 | Aug 1, 2026 |
| org.yhjrihi.managerrk9u6 | 20068b91036145b3e1b1d7e294b7a2f5ba26bd7f | Aug 1, 2026 |
| io.nmflf.pro4d2ll | b164a1bf2c7b478ce040e479377526c00885ab7f | Aug 5, 2026 |
Network Indicators
- oscofneuid[.]com
- kenobuias[.]com
Appendix
Full Inventory of Mirax C2 Commands
| Command | Description |
| addExternalHtmlTemplate | Pushes a new HTML overlay template to the device |
| addHtmlInjectionConfig | Binds a target package name to an overlay template |
| back | Simulates pressing the Back button |
| blackScreen | Activates a full-screen black overlay |
| blackScreen_unlock | Removes the black screen overlay |
| blackScreen_updating | Shows a fake “updating” message on the black overlay |
| blockApp | Prevents a specific application from being launched |
| camera_status | Returns current camera service status |
| checkExternalTemplateExists | Checks whether a named template is stored locally |
| collectSmsNow | Triggers an immediate SMS upload |
| disableHtmlInjection | Disables the overlay injection system |
| disableNeverSleep | Restores normal screen timeout behavior |
| disableUninstallProtection | Disables anti-uninstall protection |
| enableHtmlInjection | Enables the overlay injection system |
| enableNeverSleep | Forces the screen to stay on indefinitely |
| enableUninstallProtection | Blocks uninstallation of the malware |
| forceReconnect | Forces reconnection to the C2 server |
| getAvailableCameras | Lists all available camera sensors |
| getBlockedApps | Returns the list of currently blocked applications |
| getCameraStatus | Returns camera service status |
| getClipboard | Retrieves current clipboard contents |
| getDeviceState | Returns device metadata (battery, network, OS, model) |
| getExternalTemplatesList | Lists overlay templates stored on device |
| getExternalTemplatesPath | Returns the storage path for overlay templates |
| getHtmlInjectionStatus | Returns the current state of the overlay engine |
| getHtmlTemplates | Lists all locally available overlay templates |
| getInstalledApps | Returns a full inventory of installed applications |
| getKeyguardInfo | Returns lock screen configuration details |
| getLockStatus | Returns the current lock screen type and status |
| getPermissions | Returns status of all Android permissions |
| getSmsPermissions | Returns SMS permission status |
| getSmsStatus | Returns SMS collection engine status |
| getVncScreenSharingStatus | Returns VNC session status |
| home | Simulates pressing the Home button |
| layout_updates_restart | Restarts screen layout monitoring |
| layout_updates_start | Begins streaming screen layout data to C2 |
| layout_updates_stop | Stops screen layout data streaming |
| listCameras | Lists available cameras |
| lockDevice | Locks the device screen immediately |
| mute | Mutes device audio |
| openApp | Launches an application by package name |
| ping | Heartbeat / keepalive |
| recents | Simulates pressing the Recent Apps button |
| removeExternalHtmlTemplate | Deletes a named overlay template from device |
| removeHtmlInjectionConfig | Removes a target application’s overlay binding |
| requestPermission | Triggers a system permission request dialog |
| rescanHtmlTemplates | Rescans storage for updated overlay templates |
| resetHtmlInjectionCounters | Resets overlay injection counters |
| resetLockCaptured | Resets the lock screen capture state |
| setClipboard | Sets clipboard content to operator-supplied text |
| setLockType | Configures the fake lock screen type (PIN/pattern/password) |
| showNotification | Displays a notification (STANDARD / OVERLAY / TOAST modes) |
| socks5_enable | Enables or disables the SOCKS5 proxy relay |
| socks5_status_request | Returns SOCKS5 proxy status |
| startCamera | Starts background camera capture |
| startScreenSharing | Starts screen capture streaming to C2 |
| startSmsCollection | Starts continuous SMS interception |
| startVncScreenSharing | Starts interactive VNC session |
| stopAllScreenSharing | Stops all active screen sharing sessions |
| stopCamera | Stops camera capture |
| stopScreenSharing | Stops standard screen sharing |
| stopSmsCollection | Stops SMS interception |
| stopVncScreenSharing | Stops VNC session |
| swipe | Performs a swipe gesture between two coordinates |
| switchClient | Switches active client session |
| tap | Performs a tap gesture at specified coordinates |
| testHtmlInjection | Manually triggers an overlay for a specified package |
| text | Types text via accessibility input |
| unblockApp | Unblocks a previously blocked application |
| uninstallPackage | Uninstalls a specified application |
| unlockDevice | Unlocks the device using captured credentials |
| updateAppRecordingConfig | Updates the list of targeted apps monitored for recording |
| updateExternalHtmlTemplate | Updates an existing overlay template on device |
| wakeDevice | Wakes the device screen from sleep |
Disclaimer
Third-party trademarks. All product names, logos and brands referenced in this publication are the property of their respective owners. They are used solely for identification and descriptive purposes in the context of security research, and their use does not imply any affiliation with, or endorsement by, their owners. Screenshots of fraudulent resources are reproduced to document the impersonation of legitimate brands and services; the brands depicted are victims of that impersonation.
1 “TikTok 18+” is a fraudulent imitation created by threat actors to deceive victims. This application is not an official product of ByteDance, nor is it affiliated with, endorsed by or connected to the official TikTok brand in any way.
© 2026 The MITRE Corporation. This work is reproduced and distributed with the permission of The MITRE Corporation. The MITRE ATT&CK content is used subject to the MITRE ATT&CK Terms of Use. MITRE ATT&CK® and ATT&CK® are registered trademarks of The MITRE Corporation. This publication is independently produced and is not affiliated with, sponsored by, or endorsed by The MITRE Corporation.
Third-party service providers. Certain indicators reference lawful hosting, serverless and API providers whose services were abused by the operators without their knowledge or involvement. No wrongdoing on their part is alleged or implied.
No legal advice. This publication is provided for information and defensive purposes only and does not constitute legal advice. Statements concerning the possible legal position of any party are general in nature; readers should obtain advice from a qualified adviser in the relevant jurisdiction.
Assessments and attribution. All assessments, attributions and confidence levels stated in this publication reflect the information available to Group-IB as at the date of publication and may change as further information becomes available. Where conduct is attributed to accounts, channels or groups, Group-IB makes no assertion as to the identity of any individual behind them beyond what is expressly stated.


